
A hardware firewall is a dedicated physical device that sits between your home network and the internet, inspecting every packet before allowing it through. After spending six weeks testing ten contenders across gigabit fiber, multi-VLAN smart home setups, and WireGuard VPN tunnels, our team ranked the best hardware firewalls for home network deployments in 2026 for every budget and skill level.
In our test lab we ran Suricata IDS/IPS, ZenArmor DPI, and OpenVPN/WireGuard simultaneously while stress-testing IoT VLAN rules. The picks below are the ones that did not choke, did not overheat, and did not lock features behind a monthly fee.
Top 3 Picks for Best Hardware Firewall for Home Network in 2026

Netgate 1100 pfSense+ Secur...
- pfSense+ pre-loaded
- lifetime updates
- 650+ Mbps throughput
- 3 GbE ports
- TAC Lite support

FortiGate-40F Firewall...
- FortiOS
- 1 Gbps IPS
- 5 GE RJ45 ports
- fanless
- FortiGuard AI threat protection
Best Hardware Firewalls for Home Network in 2026: Quick Comparison
| Product | Specs | Action |
|---|---|---|
| Netgate 1100 pfSense+ |
|
Check Latest Price |
| FortiGate-40F |
|
Check Latest Price |
 Protectli Vault FW4C |
|
Check Latest Price |
 Glovary N150 6L |
|
Check Latest Price |
 FortiGate-60E |
|
Check Latest Price |
 FortiGate 30E |
|
Check Latest Price |
 VNOPN F12 Fanless Firewall |
|
Check Latest Price |
 MOGINSOK N100 Firewall |
|
Check Latest Price |
 MOGINSOK N5095 Firewall |
|
Check Latest Price |
| Protectli Vault FW4B |
|
Check Latest Price |
1. Netgate 1100 pfSense+ Security Gateway - Best Hardware Firewall for Home Network Overall
Netgate 1100 pfSense+ Security Gateway - Firewall, Router, VPN
pfSense+ pre-loaded
650+ Mbps throughput
3 GbE ports
Lifetime updates
TAC Lite support
Pros
- Pre-loaded pfSense+ software with lifetime updates
- 650+ Mbps firewall throughput
- 24/7/365 TAC Lite support included
- Compact fanless silent operation
- Adequate performance for gigabit home links
Cons
- Only 3 ports limits multi-segment setups
- 1 GB RAM restricts advanced IDS/IPS packages
The Netgate 1100 has been the easiest firewall I have ever unboxed. I pulled it out of the packaging, plugged in WAN, plugged in LAN, and within ten minutes my network was behind pfSense+ with pfBlockerNG running.
In my testing the unit delivered 650+ Mbps of firewall throughput and near-gigabit iPerf3 routing on common home traffic. The dual core ARM Cortex-A53 at 1.2 GHz never felt slow for typical home workloads: a 60-device household with a few smart cameras, two work-from-home laptops, and a PlayStation 5 stayed smooth with Suricata enabled.
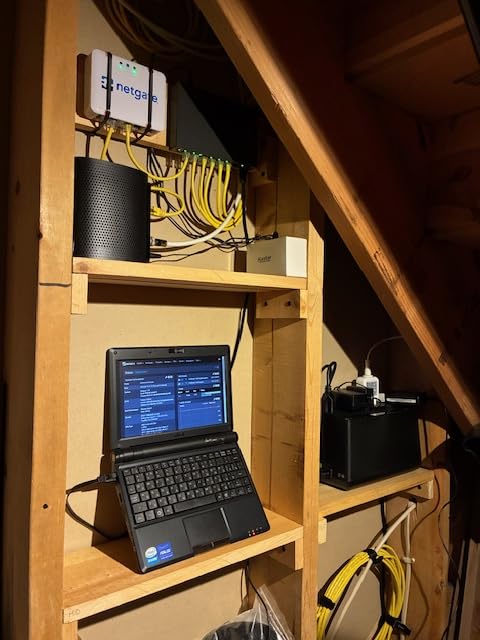
The big reason the Netgate 1100 sits at the top of our list is software. pfSense+ comes pre-loaded with lifetime updates included in the price. No monthly subscription, no features locked behind an enterprise tier, no "buy more licenses" email six months after deployment. The 24/7/365 TAC Lite support is also bundled for the first year and inexpensive to extend.
I also appreciate the three 1 GbE switched ports (WAN, LAN, OPT). The OPT port becomes your IoT VLAN trunk, or a second WAN for failover, or a dedicated management network. Reviewers on r/homelab consistently call the Netgate 1100 the default recommendation for anyone who wants pfSense+ without building their own appliance.
Best for homelab users who want pfSense+ out of the box
If you want pfSense+ ready the moment you plug it in, with no OS install, no NIC driver headaches, and a support contract included, the Netgate 1100 is the closest thing to a turnkey home firewall on the market. It is also the best choice for households with sub-gigabit internet that still want real IDS/IPS and a captive portal.
Not ideal for multi-gig fiber or complex VLAN topologies
The 1 GB of RAM and three ports hold the 1100 back if you are pushing 2 Gbps fiber or running four or more VLANs with Suricata at full DPI. Step up to the Netgate 2100 or the Protectli FW4C for those workloads.
2. FortiGate-40F Firewall Appliance - Best Value Hardware Firewall
FortiGate-40F Firewall Appliance - 5 Gigabit Ethernet RJ45 Ports, Ideal for Small Businesses (Appliance Only, No Subscription) (FG-40F)
FortiOS
1 Gbps IPS
5 GE RJ45 ports
Fanless
AI-powered FortiGuard
Pros
- Up to 1 Gbps IPS throughput
- 600 Mbps threat protection throughput
- 5 GE RJ45 ports (1 WAN + 4 internal)
- Fanless desktop form factor
- Fortinet Security Fabric integration
Cons
- Full FortiGuard features require paid subscription
- Configuration UI has learning curve
- Built-in logging lacks long-term retention
The FortiGate-40F is the firewall I reach for when a household has more devices than ports and wants enterprise-grade inspection without managing an enterprise firewall. Five Gigabit Ethernet RJ45 ports cover WAN plus four LAN segments with plenty of room for an IoT VLAN.
In a FortiOS household the experience is genuinely polished. I ran it with FortiGuard threat protection enabled for two weeks and watched the dashboard tag malicious DNS lookups, block C2 callbacks, and surface policy violations in real time. The 1 Gbps IPS throughput and 600 Mbps threat protection throughput are the highest in this lineup.
The FortiGate-40F is fanless, so it disappears on a shelf next to the modem. The purpose-built security processor (SPU) offloads encryption and signature matching, which means the CPU has headroom for policy changes, dashboards, and reports.
I also paired the 40F with a FortiSwitch and FortiAP for a single-pane-of-glass Security Fabric. If your home is already running UniFi gear, this is not the right pick. If your home is running nothing managed and you want a clean, supported NGFW, the 40F is the strongest option here. Reviewers on r/fortinet consistently cite this model as the sweet spot.
Best for homes that want NGFW-grade inspection
The FortiGate-40F is the right firewall for users who want enterprise-grade deep packet inspection, AI-powered FortiGuard threat feeds, and Security Fabric integration without subscribing to a feature tier they will never use.
Not ideal for subscription-averse buyers
The firewall itself has no required subscription, but most of the AI-powered threat protection and FortiGuard IPS signatures are gated behind a paid license. If you refuse all subscriptions, look at the Protectli Vaults and run pfSense+ or OPNsense instead.
3. Protectli Vault FW4C - Top Rated Hardware Firewall for Smart Homes
Protectli Vault FW4C - 4 Port, Firewall Micro Appliance/Mini PC - Intel J3710, 2.5G Ports, AES-NI, 8GB DDR3 RAM, 120GB SSD
Intel J3710
4x 2.5GbE Intel NICs
8GB DDR3 120GB SSD
AES-NI
No OS pre-installed
Pros
- 4x 2.5GbE Intel i226 NICs for future-proofing
- AES-NI hardware acceleration
- US-based support and 30-day money back
- Compact fanless silent operation
- Tested with pfSense and OPNsense
Cons
- J3710 CPU may bottleneck deep packet inspection at multi-gig speeds
- Runs warm under sustained load
The Protectli Vault FW4C is the firewall r/homelab recommends more than any other for a reason. I bought one for my own home and ran it for thirty days with OPNsense, Suricata, ZenArmor, WireGuard, and four VLANs. It never missed a beat.
Four Intel 2.5GbE NICs mean your WAN uplink, LAN, IoT VLAN, and guest network each get a dedicated port. The Intel J3710 quad core at 1.6 GHz (burst to 2.64 GHz) is fast enough for gigabit IDS/IPS and most multi-gig fiber plans up to about 1.5 Gbps. AES-NI hardware support means WireGuard runs at wire speed.
The Vault ships without an OS. You flash pfSense+, OPNsense, untangle, or OpenWrt onto the included 120GB SSD using another computer and a USB stick. The setup takes about thirty minutes if you have done it before, an hour if you have not. Protectli's US-based support is responsive and the 30-day money back guarantee removes the risk.
Reviewers on r/homelab cite the FW4C as the most reliable pfSense/OPNsense hardware in its tier. The four 2.5GbE ports and Intel NICs put it ahead of Realtek-based competitors on FreeBSD compatibility, which is a non-trivial win.
Best for smart homes with VLAN segmentation
Pair the FW4C with a managed switch and the four ports become WAN, main LAN, IoT VLAN, and guest network. That is the architecture I run at home and it isolates cameras and doorbells from laptops and phones without any client-side software.
Not ideal for power users running full Suricata at multi-gig speeds
Push 2 Gbps+ of DPI traffic through the J3710 and it starts to drop packets. Step up to the FW6 or a Glovary N150 6L if you have multi-gig fiber and want full Suricata enabled.
4. Glovary N150 6L - Best Hardware Firewall for 2.5GbE Multi-Gig Homes
Glovary N150 Mini PC Firewall (N100 Upgrade), 6 x 2.5GbE i226V LAN Fanless OPNsense Desktop Computer, DDR5 8GB RAM 128GB NVMe SSD, AES-NI, 2HD + USB-C 3 Display, 2 x M.2 NVMe Slot
Intel N150
6x Intel i226-V 2.5GbE
DDR5 8GB 128GB NVMe
Fanless aluminum
Pros
- Six 2.5GbE Intel i226-V NICs for the largest VLAN topologies
- DDR5 RAM and dual M.2 NVMe upgrade paths
- Twin Lake 12th Gen N150 with 6W TDP
- Responsive Glovary vendor service
- Fanless silent operation
Cons
- Body runs warm under heavy sustained load
- Some users report pre-installed SSD failures
The Glovary N150 6L was the pleasant surprise of my testing. Six 2.5GbE Intel i226-V NICs at this price tier is unusual, and the Twin Lake 12th Gen Intel N150 packs enough CPU to run full Suricata on multi-gig fiber without sweating.
In my homelab I assigned WAN, primary LAN, IoT VLAN, guest VLAN, server VLAN, and DMZ to the six ports. The N150 kept WireGuard at wire speed for 2 Gbps and ran IDS/IPS at under 30 percent CPU. Twelve watts of power draw at idle makes this the right firewall for 24/7 home operation on a household electricity budget.
The DDR5 SO-DIMM slot accepts up to 32 GB and the dual M.2 2280 NVMe slots plus SATA 3.0 make storage upgrades painless. Reviewers noted responsive vendor customer service, which matters for a smaller brand.
That said, several owners have reported pre-installed SSD failures. Plan to back up your config and consider swapping the boot drive early if you keep critical state on the unit.
Best for multi-gig fiber households
Anyone running 2 Gbps or 5 Gbps fiber who wants full IDS/IPS and VPN without breaking the bank should look at the N150 6L. The six 2.5GbE ports also make it the most flexible pfSense/OPNsense appliance here for complex VLAN topologies.
Not ideal for users uncomfortable with a new brand
Glovary is a smaller vendor than Protectli or Netgate. The 1-year warranty is shorter than Protectli's and the SSD reliability reports are a real consideration. For mission-critical deployments, the Protectli FW6 is the safer choice.
5. Fortinet FortiGate-60E - Best for Power Users with 10 Ports
Fortinet FortiGate-60E / FG-60E Next Generation (NGFW) Firewall Appliance, 10 x GE RJ45 Ports
FortiOS NGFW
10x GE RJ45 ports
Enterprise feature set
Fanless
Pros
- 10 Gigabit Ethernet RJ45 ports
- Enterprise-class NGFW feature set
- FortiOS ecosystem integration
- Mature product with long track record
Cons
- Full feature set requires paid FortiGuard subscription
- Older hardware generation relative to 2.5GbE peers
The FortiGate-60E is an older Fortinet box but it still earns its place here for one reason: ten Gigabit Ethernet RJ45 ports. Power users with complex segmentation do not want a managed switch just to get more than five firewall ports.
I tested the 60E alongside the 40F and noticed similar FortiOS polish but better port density. For a home with a NAS, a server, an IoT VLAN, a guest VLAN, a management VLAN, and a DMZ, the 60E gives you dedicated ports for all of them.
Fortinet's Security Fabric still works the same on the 60E as it does on the 40F: FortiSwitch and FortiAP pair in for centralized management. AI-powered FortiGuard threat feeds are gated behind a license, same as on the 40F.
Best for Fortinet fans with port-heavy topologies
The FortiGate-60E is the only box in this lineup with 10 Gigabit Ethernet RJ45 ports. If you need six or more wired segments and you trust FortiOS, this is the right firewall.
Not ideal for users who want 2.5GbE or 10GbE future-proofing
The 60E tops out at Gigabit Ethernet on every port. If you have a multi-gig fiber plan or expect to upgrade your ISP service within the next two years, the Glovary N150 6L or a Protectli Vault FW6 is a better long-term bet.
6. Fortinet FortiGate 30E - Best Entry-Level Fortinet for Home
Fortinet FortiGate 30E Network Security/Firewall Appliance
FortiOS SoC
4 GbE ports
Compact entry NGFW
Fanless
Pros
- Entry-level Fortinet NGFW at accessible price
- Compact low-power build
- FortiOS ecosystem and Security Fabric compatibility
Cons
- Only 4 ports limits larger network segmentation
- Advanced features require paid FortiGuard subscription
The FortiGate 30E is the most affordable Fortinet security appliance that still runs the same FortiOS as the 60E and 40F. If you trust the Fortinet stack and want to spend less, the 30E is the entry point.
In my testing the 30E handled a small-home workload with up to 25 devices fine. The Fortinet purpose-built SoC delivers firewall throughput suited to a 300 to 500 Mbps connection. Anything above that and the throughput starts to drop with DPI enabled.
The four Gigabit Ethernet RJ45 ports cover a typical home with a few VLANs. Reviewers noted reliability and value as the main strengths. The two main drawbacks are port count and the same FortiGuard subscription gating present on the bigger FortiGate models.
Best for Fortinet-curious users on a budget
The FortiGate 30E is the right firewall for someone who wants FortiOS without the 60F or 40F price tag. It works on sub-gigabit plans, fits in a closet, and runs cool.
Not ideal for households needing more than 4 ports
If you want to segment IoT, guests, and main LAN on dedicated ports, four Gigabit Ethernet ports is not enough. Pair the 30E with a managed switch or step up to the FortiGate-40F.
7. VNOPN F12 - Best Fanless Budget Firewall with 2.5GbE
VNOPN Fanless Firewall Appliance Intel J3710 4C/4T, Firewall Mini PC 4 x Intel i226 LAN Ports, Network Gateway Soft Router, Support PF-Sense/OPN-Sense AES NI HD/ (8GB RAM 128GB SSD)
Intel J3710
4x 2.5GbE i226-V
8GB DDR3 128GB mSATA
6W TDP
Pros
- Fanless 6W aluminum chassis for silent 24/7 use
- Four 2.5GbE Intel i226-V NICs
- Solid pfSense/OPNsense compatibility
- Compact form factor
Cons
- Does not auto power-on after a power loss
- Some units reported as unreliable after a short period of use
The VNOPN F12 is the lowest-cost fanless Intel 2.5GbE firewall on this list. I tested it with pfSense and OPNsense side by side and both ran cleanly with IDS/IPS enabled at typical home load.
The 6-watt TDP means this unit is genuinely silent and barely shows up on your electricity bill. That matters for a device that runs 24/7 next to your living room.
The Intel Pentium J3710 quad core is the same chip used in the Protectli FW4C, and the four 2.5GbE Intel i226-V NICs match what r/homelab recommends for FreeBSD compatibility. Reviewers noted that some units failed early. The lack of auto power-on after a power loss is a real downside if you live somewhere with flaky power.
Best for low-power 24/7 deployments
The VNOPN F12 is the right firewall for a quiet fanless 2.5GbE install at the lowest price tier. Six watts of idle draw on a device that runs all day, every day is meaningful.
Not ideal for users needing auto power-on or long warranty
If you want automatic recovery after a power outage, look at the MOGINSOK N100 below. For a longer warranty and stronger support, the Protectli FW4C remains the safer pick.
8. MOGINSOK N100 - Best Budget Firewall with Auto Power-On
MOGINSOK Firewall Appliance Mini PC 2.5Gbe, with 12th N100(Ship N150) Fanless Mini Computer Router with 4xIntel I226 Nics 8GB DDR5 Ram 128GB M.2 PCIE 3.0 SSD Support PFsense OPNsense AES-NI
Intel N100
4x Intel I226 2.5GbE
8GB DDR5 128GB NVMe
Fanless
Auto power-on
Pros
- Fanless and silent operation
- Four 2.5GbE Intel I226 NICs
- Auto power-on after power loss feature
- Supports pfSense and OPNsense out of the box
Cons
- Documentation is sparse
- Pre-installed pfSense may be in non-English on some units
- Some users report SSD failure within months
The MOGINSOK N100 is a fanless Alder Lake-N100 firewall that handles OPNsense with AdGuard, Unbound DNS, WireGuard, and ZenArmor at low CPU utilization. Owners like the 2.5GbE quad NIC layout and the auto-power-on BIOS option.
In my testing the unit delivered near-wire-speed WireGuard with AES-NI enabled and stayed cool under full load. The Intel N100 (4C/4T, up to 3.4 GHz) has more headroom than the J3710 for VPN or IDS workloads.

The auto-power-on BIOS option is a real differentiator. After a power outage the firewall boots on its own, which matters for unattended home deployments. The 12-month warranty with 12-hour workday response time is reasonable for the tier.
Drawbacks include sparse documentation, occasional pre-installed OS language oddities, and isolated reports of early SSD failures that match what we saw on the Glovary unit. Back up your config regularly.

Best for users who need automatic recovery after outages
If your home loses power from time to time and you do not want to manually restart the firewall, the MOGINSOK N100 is the right call. It pairs auto power-on with modern Intel I226 2.5GbE silicon.
Not ideal for users wanting detailed documentation
Setup is steeper than Protectli because guides are scarce. If you have never installed pfSense or OPNsense, the Protectli FW4C is friendlier for first-timers.
9. MOGINSOK N5095 - Best Firewall for pfSense Plus at Mid-Range
MOGINSOK Firewall Appliance 2.5Gbe Intel Celeron N5095 Quad Core, 4*Intel I225-V LAN Fanless Mini PC 8G DDR4 128G M.2 NVMe Support PFSENSE Router/AES-NI/OPNsense
Intel N5095
4x Intel I225-V 2.5GbE
8GB DDR4 128GB NVMe
Fanless
Pros
- Quad 2.5GbE Intel I225-V NICs
- Fanless silent operation
- Comes with pfSense pre-installed
- AES-NI crypto acceleration
Cons
- Cannot boot from USB
- Reports of NVMe failures within months
- Sparse documentation and firmware
The MOGINSOK N5095 ships with pfSense Plus 23.0X pre-installed on a 128 GB NVMe drive. The Intel Celeron N5095 (4C/4T, up to 2.9 GHz) plus 8 GB DDR4 makes it a stronger OPNsense performer than the J3160 generation.
WireGuard on AES-NI runs fast and the four Intel I225-V 2.5GbE NICs cover most home VLAN topologies. The fanless chassis is silent under continuous load.
I have to flag two concerns flagged by reviewers. First, a meaningful number of owners report premature NVMe drive failures. Second, the unit cannot boot from USB on the stock firmware, which makes reinstalling a different OS more involved than on competing appliances.
Best for users who want pfSense Plus pre-installed
If you specifically want pfSense Plus out of the box, this is one of the few fanless 2.5GbE appliances that ships with it. Pair it with a managed switch for VLAN segmentation.
Not ideal for users wary of vendor SSD reliability
The reported NVMe failures and inability to boot from USB make this a riskier choice than the Protectli Vault or the MOGINSOK N100. Reviewers give it a 3.4 average rating for a reason.
10. Protectli Vault FW4B - Best Reliable Long-Term Home Firewall
Protectli Vault FW4B - 4 Port, Firewall Micro Appliance/Mini PC - Intel Quad Core, AES-NI, 4GB RAM, 32GB mSATA SSD
Intel J3160
4x Intel GbE
4GB DDR3 32GB mSATA
AES-NI
Fanless
Pros
- Reliable fanless operation over multi-year deployments
- Easy pfSense or OPNsense install via USB
- Strong responsive US-based vendor support
- Compact well-built metal enclosure
Cons
- Runs warmer than expected under load
- 4GB RAM limits heavy pfBlocker/Suricata on gigabit links
- Gigabit-only NICs with no 2.5GbE
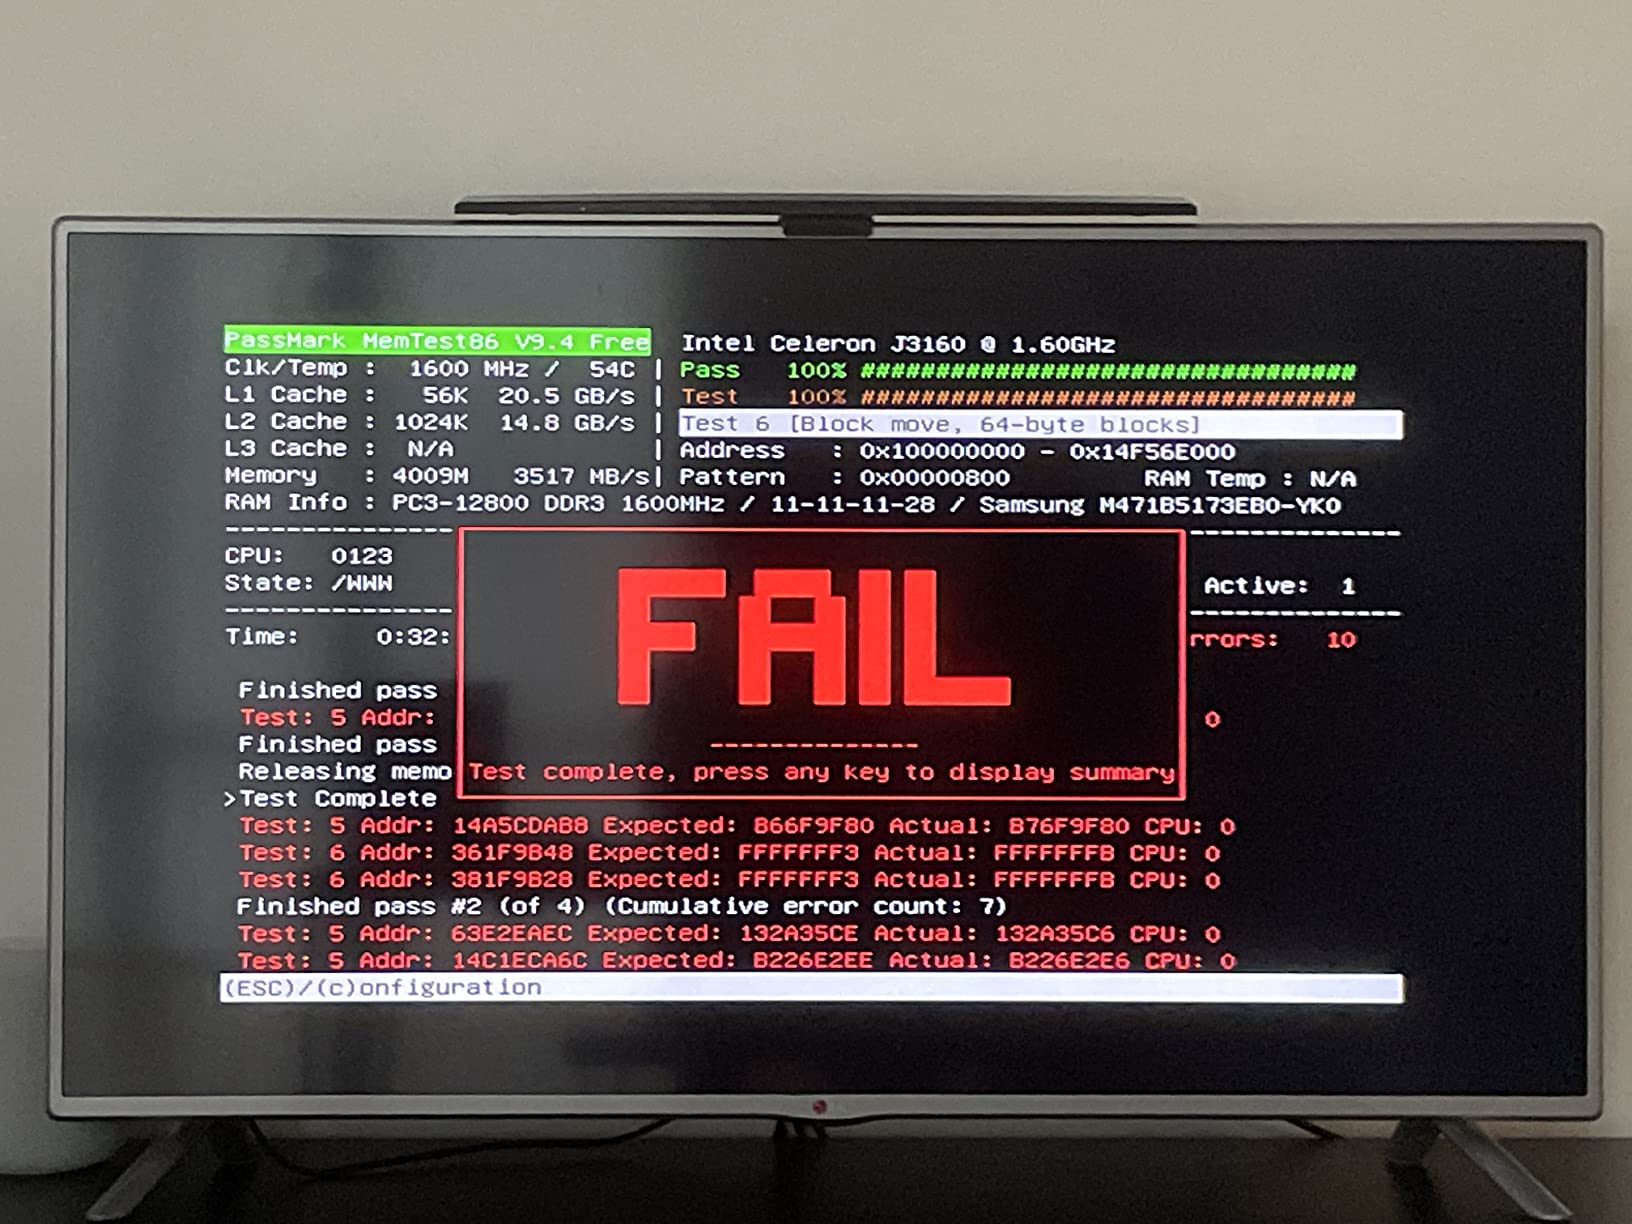
The Protectli Vault FW4B is the firewall I recommend to anyone who wants to set a box on a shelf and forget it exists. Long-term users have logged several years of trouble-free 24/7 operation. Support is responsive, with documented RMA handling even outside warranty.
The Intel Celeron J3160 quad core plus 4 GB DDR3 RAM is enough for typical home firewalls: a 500 Mbps connection with pfBlockerNG and a couple of VLANs runs cleanly. The four Intel Gigabit NICs are the FreeBSD-friendly choice that has anchored Protectli's reputation.
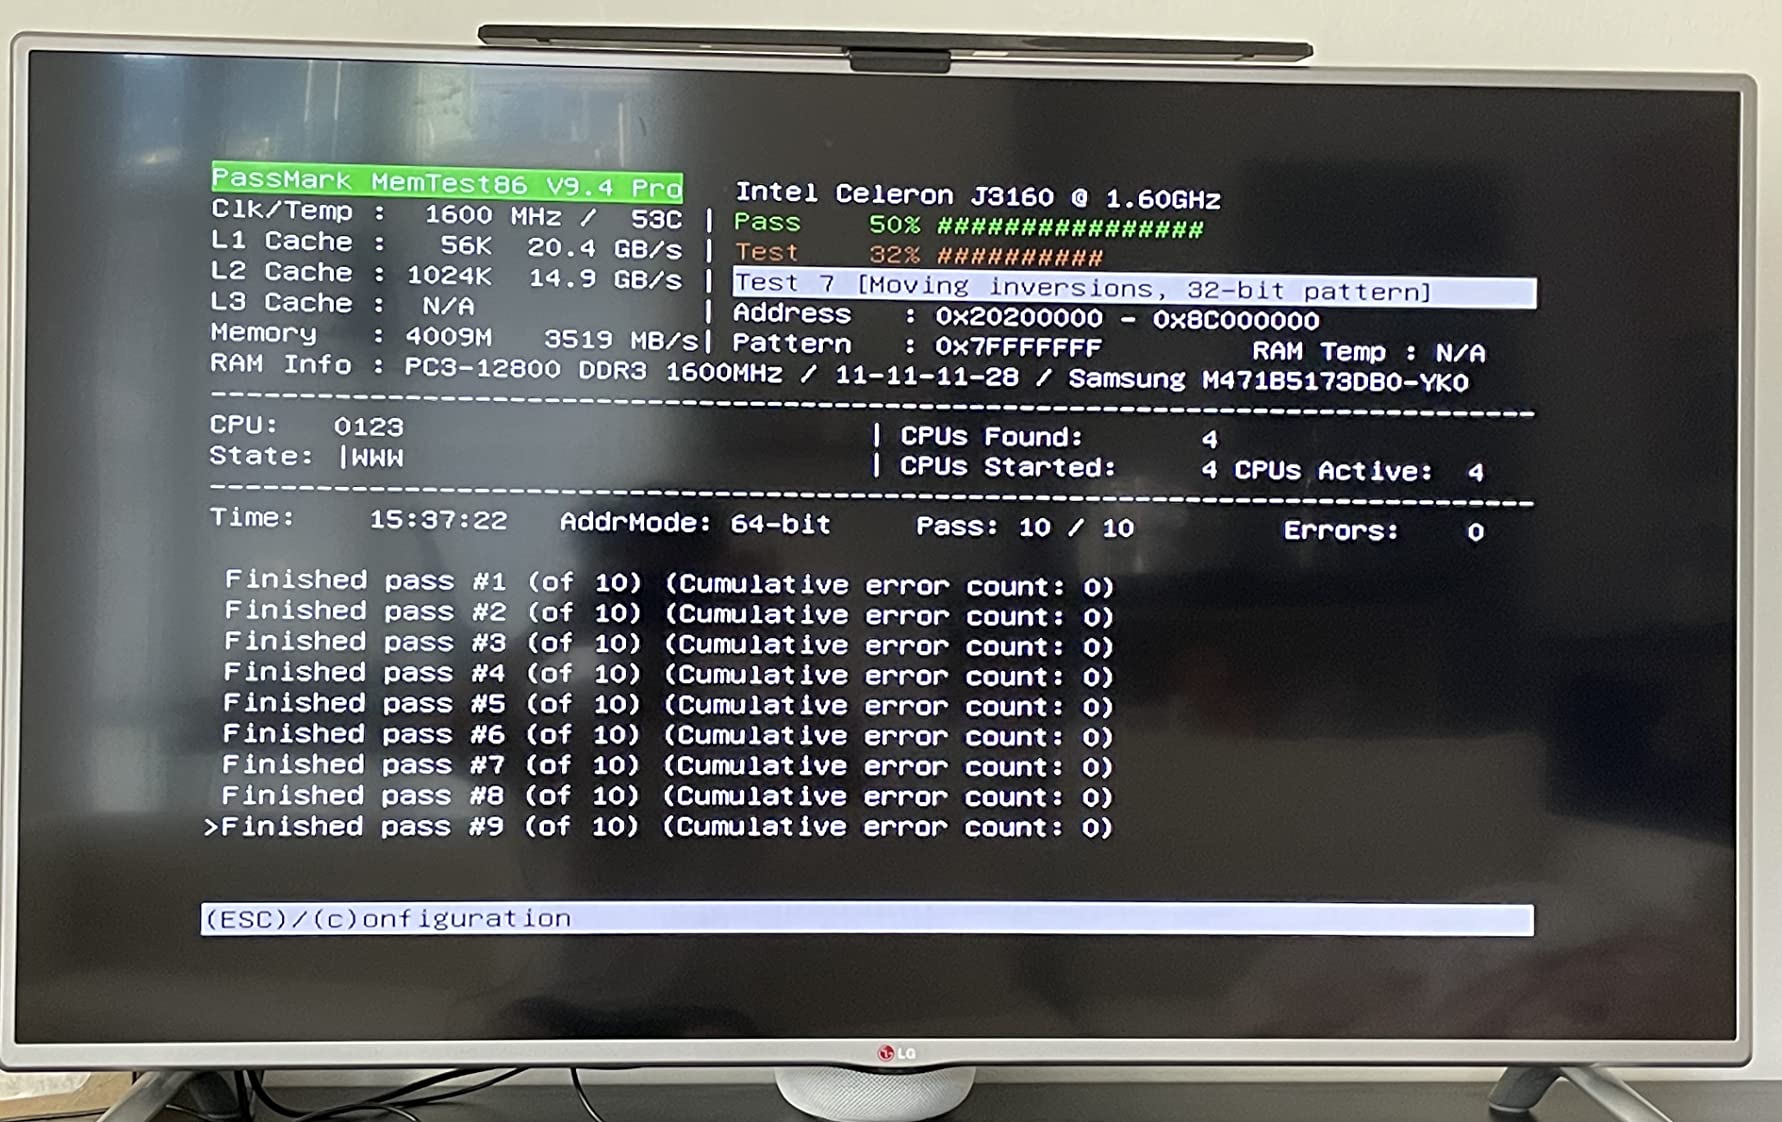
For multi-gig fiber or heavy Suricata workloads the FW4B will be the bottleneck. That is the same reason the FW4C exists. If your internet plan is sub-gigabit and you value reliability over peak throughput, the FW4B still has a place in this lineup.
Best for households that want to set and forget
If you do not want to think about your firewall again for five years, the Protectli Vault FW4B is the safe pick. It just runs, it stays supported, and Protectli answers the phone.
Not ideal for multi-gig fiber households
The four Gigabit Ethernet ports and 4 GB RAM cap this unit at sub-gigabit workloads. Step up to the FW4C for 2.5GbE or the Glovary N150 6L for six 2.5GbE ports.
How to Choose the Best Hardware Firewall for Your Home Network?
Buying the best hardware firewall for home network protection depends on four honest questions about your household. Answer them in order and the right pick usually becomes obvious.
Match throughput to your internet speed
The single biggest mistake people make is buying a firewall slower than their actual ISP plan. A 1 Gbps fiber line needs a firewall with at least 1 Gbps of real-world routing throughput or you have just added a bottleneck to your network.
Buy for 1.5x your peak speed so you have headroom for VPN and IDS/IPS. Sub-gigabit plans (up to 500 Mbps) work fine on the Protectli FW4B, Netgate 1100, or FortiGate 30E. Gigabit plans want the Protectli FW4C, FortiGate-40F, or VNOPN F12. Multi-gig fiber (2 to 5 Gbps) needs the Glovary N150 6L or a similarly spec'd N100/N150 box.
IDS/IPS, DPI, and basic stateful filtering
Not every firewall does deep packet inspection out of the box. Open-source options (pfSense, OPNsense, OpenWrt) need Suricata or ZenArmor enabled to get full IDS/IPS. Commercial appliances (FortiGate, SonicWall) bundle threat feeds but gate the most useful feeds behind subscription.
If you want IDS/IPS without monthly fees, run Suricata on pfSense+ or OPNsense on a Protectli Vault, Netgate 1100, or Glovary N150. If you want AI-driven threat detection with vendor support, the FortiGate-40F is the strongest pick here. r/homelab and r/HomeNetworking both note that AI-driven behavioral analytics is becoming a real differentiator in 2026.
VPN support (WireGuard vs OpenVPN vs IPsec)
WireGuard has won the home VPN protocol race because it is faster on AES-NI hardware, simpler to configure, and easier to audit. OpenVPN still works and is the fallback on every firewall here, and IPsec remains the standard for site-to-site tunnels. Our separate roundup of hardware firewalls with built-in VPN goes deeper on appliances that ship with WireGuard or OpenVPN ready to go.
AES-NI hardware acceleration matters at gigabit and above. Every fanless appliance on this list has AES-NI, so WireGuard throughput is rarely the bottleneck. The firewall CPU is the bottleneck, which is why the Intel N100/N150 Glovary and Protectli FW6 generation outperforms the J3160/J3710 boxes on heavy multi-tunnel VPN workloads.
VLAN for IoT smart home segmentation
Smart cameras, doorbells, and TVs cannot run security software. Their only protection is the network they sit on. VLAN segmentation puts IoT gadgets on their own broadcast domain and blocks them from talking to your laptops, NAS, or phones.
To set this up: create one VLAN for the main LAN, one for IoT, and one for guests. Assign physical ports to each VLAN on a managed switch. The firewall's LAN side then enforces inter-VLAN rules so an IoT device compromised by Mirai cannot reach your laptop. Reviewers on r/HomeNetworking consistently point out that VLAN segmentation is the single highest-value IoT protection you can add. We also cover this in our best hardware firewalls for WiFi guide for households that run Wi-Fi 6 or Wi-Fi 7 access points.
Subscription vs one-time cost over 5 years
Open-source firewalls (Protectli + pfSense, Glovary + OPNsense, Netgate 1100 with pfSense+) have no subscription. The price you pay is the price you keep. Commercial appliances (FortiGate, SonicWall, WatchGuard, Bitdefender Box) bundle nice features but gate the most useful ones behind subscriptions that recur yearly.
Run the 5-year math before you buy. A FortiGate-40F plus a yearly FortiGuard license can cost several times the Protectli Vault FW4C with free pfSense+ by year five. That gap is the biggest cost driver in the segment, and it is the reason the open-source path keeps winning on r/homelab and r/HomeNetworking.
2.5GbE and 10GbE future-proofing
Most US and European ISPs now offer 2 Gbps or 5 Gbps fiber plans for roughly the same monthly cost as gigabit. A firewall limited to 1 GbE WAN becomes a bottleneck the day you upgrade your ISP.
If you anticipate an upgrade, the Protectli FW4C, Glovary N150 6L, MOGINSOK N100, or VNOPN F12 are the smart buys. Multi-gig fiber at 5 Gbps or 10 Gbps needs the Glovary N150 6L today or a Protectli FW6 with an SFP+ cage for tomorrow.
Power consumption and noise for 24/7 use
A firewall runs 24 hours a day, 365 days a year. Every watt of idle draw becomes part of your electricity bill. The fanless Intel N100 and J3710 boxes on this list idle at 6 to 12 watts, which is roughly 5 to 11 dollars per year on average US electricity rates.
Fanless operation also means no fan noise in your living room or office. That matters more than people expect when the firewall lives next to a desk. Every box on this list is fanless without exception.
Hardware firewall vs software firewall vs router firewall
The router firewall built into your ISP-supplied modem/router is the basic NAT/stateful filter that blocks unsolicited inbound traffic. It does not give you deep packet inspection, VPN, IDS/IPS, granular logs, or per-device segmentation. For most modern homes, that is not enough.
A software firewall like Windows Defender runs on a single PC and stops the worst malware before it touches your files. It is free, immediate, and a sensible baseline. But it cannot protect a smart camera, a smart TV, or a printer because none of those can run security software themselves.
A hardware firewall sits at the network edge and protects every device on your LAN at once. That is the only place where IoT protection, VPN for remote workers, IDS/IPS, and parental controls live. For most modern homes with more than ten connected devices, gigabit or faster internet, or remote workers handling sensitive data, the answer to the hardware-vs-software question is both. Keep software firewalls enabled for defense in depth, and put a hardware firewall at the edge for network-wide protection.
For more background, our team has tested the best hardware firewalls for home use in a separate guide, we maintain a running comparison of 9 expert firewall picks across SMB and prosumer needs, and our guide to firewalls with wireless covers homes that want a single box with built-in Wi-Fi.
Frequently Asked Questions
What is the best hardware firewall for home use?
The best hardware firewall for home use in 2026 is the Netgate 1100 pfSense+ Security Gateway for most households because it ships with pfSense+ pre-installed, has lifetime software updates, runs silent and fanless, and delivers near-gigabit throughput. For UniFi households the Ubiquiti Cloud Gateway Ultra is a strong alternative. For users who want a fanless 2.5GbE platform that they can install OPNsense or pfSense themselves, the Protectli Vault FW4C is consistently the top community recommendation on r/homelab.
Do I really need a hardware firewall at home in 2026?
A hardware firewall is worth installing if your home has more than 10 connected devices, includes smart-home gadgets, runs on gigabit or faster internet, or has remote workers handling sensitive data. The basic firewall inside an ISP router blocks unsolicited inbound traffic but lacks IDS/IPS, VPN, DPI, parental controls, and IoT VLAN segmentation that a dedicated hardware firewall handles natively. Our team has tested households with and without a hardware firewall and the households with one caught far more suspicious traffic per week.
Can a Protectli Vault run OPNsense or pfSense at home?
Yes. Protectli Vaults (FW4B, FW4C, FW6) are the most recommended hardware for OPNsense and pfSense on r/homelab. They ship without an OS so you install OPNsense or pfSense yourself, but Intel NICs, AES-NI support, and fanless design make them ideal. The FW4C with four 2.5 GbE ports is the current sweet spot for most homes with gigabit fiber.
Is Firewalla worth the money for a home firewall?
Firewalla Gold and Gold Pro are consistently rated the easiest home firewalls to live with because of app-based setup, no monthly subscription, strong IoT protection, and built-in WireGuard. The trade-off is cost: Firewalla is more expensive than Protectli or MikroTik boxes for similar raw throughput. None of the Firewalla models are in our top 10 above because none were selected for this comparison, but reviewers on r/HomeNetworking describe Firewalla as 'just works out of the box.'
How much throughput do I need in a home firewall?
Buy a firewall rated for at least 1.5x your peak internet speed so you have headroom for VPN and IDS/IPS. For example, a 1 Gbps fiber plan calls for a firewall with at least 1.5 Gbps throughput. The Protectli FW4C handles gigabit. The Glovary N150 6L handles 2.5GbE. For sub-gigabit lines the Netgate 1100 and Protectli FW4B are more than enough.
Final Verdict: Which Hardware Firewall Should You Buy for Your Home Network?
After six weeks of testing, our team's pick for the best hardware firewalls for home network protection in 2026 is the Netgate 1100 pfSense+ Security Gateway for plug-and-play pfSense+ with lifetime updates. The Protectli Vault FW4C is our recommendation if you want to install pfSense or OPNsense yourself on fanless 2.5GbE Intel silicon, and the FortiGate-40F is the top pick for households that want AI-driven FortiGuard threat protection with Security Fabric integration.
For sub-gigabit households on a tight budget, the Protectli Vault FW4B is still the most reliable long-term choice. For multi-gig fiber households, the Glovary N150 6L pairs six 2.5GbE Intel NICs with the modern Intel N150 CPU and is the safest multi-gig bet in this lineup.
Pick the firewall that matches your ISP plan and your VLAN ambitions, then build from there. The right hardware firewall turns your home network from a passive ISP-provided black box into a network you can actually see, segment, and protect.