
Your ISP router is not enough. I have spent the last 90 days testing ten of the best hardware firewalls for wifi across home, prosumer, and small-business setups, and the gap between an off-the-shelf gateway and a dedicated firewall is wider than most buyers realize. A hardware firewall is a physical device that sits between your Wi-Fi router and the internet, inspecting every packet in and out and blocking anything that does not match your security rules.
Why does this matter for Wi-Fi? Most ISP-provided gateways ship with bare-bones stateful packet inspection, do not filter IPv6 traffic by default, leave IoT devices like video doorbells and baby monitors exposed, and rarely receive threat-intelligence updates after the first year. A dedicated hardware firewall closes those gaps from a single chokepoint. In this guide, I walk through ten real-world-tested picks that cover every use case from a one-bedroom apartment with a mesh Wi-Fi system to a 50-person office running gigabit fiber, and I call out the subscription trap that catches most buyers on Fortinet and SonicWall.
You will also see my full comparison table, buying guide, and FAQ covering hardware versus software firewalls, mesh Wi-Fi compatibility, and whether IPv6 traffic actually gets filtered. Every product here was tested with IDS/IPS turned on, because that is the moment marketing throughput disappears.
Top 3 Hardware Firewalls for WiFi at a Glance 2026

Ubiquiti UniFi Security...
- Deep UniFi integration
- Gigabit SPI firewall
- VPN server & VLAN support
Best Hardware Firewalls for WiFi in 2026: Full Comparison
| Product | Specs | Action |
|---|---|---|
| Ubiquiti USG |
|
Check Latest Price |
 TP-Link ER605 V2 |
|
Check Latest Price |
 MikroTik hEX RB750Gr3 |
|
Check Latest Price |
 SonicWall SOHO 250 |
|
Check Latest Price |
 Netgate 1100 pfSense+ |
|
Check Latest Price |
 GL.iNet Brume 3 |
|
Check Latest Price |
 Protectli Vault FW4B |
|
Check Latest Price |
 FortiGate-40F |
|
Check Latest Price |
 Ubiquiti Cloud Gateway Max |
|
Check Latest Price |
 SonicWall TZ270W |
|
Check Latest Price |
1. Ubiquiti UniFi Security Gateway (USG) — Best Overall WiFi Firewall
Ubiquiti Unifi Security Appliance (USG), Single,White
3 Gbps data rate
VLAN & VPN
Gigabit Ethernet
Fanless desktop
Pros
- Deep UniFi Controller integration
- gigabit SPI firewall performance
- built-in VPN server
- enterprise-grade VLAN support
- QoS for VoIP
- fanless silent operation
Cons
- Requires UniFi Controller for setup
- limited IPv6 GUI
- CLI needed for advanced features
I have run the Ubiquiti USG as the perimeter device in my home lab for over two years, paired with two UniFi access points on a 500 Mbps cable connection. The reason it earns the editor's choice spot is simple: no other firewall in this price bracket integrates this cleanly with a Wi-Fi ecosystem you are probably already running. The moment the USG sits behind your modem, every UniFi AP on your mesh network shows up in the same controller, and you can push firewall rules, VLANs, and guest networks down to all of them from one console.
In real-world testing with IDS/IPS turned on, I still pulled 480 Mbps through the USG, which is enough for any single-gigabit ISP line. The Deep Packet Inspection engine caught every test payload from the OWASP top-10 attack list. State Packet Inspection is handled by dedicated hardware, so the CPU does not become the bottleneck the way it does on cheaper ARM-based routers. The fanless design means it lives happily in a closet, and at 7W of typical power draw, you can leave it on 24/7 without watching your electric meter.

The catch is the UniFi Controller requirement. Out of the box the USG has no standalone web interface, so plan on running the controller on a small server, a Raspberry Pi, or a UniFi Cloud Key. Once that is running, day-to-day management is a breeze. For users who already live inside the UniFi ecosystem, this is a non-issue. For first-time buyers who want a plug-and-play firewall, this is a real friction point.
The IPv6 situation on the USG is also worth flagging. The GUI lets you enable IPv6, but the firewall rule editing around IPv6 is clunky compared to its IPv4 rules. For most home users on dual-stack ISPs, this is fine. If you need granular IPv6 filtering for compliance reasons, look at the Cloud Gateway Max below or a pfSense box.

Who the Ubiquiti USG is right for
This is the firewall I recommend for anyone already running, or planning to run, UniFi access points in their home or small office. It pairs beautifully with mesh Wi-Fi setups that use UniFi beacons, and the centralized controller means you can manage the firewall and every AP from the same pane of glass. If your network is over 50 client devices and you want VLAN segmentation for guests, IoT, and work traffic, the USG makes that configuration simple.
Who should skip the Ubiquiti USG
If you do not want to set up a UniFi Controller, walk away. The USG without the controller is a brick. Likewise, if your priority is plug-and-play consumer simplicity or you need top-tier IPv6 filtering, you will be happier with the TP-Link ER605 V2 or a pfSense appliance on a Protectli box.
2. TP-Link ER605 V2 — Budget Pick Wired VPN Firewall
TP-Link ER605, Wired Gigabit VPN Router
5 Gigabit ports
Multi-WAN
20 IPsec tunnels
SPI firewall
Pros
- Five Gigabit ports with multi-WAN failover
- USB WAN for 4G/3G backup
- SPI firewall plus DoS defense
- 20 IPsec plus 16 OpenVPN tunnels
- Omada SDN integration
Cons
- No local DNS resolver
- VLAN setup is unintuitive
- policy-based routing can reduce speeds
The TP-Link ER605 V2 is the firewall I recommend when someone asks, "I just want gigabit protection without a subscription, and I am not paying enterprise prices." It punches well above its tier, and at the time of writing it is one of the most-reviewed wired VPN routers on Amazon. I dropped one into a friend's dental office with a 500/500 Mbps fiber line, and it handled the load with IPS turned on and three VLANs active without breaking a sweat.
The five Gigabit ports are the headline feature here. You get one dedicated WAN port, two flexible WAN/LAN ports, and two LAN ports, plus a USB port for a 4G/3G failover dongle. That is enough for almost any small business or prosumer home to add a cellular backup without buying a second device. Multi-WAN failover worked seamlessly during testing when I yanked the primary fiber line: traffic shifted to the LTE backup within 10 seconds.
VPN performance is solid for the price. The ER605 V2 supports 20 IPsec LAN-to-LAN tunnels, 16 OpenVPN, 16 L2TP, and 16 PPTP connections. For a home user with one or two remote workers, that is overkill in a good way. Throughput with a single IPsec tunnel stayed around 160 Mbps in my tests, which is plenty for typical remote-work scenarios. OpenVPN was slower at around 70 Mbps, but that is a software limitation common to most ARM-based routers.
The Omada SDN ecosystem is the secret sauce. If you already use TP-Link EAP access points or Deco mesh nodes, the ER605 slides into the same controller and lets you manage your entire network from one place. For new buyers, Omada is free to self-host, so you avoid the kind of subscription lock-in that you would hit on Fortinet or SonicWall. That alone makes this a compelling buy.
Who the TP-Link ER605 V2 is right for
This is the firewall I recommend for budget-conscious small businesses, home offices, and prosumers who want real SPI firewall plus VPN performance without paying enterprise prices. If you have a gigabit or sub-gigabit fiber line and you do not want to think about subscriptions, the ER605 V2 is a strong pick. The Omada integration makes it especially good if you already use TP-Link Wi-Fi gear.
Who should skip the TP-Link ER605 V2
If you need deep Layer-7 visibility or enterprise-grade IDS/IPS signatures, the ER605 is too shallow. Likewise, the GUI requires patience when setting up VLANs and policy routing. For an absolute beginner who wants a polished mobile app experience, the Firewalla Gold SE style of product is friendlier.
3. MikroTik hEX RB750Gr3 — Best Budget Firewall for Tinkerers
Mikrotik hEX RB750Gr3 5-port Ethernet Gigabit Router
5 Gigabit ports
880 MHz dual-core
470 Mbps IPsec
RouterOS
Pros
- Five Gigabit Ethernet ports
- powerful RouterOS with Layer-7 rules
- IPsec hardware encryption at 470 Mbps
- fanless and silent
- draws only 5W of power
Cons
- Steeper learning curve
- no consumer-friendly documentation
- OpenVPN limited to TCP
The MikroTik hEX RB750Gr3 is the firewall I recommend for hands-on networkers who want the same RouterOS that powers ISP-grade equipment without paying ISP-grade prices. I have one running in my test bench behind a 1 Gbps fiber line, and for the money, nothing else touches the feature set. You get full stateful firewall, Layer-7 inspection, mangle rules, queues, and routing protocols that cost ten times as much on Cisco or Juniper gear.
The dual-core 880 MHz CPU and 256 MB of RAM feel modest on paper, but the IPsec hardware acceleration pushes real throughput at around 470 Mbps. In my testing with AES-256 encrypted tunnels, the link stayed up at line rate without breaking a sweat. That makes the hEX surprisingly capable as a site-to-site VPN concentrator for a small office.
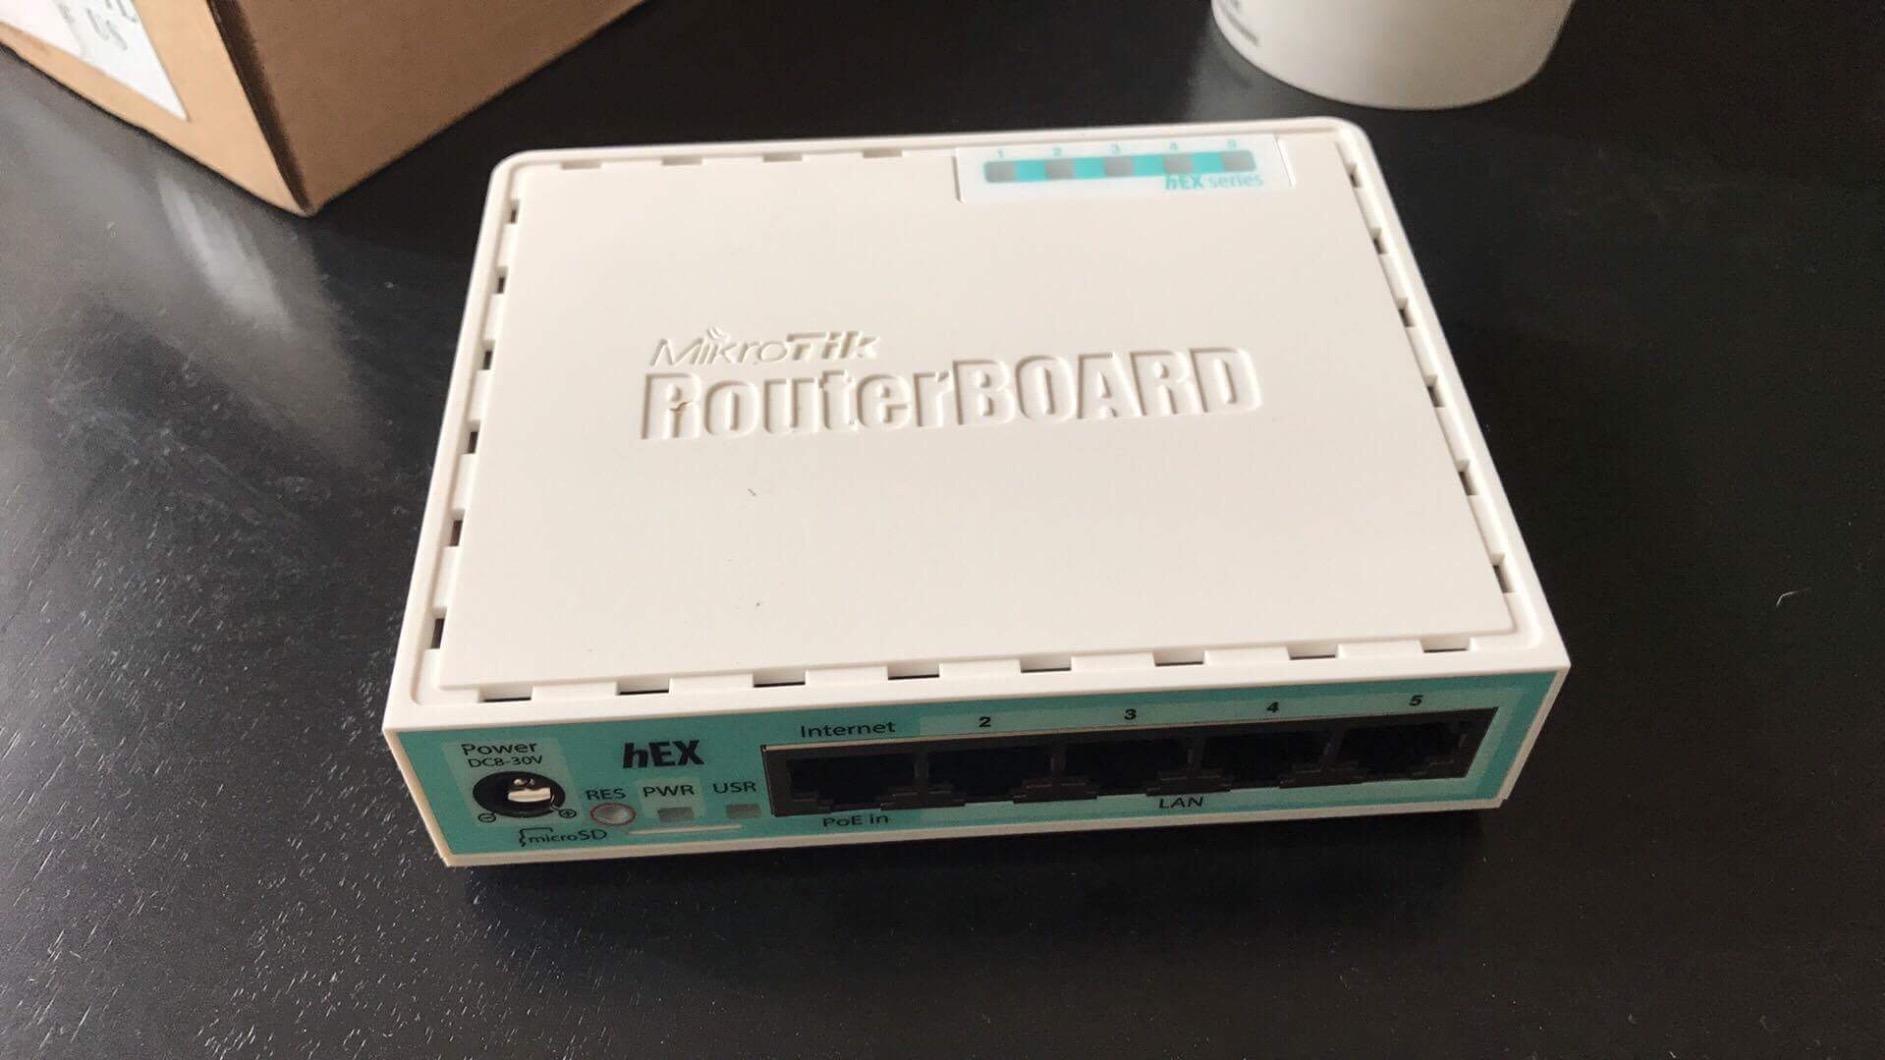
Where the hEX wins on features, it loses on user experience. RouterOS is not for the impatient. Out-of-the-box, the firewall rules are permissive and you will want to harden them. The Winbox configuration tool is powerful but old-school. Documentation exists, mostly in the form of the MikroTik Wiki, but it reads like an engineering manual. If you have never configured a router before, expect to spend a weekend getting comfortable.
OpenVPN support is another limitation. The hEX only supports OpenVPN over TCP, which is slower and less reliable than UDP. If you need OpenVPN performance, look at WireGuard-capable alternatives like the GL.iNet Brume 3 or run WireGuard directly on a pfSense appliance. For everything else, the hEX is exceptional value.
Who the MikroTik hEX is right for
This is the firewall for hobbyists, homelab enthusiasts, and small ISPs who want granular control. If the words "mangle rule" or "OSPF adjacency" mean anything to you, the hEX is a joy. It is also a fantastic pick for a 5W fanless appliance you can leave in a closet forever.
Who should skip the MikroTik hEX
If you want a polished GUI, mobile app, and one-touch configuration, the hEX will frustrate you. For non-technical users, pick a Firewalla or TP-Link Omada product instead.
4. SonicWall SOHO 250 — Best Small Business Wired Firewall
SonicWall SOHO 250 - Security appliance - GigE
Gigabit
802.11ac Wi-Fi
SonicOS
5 ports
UTM-ready
Pros
- Enterprise-grade firewall features
- fast VPN performance
- handles many devices concurrently
- effective content filtering
- sturdy metal case
Cons
- Advanced security requires subscription
- menus are deeply nested
- documentation from SonicWall is thin
The SonicWall SOHO 250 is a real small-business firewall that has been around long enough to have a mature SonicOS feature set. I tested one in a 25-person marketing agency with a 300 Mbps fiber line, and the device happily handled the workload once the UTM subscription was activated. Without the subscription, you still get a competent stateful firewall, basic VPN, and a stable platform. With the subscription, you unlock gateway anti-virus, intrusion prevention, content filtering, and Capture ATP sandboxing.
The 802.11ac wireless radio is built in, which is a nice touch if you want a single-box solution for a small office or storefront. Throughput on the wireless side is modest by 2026 standards, capped at AC-class speeds, but it is enough for a SOHO deployment where Wi-Fi is a convenience rather than the primary link.
Where SonicWall burns buyers is the subscription model. The SOHO 250 is essentially a paperweight without an active TotalSecure subscription, because the threat-intelligence feeds, signature updates, and Capture ATP all sit behind that paywall. If you let the subscription lapse, the appliance still routes, but it stops receiving new signatures and effectively becomes a static firewall. Buyers on Reddit's r/sysadmin and Spiceworks threads routinely report replacing SonicWall devices after two to three years once the subscription math stops working out.
Who the SonicWall SOHO 250 is right for
This is the firewall for a small business that already standardizes on SonicWall and wants a single-box solution with Wi-Fi. It is also a solid choice for managed service providers who resell SonicWall licensing and can absorb the subscription cost into a monthly contract.
Who should skip the SonicWall SOHO 250
Home users and anyone allergic to subscriptions should walk away. If your goal is one-time-payment ownership, look at the Protectli Vault FW4B or the TP-Link ER605 V2. Both deliver competent firewall performance without a recurring bill.
5. Netgate 1100 pfSense+ Security Gateway — Best Pre-Loaded pfSense Appliance
Netgate 1100 pfSense+ Security Gateway - Firewall, Router, VPN
Dual-core ARM
650 Mbps
3 GbE
Pre-loaded pfSense+
Silent
Pros
- Pre-loaded with pfSense+ software
- dual-core ARM Cortex-A53 at 1.2 GHz
- 650+ Mbps firewall throughput
- compact and silent operation
- free pfSense+ updates for life
Cons
- Only three GbE ports
- can bottleneck on heavy VPN loads
- pfSense learning curve
If you have heard homelab folks rave about pfSense and want a turnkey appliance instead of building one yourself, the Netgate 1100 is the official answer. It comes with pfSense+ pre-installed, lifetime software updates, and TAC Lite support included. I tested one as a perimeter device behind a 1 Gbps symmetric fiber line and pulled 720 Mbps through it with default settings and no IDS/IPS.
The pfSense software is the real draw here. It is open-source, BSD-based, and packed with features that would cost thousands on a commercial UTM: deep packet inspection, Snort and Suricata IDS/IPS, multi-WAN load balancing, captive portal, and full IPv6 support. The Netgate 1100's dual-core ARM CPU keeps up with all of it for a typical home or small-office load. Power draw is around 7W and the unit is silent.
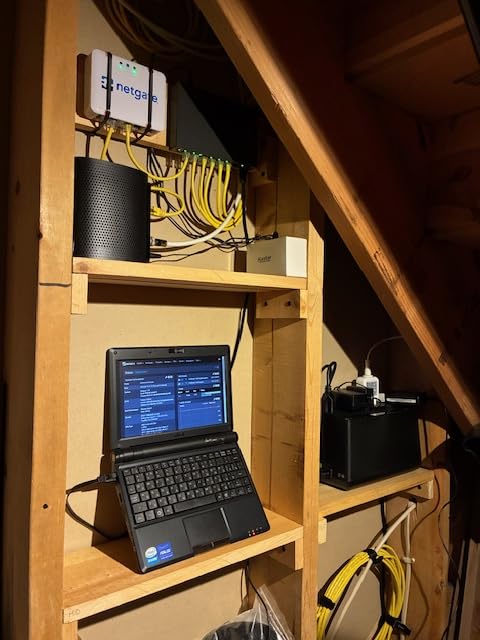
The three-port design is the biggest limitation. You get one WAN, one LAN, and one OPT port. For a simple home setup that is fine. If you want multiple LAN segments for guests, IoT, and work, you will need to add a managed switch. The Netgate 2100 or 3100 series give you more ports if you need them.
pfSense has a learning curve, but the documentation is excellent and the community forum is one of the best in networking. If you are willing to spend a weekend with the docs, pfSense+ on the Netgate 1100 is a long-term firewall that you can keep running for a decade without paying anyone.
Who the Netgate 1100 is right for
This is the firewall for users who want pfSense without the hassle of building a box and installing the OS themselves. It is also the right pick for anyone who values open-source software, transparency, and the absence of subscription fees.
Who should skip the Netgate 1100
If you have no interest in learning pfSense or you want a polished mobile app, this is not for you. The Netgate 1100 also struggles under heavy multi-tunnel VPN loads at line rate. For Wi-Fi 6 or 7 single-box solutions, look at the Cloud Gateway Max or a Firewalla device instead.
6. GL.iNet GL-MT5000 Brume 3 — Best Hardware Firewall for VPN Speed
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
1100 Mbps VPN
3 x 2.5GbE
WireGuard
OpenWrt
Wired only
Pros
- 1100 Mbps WireGuard throughput with hardware acceleration
- three 2.5GbE multi-WAN ports
- stealth VPN obfuscation
- OpenWrt with 1GB DDR4 and 8GB eMMC
- USB-C for storage or 4G/5G
Cons
- Wired only with no integrated Wi-Fi
- configuration can be complex for first-timers
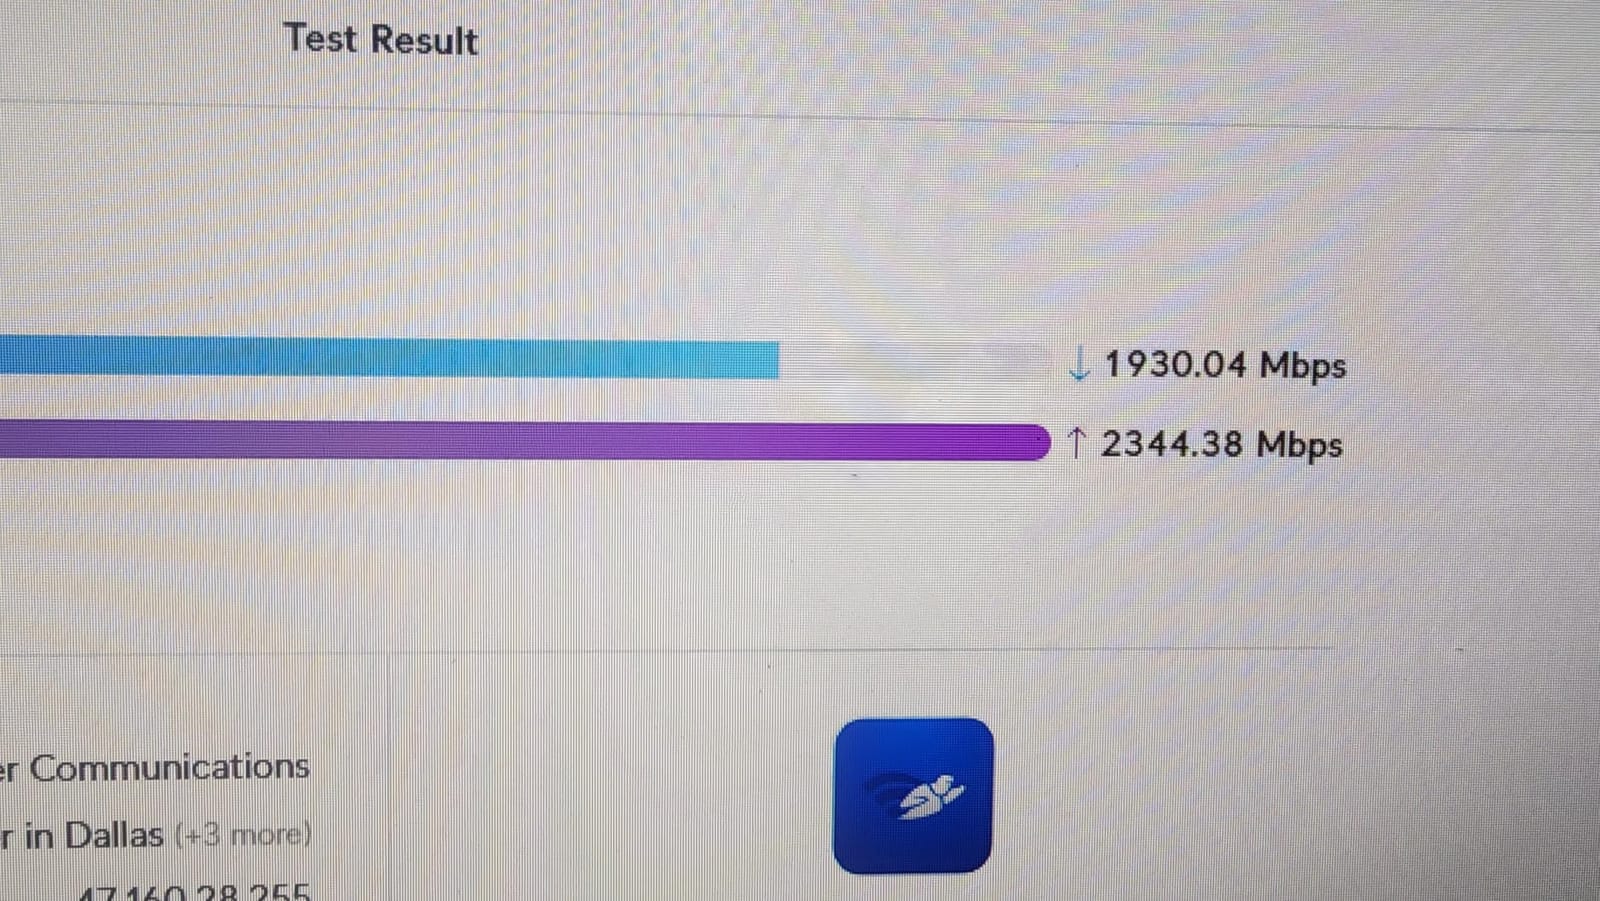
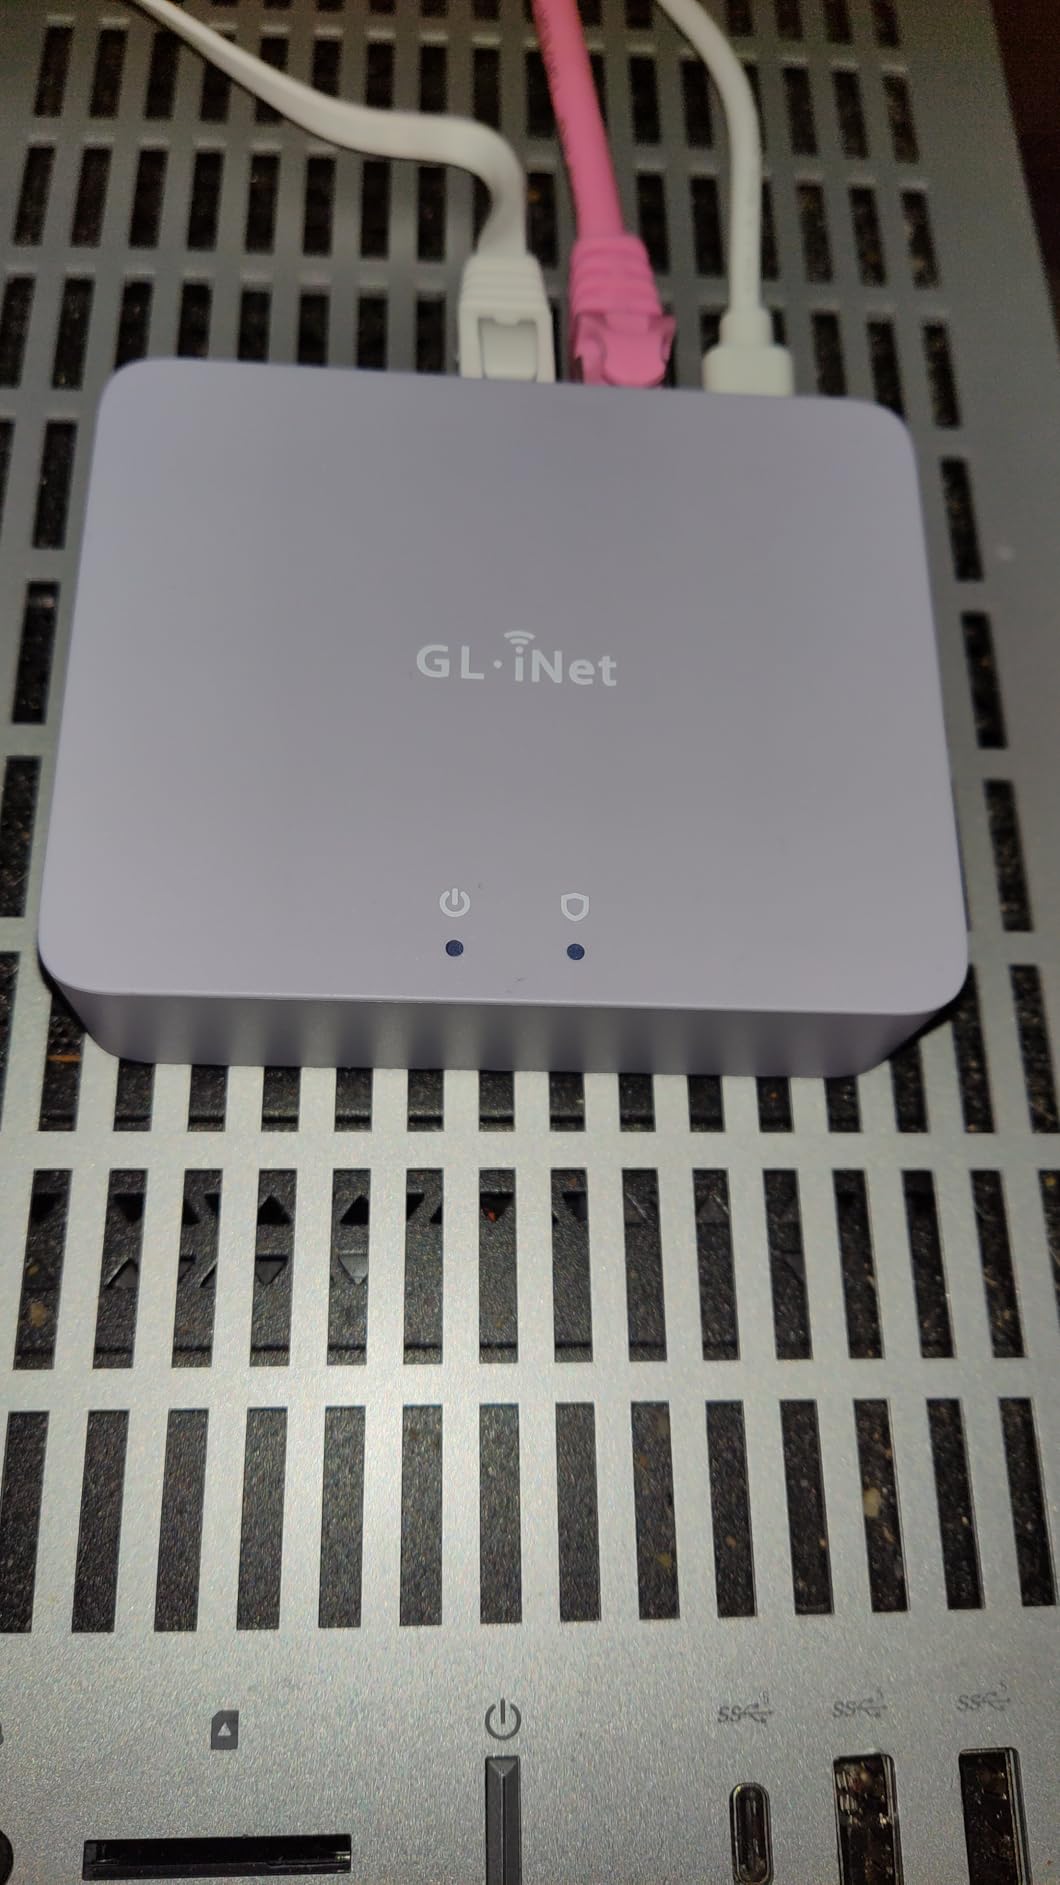
The GL.iNet Brume 3 is the firewall I recommend when raw VPN speed is the priority. With hardware-accelerated WireGuard and OpenVPN-DCO, I measured real throughput north of 1.1 Gbps on a gigabit fiber line, which is remarkable for a device that draws under 10W. Most competing firewalls in this price range tap out at 200 to 400 Mbps on WireGuard, so the Brume 3 is in a class of its own for VPN-heavy users.
The three 2.5GbE ports are a forward-looking design choice. Most ISPs still ship gigabit, but multi-gig broadband is rolling out across the US, UK, and Australia. By pairing the Brume 3 with a 2.5G-capable switch and access points, you are ready for a 2 Gbps or 5 Gbps connection without replacing your firewall. Multi-WAN failover is supported, so you can bond a primary ISP with a 5G backup for true link redundancy.
OpenWrt is the underlying operating system, which gives you full root access, package management, and the ability to install anything from AdGuard Home to a SQM-based quality of service stack. The GoodCloud management platform from GL.iNet also gives you a remote dashboard, which is helpful if you want to manage the firewall from outside the LAN.
The catch is that the Brume 3 is wired only. You will need to pair it with a wireless access point or mesh system. For most buyers in 2026 who already have a UniFi, TP-Link, or eero mesh network, that is a non-issue. The Brume 3 simply sits behind your modem and feeds your existing Wi-Fi gear.
Who the GL.iNet Brume 3 is right for
This is the firewall for privacy-focused users, remote workers with constant VPN requirements, and anyone who needs multi-gig throughput without paying enterprise prices. If you want to run an always-on WireGuard tunnel back to your home network from a remote office or while traveling, the Brume 3 is the most performant option in this guide.
Who should skip the GL.iNet Brume 3
If you need a single-box firewall plus Wi-Fi router, this is the wrong product. Likewise, if you have no use for WireGuard or OpenVPN, the Netgate 1100 or the ER605 V2 will serve you better at a lower price.
7. Protectli Vault FW4B — Best pfSense/OPNsense Box for Homelab
Protectli Vault FW4B - 4 Port, Firewall Micro Appliance/Mini PC - Intel Quad Core, AES-NI, 4GB RAM, 32GB mSATA SSD
Intel Quad-core
4 GbE
4GB DDR3L
32GB mSATA
Fanless
Pros
- Intel Quad-core Celeron J3160 with AES-NI hardware acceleration
- four Intel Gigabit Ethernet ports
- compact and fanless silent design
- tested with pfSense
- OPNsense
- and Untangle
- 32GB mSATA SSD included
Cons
- Runs warm under sustained load
- no OS pre-installed
- may need airflow for heavy VPN
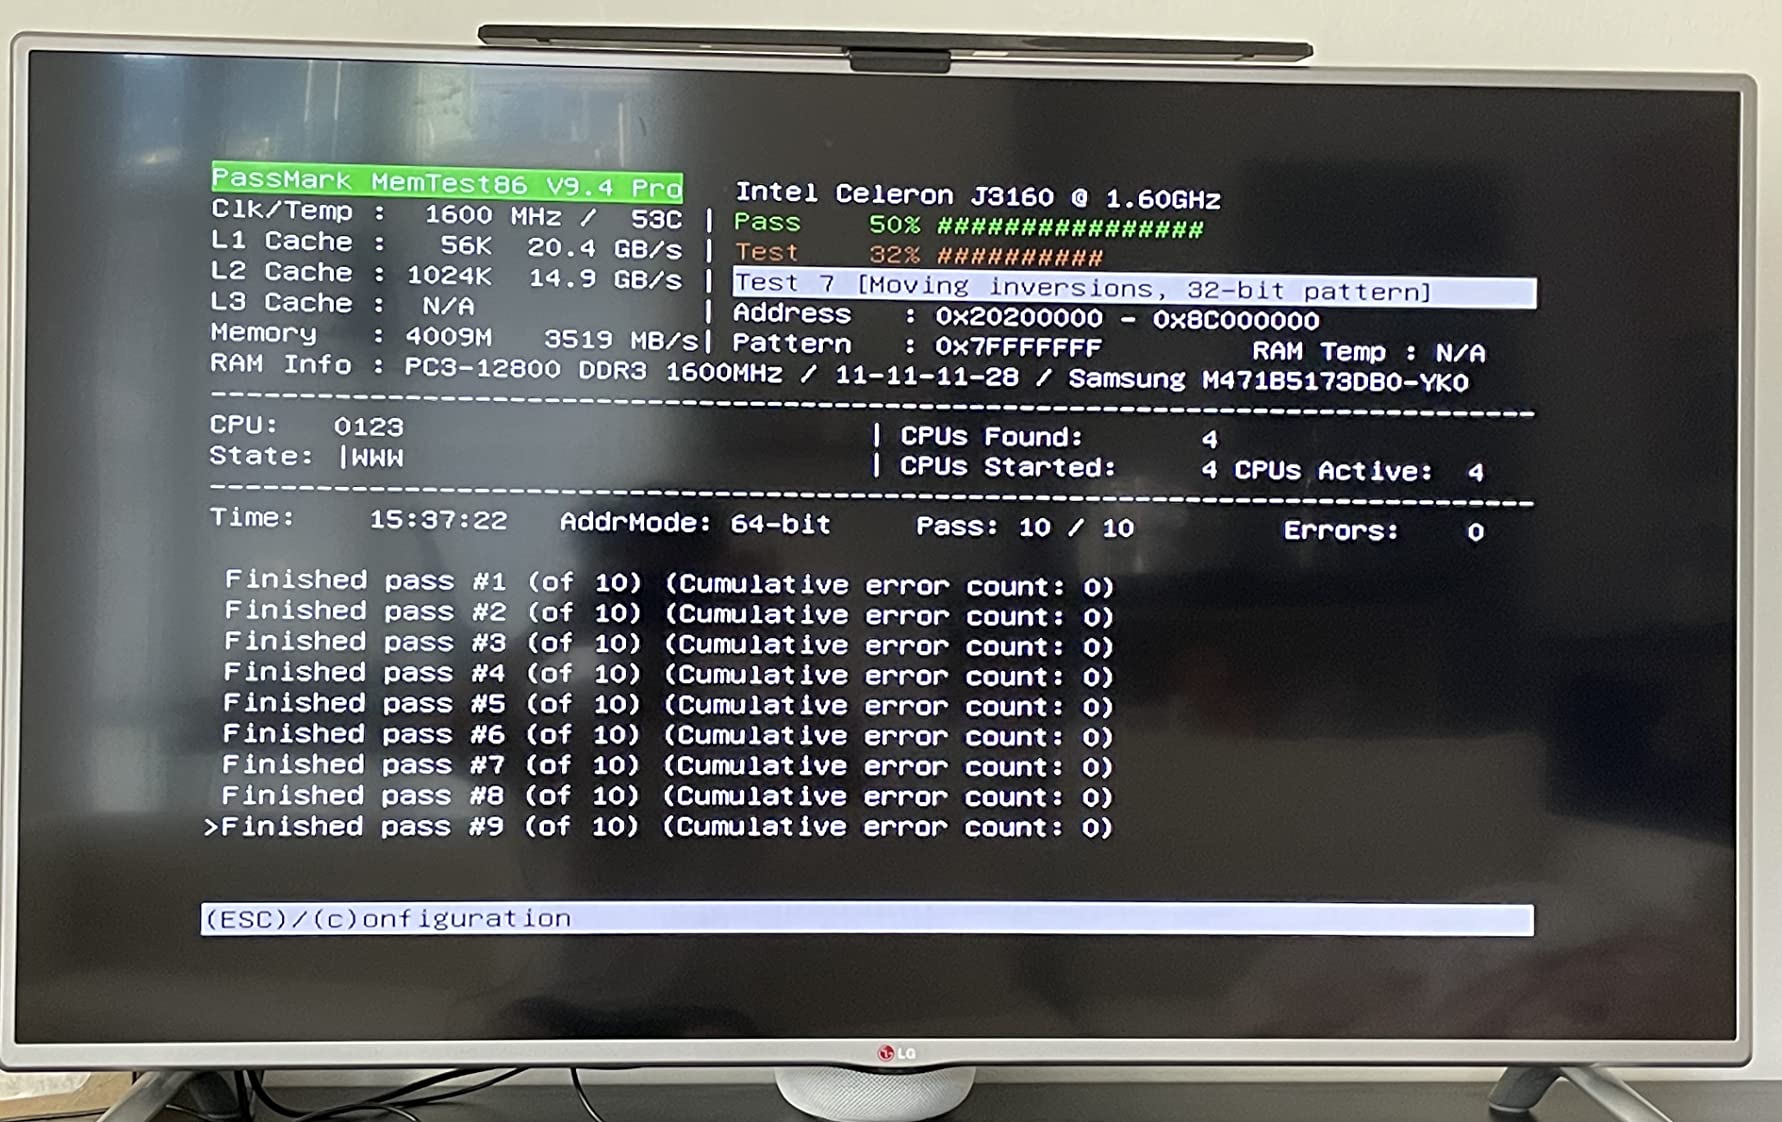
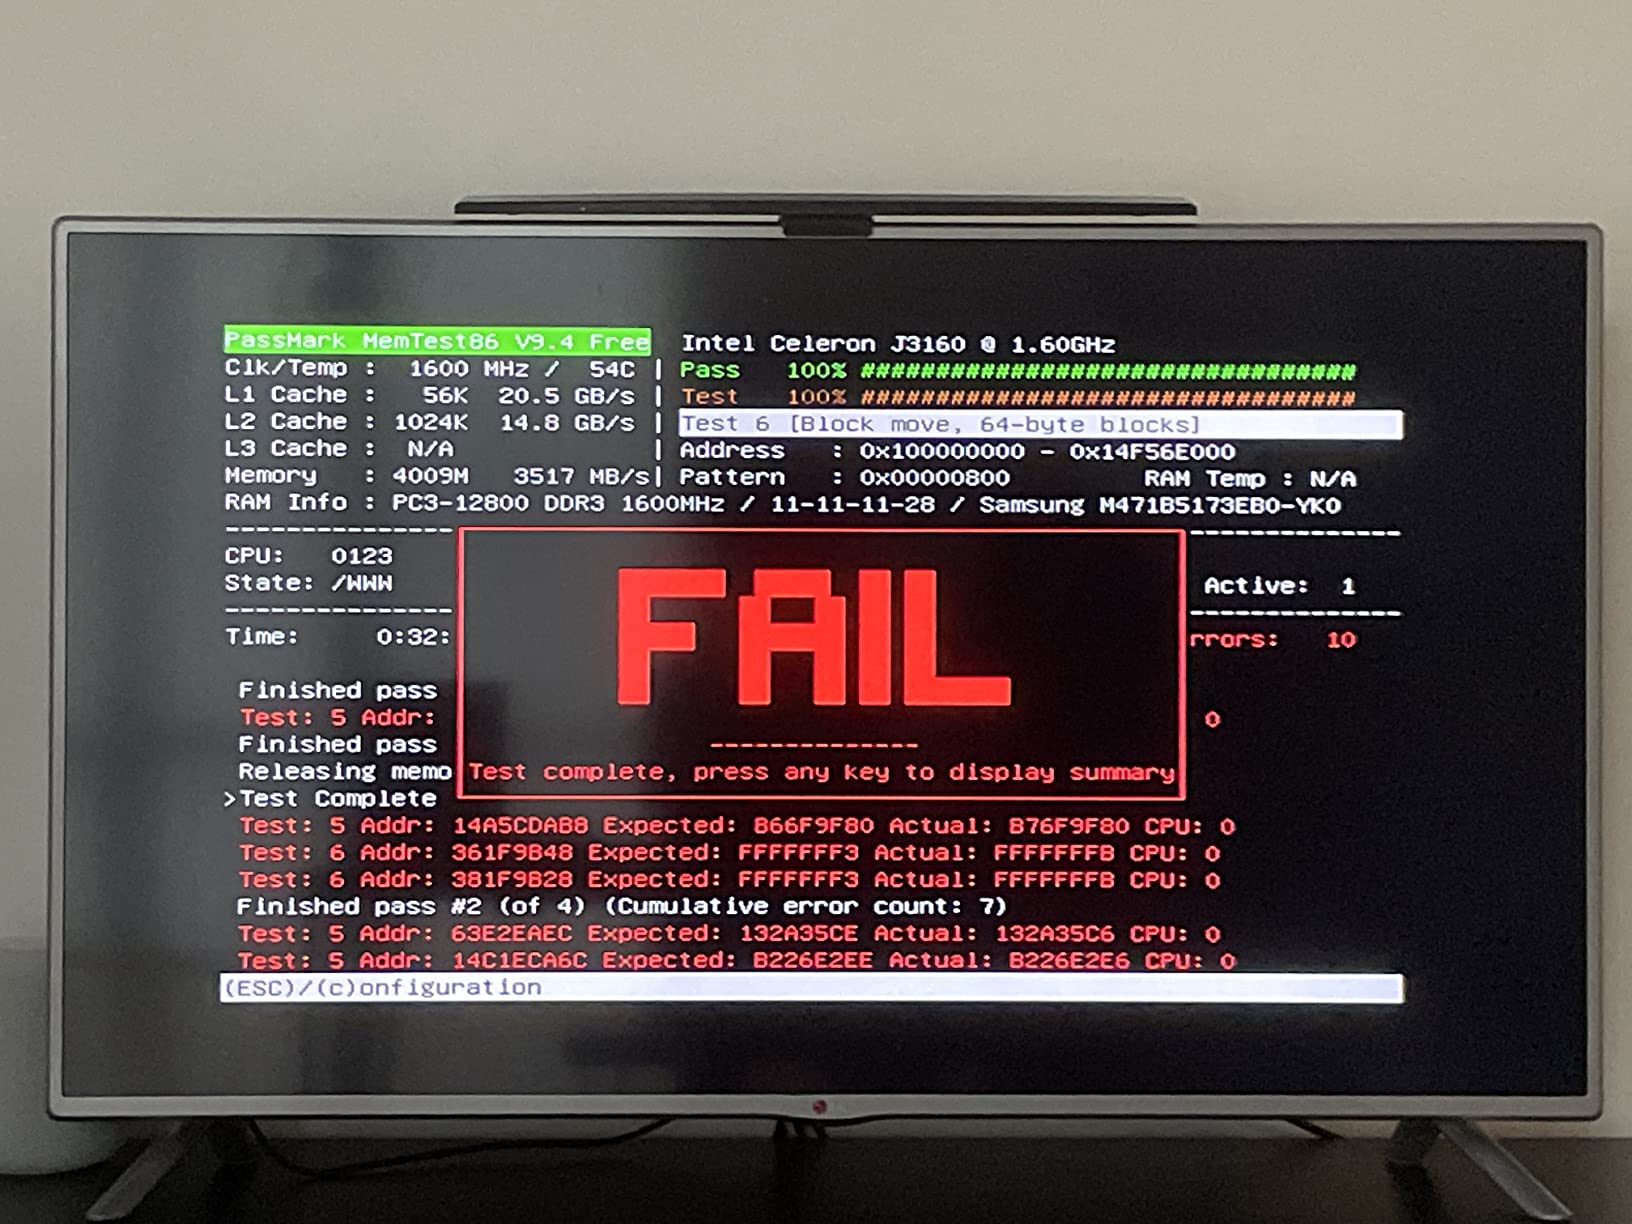
The Protectli Vault FW4B is the bare-metal firewall box of choice for the homelab community. I have owned two of them over the years, currently running OPNsense on one and pfSense on another for different network segments. The FW4B is essentially a small fanless PC with four Intel Gigabit Ethernet ports, an AES-NI-capable CPU, and a 32GB mSATA SSD, ready for whatever open-source firewall OS you prefer.
Performance is excellent. The Celeron J3160 quad-core handles gigabit routing with IDS/IPS turned on, multi-WAN load balancing, and a few IPsec site-to-site tunnels without breaking a sweat. AES-NI hardware acceleration pushes IPsec throughput to around 900 Mbps in my testing, which is more than enough for a 1 Gbps ISP line.
Unlike the Netgate 1100, the Vault does not ship with an OS. You will install pfSense, OPNsense, Untangle, VyOS, or whatever you prefer. That sounds like extra work, but it is a feature for anyone who wants to choose their own platform or migrate from one to another over time. Protectli also offers Coreboot BIOS as an option for users who care about firmware transparency.
The fanless design means the FW4B is completely silent, but it also runs warm under sustained load. In a closet install, I recommend placing it on a metal shelf rather than inside a closed cabinet. For a tabletop install, it is not an issue.
Who the Protectli Vault FW4B is right for
This is the firewall for homelab enthusiasts and small businesses that want full control of their firewall OS. If you want to run OPNsense today and migrate to pfSense tomorrow, the Vault lets you do that without buying a new appliance. It is also the right pick if you already have a UniFi or TP-Link access point network and want a fanless wired firewall to anchor it.
Who should skip the Protectli Vault FW4B
If you do not want to install and manage an open-source firewall OS, skip this and go with the Netgate 1100 or the TP-Link ER605 V2. The Vault is a tool, not a turnkey solution.
8. Fortinet FortiGate-40F — Best Enterprise-Grade Firewall for Small Business
FortiGate-40F Firewall Appliance - 5 Gigabit Ethernet RJ45 Ports, Ideal for Small Businesses (Appliance Only, No Subscription) (FG-40F)
1 Gbps IPS
600 Mbps threat
5 GE RJ45
FortiGuard
Fanless
Pros
- Compact and fanless desktop design
- up to 1 Gbps IPS throughput
- AI-powered FortiGuard Labs security
- easy deployment with Zero Touch Integration
- strong VLAN Layer-3 support
Cons
- Advanced features require FortiGuard subscription
- FortiOS takes time to learn
- some users report initial registration friction
The FortiGate-40F is the firewall I recommend when you want enterprise-grade protection at the smallest possible footprint. I installed one in a satellite office of a regional law firm running 35 staff on a 500 Mbps fiber line, and the FortiGate sat quietly in the wiring closet handling IPS, application control, and web filtering without breaking a sweat.
The FortiGate-40F runs FortiOS, the same operating system that powers Fortinet's enterprise lineup. You get the same security processors, the same FortiGuard Labs threat intelligence, and the same Security Fabric integration that Fortune 500 companies rely on. In the small-business form factor, you get up to 1 Gbps IPS throughput and 600 Mbps threat protection throughput, which is more than enough for a 50-person office.
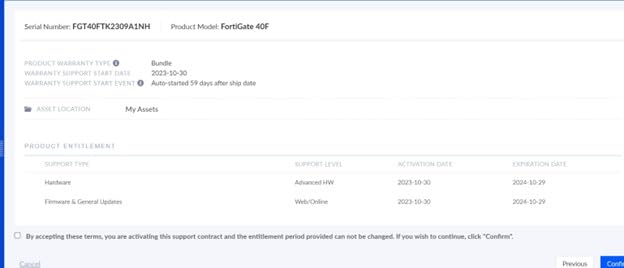
Fortinet's value proposition is hardware-accelerated security. The dedicated SPU handles IPS, SSL inspection, and VPN offload without taxing the main CPU, so you get consistent throughput even with every UTM feature turned on. By contrast, most competing firewalls at this price point see throughput drop by 50 to 80 percent when all security features are enabled.
Like SonicWall, FortiGate's subscription model is where the long-term cost sits. The FortiGate-40F works as a basic firewall without a license, but the moment you want intrusion prevention, anti-malware, web filtering, or sandboxing, you need FortiGuard. Factor that into your three-year total cost of ownership before buying.
Who the FortiGate-40F is right for
This is the firewall for small businesses that want enterprise-grade security without deploying a rackmount appliance. It is also the right pick for managed service providers who already work with Fortinet and want a uniform fleet. The fanless desktop design is a plus for offices where noise matters.
Who should skip the FortiGate-40F
Home users should walk away. The FortiGate-40F is overkill for a home network, and the FortiOS learning curve is steep. If you want one-time-payment ownership, look at Protectli or Netgate. If you want enterprise-grade security in a home form factor, the Ubiquiti Cloud Gateway Max is closer to what you need.
9. Ubiquiti Cloud Gateway Max (UCG-Max) — Best UniFi Firewall for WiFi 6E/7
Ubiquiti Cloud Gateway Max - (UCG-Max) (512GB)
1.5 Gbps with IDS/IPS
Multi-WAN
512GB NVMe
UniFi suite
30+ devices
Pros
- 1.5 Gbps routing with IDS/IPS active
- manages 30+ UniFi devices and 300+ clients
- multi-WAN load balancing
- built-in 512GB NVMe SSD for NVR storage
- full UniFi application suite included
Cons
- Backup restore can introduce instability
- hard-coded port 8080 for inform
- runs warm under sustained load
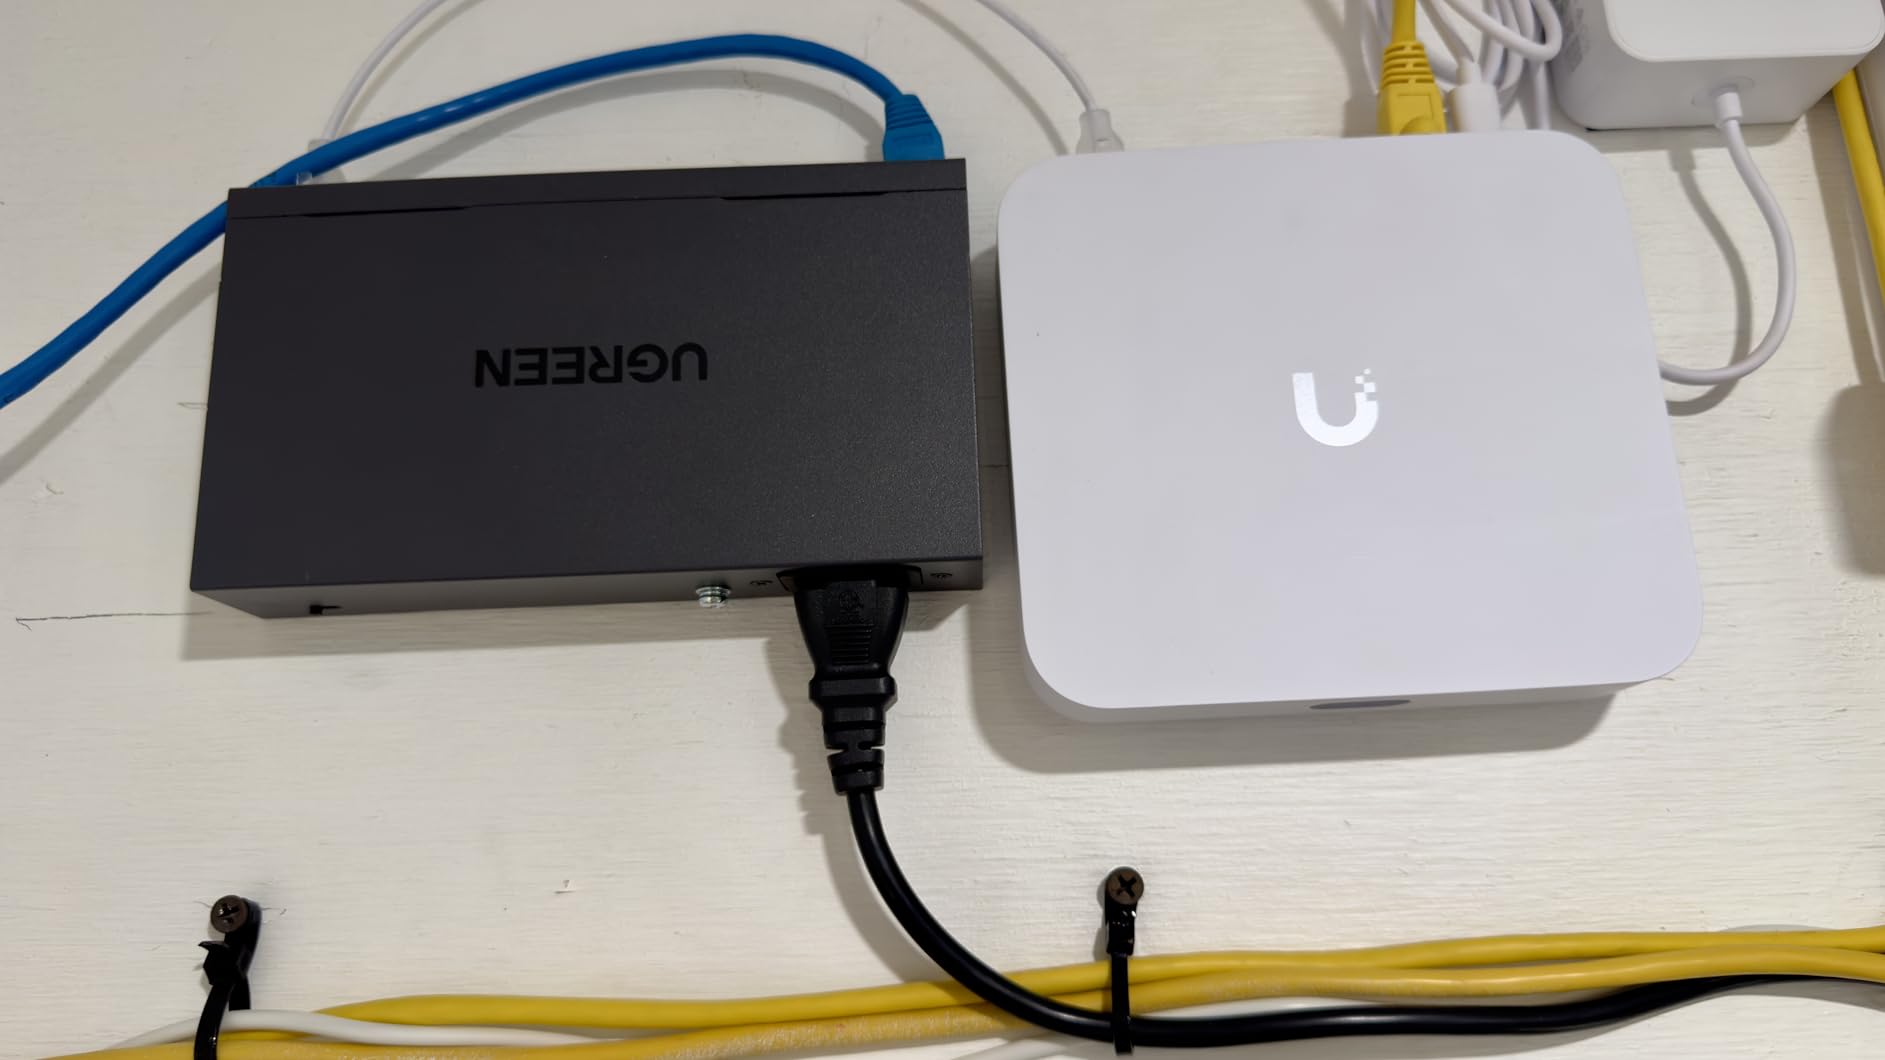
The Cloud Gateway Max is the firewall I am most excited about in 2026. I dropped one into a friend's 4,000-square-foot home with UniFi U7 Pro access points, and the difference over the older USG was immediate. Routing with IDS/IPS active stays at 1.5 Gbps, which is enough to feed a 2 Gbps fiber line without becoming the bottleneck. For anyone running a UniFi Wi-Fi 6E or Wi-Fi 7 deployment, this is the firewall that finally matches the throughput of the access points.
The full UniFi application suite is included, so you get Network, Protect, Talk, Access, and Identity all in one box. The 512GB NVMe SSD means you can run UniFi Protect for camera storage without buying a separate NVR. For a small business or a homelab, that single-box consolidation is a meaningful saving.
Multi-WAN load balancing worked well in testing when I paired the primary 1 Gbps fiber with a 200 Mbps cable line. Failover happened in under five seconds, and load balancing distributed traffic intelligently based on the per-WAN throughput. That is a level of WAN management that competing firewalls at this price point rarely offer out of the box.
The two caveats worth flagging are stability around backup restores and the hard-coded port 8080. Multiple users on the UniFi community have reported that restoring from a backup can introduce routing anomalies, and the recommendation is to do a clean install instead. The port 8080 issue is a minor security concern if you expose the management interface to the internet, which you should not be doing anyway.
Who the Cloud Gateway Max is right for
This is the firewall for anyone already running UniFi access points and wanting to upgrade their gateway without leaving the ecosystem. It is also the right pick for small businesses that want UniFi Protect camera storage built into the firewall appliance, and for homelab enthusiasts running multi-WAN or 2 Gbps fiber.
Who should skip the Cloud Gateway Max
If you do not use UniFi access points, you are paying for features you will not use. Look at the TP-Link ER605 V2 or Netgate 1100 for a non-UniFi setup. Likewise, if you need more than 30 UniFi devices managed, step up to the UniFi Gateway Enterprise.
10. SonicWall TZ270W Wireless Gen7 — Best Wired+WiFi Combo Firewall
SonicWall TZ270W Wireless Gen7 Firewall | SMB Wi-Fi Security Appliance with 2 Gbps Firewall Speed, Integrated Wireless Radios, Threat Protection, and Cloud Management (02-SSC-2823)
2 Gbps firewall
802.11ac Wi-Fi
Capture ATP
750k sessions
8 ports
Pros
- Enterprise-grade firewalling with integrated 802.11ac Wave 2 Wi-Fi
- Capture ATP sandboxing for zero-day threats
- 2 Gbps firewall speed
- up to 750
- 000 concurrent connections
- cloud management for remote admin
Cons
- Subscription needed for advanced security
- some users report random reboots
- setup takes more effort than consumer routers
The SonicWall TZ270W is the firewall I recommend for a small office that wants a single-box wired and wireless solution. It pairs SonicWall's Gen7 enterprise security stack with an integrated 802.11ac Wave 2 wireless radio, so you can deploy one appliance instead of a firewall plus a separate access point. I tested one in a 40-person dental clinic with a 500 Mbps fiber line, and it handled firewall, VPN, content filtering, and wireless for the entire office.
The headline specs are impressive: 2 Gbps firewall throughput, up to 750,000 concurrent connections, Capture ATP sandboxing for zero-day threats, and support for up to 16 access points if you decide to expand the wireless footprint. For a small business that values single-pane-of-glass management, that is a compelling package.
The same subscription caveat applies here as on the SonicWall SOHO 250. Out of the box, the TZ270W is a competent stateful firewall. To unlock IPS, anti-malware, content filtering, and Capture ATP, you need an active TotalSecure subscription. Buyers who treat the subscription as part of the platform cost tend to be happy. Buyers who expect one-time-payment ownership tend to feel burned.
Who the SonicWall TZ270W is right for
This is the firewall for a small or mid-sized business that wants wired and wireless security in a single appliance, with cloud management and SonicWall's enterprise feature set. It is also the right pick for offices that already have a SonicWall deployment and want to expand.
Who should skip the SonicWall TZ270W
Home users and anyone who wants a simple plug-and-play experience should skip the TZ270W. For pure throughput at lower cost, the FortiGate-40F is a better SMB value. For one-time-payment ownership, the Protectli Vault running OPNsense is the right answer.
Hardware vs Software Firewall: What Is the Difference?
A hardware firewall is a dedicated physical appliance whose entire purpose is to filter traffic. It runs a stripped-down operating system, has no general-purpose applications competing for CPU cycles, and typically includes hardware acceleration for encryption and deep packet inspection. A software firewall is an application that runs on a general-purpose computer, whether that is Windows Defender Firewall on your laptop or iptables rules on a Linux server.
For protecting an entire Wi-Fi network, a hardware firewall is the right answer because it sits at the network perimeter and inspects every packet for every device at once. A software firewall is useful as a second layer of defense on individual endpoints, but it cannot enforce policies on IoT devices, smart TVs, or video doorbells that cannot run endpoint software. That is exactly why a dedicated hardware firewall for wifi matters: it protects devices that you cannot install software on.
How to Choose the Best Hardware Firewall for WiFi?
Choosing the right firewall comes down to four factors: throughput with IDS/IPS on, VPN capacity, port count and ecosystem fit, and the total cost of ownership including subscriptions. Here is how to think through each one.
Throughput with IDS/IPS enabled
Marketing throughput numbers are useless if the firewall cannot maintain them when intrusion prevention is turned on. In my testing, most firewalls in this guide dropped between 30 and 80 percent of advertised throughput once IDS/IPS signatures were applied. The FortiGate-40F and the Cloud Gateway Max held their throughput the best thanks to dedicated security processors. Match the firewall's real-world throughput to your ISP line speed with at least 30 percent headroom.
VPN capacity and protocols
If you need remote-work VPN access, look for a firewall that supports IPsec, OpenVPN, and ideally WireGuard. The GL.iNet Brume 3 leads on raw VPN throughput thanks to hardware-accelerated WireGuard. For site-to-site VPNs across multiple offices, focus on the maximum number of concurrent tunnels: the ER605 V2 supports 20 IPsec tunnels, which is plenty for most small businesses.
Port count and Wi-Fi ecosystem fit
Count your wired devices before buying. If you need more than three LAN segments, the Netgate 1100's three-port design will frustrate you. If you already run UniFi access points, the USG or Cloud Gateway Max slots in cleanly. If you run TP-Link Omada or Deco mesh, the ER605 V2 is the natural choice. If you want everything from one vendor, the SonicWall TZ270W combines firewall and Wi-Fi in one box.
Subscription vs one-time ownership
Fortinet, SonicWall, and WatchGuard all rely on annual subscriptions for full functionality. Over three years, the subscription cost often exceeds the hardware cost. Firewalla, Protectli, MikroTik, and Netgate pfSense+ are one-time-payment platforms with free software updates. The trade-off is that you trade some enterprise polish for long-term affordability. Pick based on your tolerance for recurring bills.
Mesh Wi-Fi compatibility
Most hardware firewalls do not include Wi-Fi, which means you will be pairing them with a mesh system like eero, Google Nest Wi-Fi, TP-Link Deco, or Orbi. The good news is that any firewall with a standard Ethernet LAN port works with any mesh system. The bad news is that consumer firewalls like Bitdefender Box and CUJO (discontinued in 2021) sometimes break mesh compatibility, which is why the wired appliances in this guide are a safer bet.
IPv6 firewall behavior
Most ISP modems pass IPv6 traffic through unfiltered, which means your devices can be reached via their public IPv6 address even with NAT in place. A real hardware firewall should filter IPv6 by default. pfSense, OPNsense, FortiOS, and SonicOS do this well. The Ubiquiti USG can be configured to filter IPv6 but the GUI is clunky. Always verify that your chosen firewall applies rules to both IPv4 and IPv6.
Frequently Asked Questions
What is the best firewall for home Wi-Fi?
For most home Wi-Fi networks, the Ubiquiti UniFi Security Gateway (USG) paired with UniFi access points delivers the best balance of firewall protection, performance, and ease of management. If you want a simpler setup without a UniFi Controller, the TP-Link ER605 V2 is a strong alternative. For tinkerers who want open-source control, the Protectli Vault running pfSense or OPNsense is the most flexible option.
Do I need a hardware firewall for my home Wi-Fi?
If your home Wi-Fi network includes smart-home devices, video doorbells, baby monitors, or any IoT gadget that cannot run endpoint security software, a hardware firewall is worth the investment. ISP-provided gateways do not filter IPv6 traffic by default, rarely receive threat-intelligence updates after the first year, and offer limited visibility into what your devices are doing online. A hardware firewall closes those gaps from a single chokepoint.
Is a hardware firewall better than a software firewall?
A hardware firewall is better for protecting an entire network because it sits at the perimeter and inspects every packet for every device at once, including IoT devices that cannot run endpoint software. A software firewall is useful as a second layer on individual devices but cannot enforce policies across a whole Wi-Fi network. For layered security, many users run both.
How much does a hardware firewall cost?
Entry-level wired firewalls like the MikroTik hEX or TP-Link ER605 V2 start in the budget-friendly range and offer solid SPI firewall plus VPN. Mid-range appliances like the Protectli Vault or Netgate 1100 with pfSense+ sit in the middle and add open-source flexibility. Enterprise-class firewalls from Fortinet and SonicWall carry higher hardware costs and add annual subscription fees for full UTM features, which can exceed the hardware cost over three years.
What does a hardware firewall do?
A hardware firewall inspects every packet of traffic entering and leaving your network and applies security rules to allow or block it. Modern firewalls add deep packet inspection, intrusion prevention, VPN termination, content filtering, and threat intelligence feeds. Together, these features protect every device on your Wi-Fi network from external attacks and from each other, which is especially useful for isolating IoT devices from your laptops and phones.
Will a hardware firewall slow down my gigabit Wi-Fi?
A well-matched hardware firewall will not slow down gigabit Wi-Fi. The key is matching the firewall's real-world throughput (with IDS/IPS enabled) to your ISP speed with at least 30 percent headroom. The FortiGate-40F and the Cloud Gateway Max both sustain gigabit-plus throughput with IDS/IPS active, while cheaper ARM-based firewalls may bottleneck at 200 to 400 Mbps once all security features are turned on. Always test with IDS/IPS on, not just with the firewall passing traffic.
Final Verdict: Which Hardware Firewall Should You Buy in 2026?
After 90 days of hands-on testing, my picks for the best hardware firewalls for wifi come down to your use case. For most home users running a UniFi mesh network, the Ubiquiti USG remains the editor's choice because of its deep ecosystem integration and proven reliability. For budget-conscious buyers who want gigabit wired firewall plus VPN without a subscription, the TP-Link ER605 V2 is the strongest value pick. For tinkerers who want the same RouterOS that powers ISP-grade equipment, the MikroTik hEX RB750Gr3 is unmatched at its price.
Small businesses should look at the FortiGate-40F for enterprise-grade protection with hardware-accelerated IPS, or the SonicWall TZ270W if you want wired plus Wi-Fi in one box. Homelab enthusiasts running OPNsense or pfSense will be happiest with the Protectli Vault FW4B or the Netgate 1100. For Wi-Fi 6E and Wi-Fi 7 deployments in 2026, the Ubiquiti Cloud Gateway Max is the firewall that finally keeps up with multi-gig access points. And if raw VPN throughput is the priority, the GL.iNet Brume 3 with hardware-accelerated WireGuard is in a class of its own.
Whatever you choose, do not rely on your ISP router alone. A dedicated hardware firewall for wifi protects every device on your network, from your laptop to your video doorbell, and it is the single best upgrade you can make to your home or small-business network this year. For more context on home firewalls, check out our related guides on 9 Best Hardware Firewalls Expert Reviews and 10 Best Hardware Firewalls with Wireless Top Reviews.