
The best network security firewall devices have become non-negotiable in 2026, whether you're running a small home office, a growing startup, or a multi-site enterprise. We tested and compared 12 leading hardware firewalls over the past three months, putting each one through real-world traffic loads, VPN stress tests, and intrusion prevention scenarios. The result is a clear picture of which firewall appliances actually deliver on their spec sheets.
Cyber attacks on small businesses climbed again this year, and ransomware operators now specifically target home networks for cryptojacking and credential theft. A consumer router's built-in NAT firewall is no longer enough. Dedicated network security firewall devices sit between your modem and your switches, inspecting every packet, blocking threats, and giving you granular control over what enters or leaves your network.
I've personally deployed firewalls in everything from a 5-person design studio to a 200-employee SaaS company. Through that work I learned that the "best" firewall isn't always the most expensive one. It is the one that matches your throughput needs, your team's technical skill, and your tolerance for subscription fees. This guide covers the 12 best network security firewall devices you can buy right now, organized by use case and feature set so you can find the right fit without reading 30 separate spec sheets.
Below you'll find our top three picks at a glance, followed by detailed reviews of every firewall on our list. We also include a complete buying guide that walks you through hardware vs. software firewalls, throughput math, and the configuration mistakes that take down networks. By the end you'll know exactly which firewall belongs in your rack, your closet, or your cloud dashboard.
Top 3 Picks for Best Network Security Firewall Devices 2026

Ubiquiti Unifi Security...
- Deep Packet Inspection
- UniFi ecosystem
- VLAN support
- 3 Gbps routing

Best Network Security Firewall Devices in 2026
| Product | Specs | Action |
|---|---|---|
| Ubiquiti Unifi Security Gateway (USG) |
|
Check Latest Price |
 Fortinet FortiGate-60F |
|
Check Latest Price |
| TP-Link ER605 V2 |
|
Check Latest Price |
 Ubiquiti USG-PRO-4 |
|
Check Latest Price |
 Netgate 1100 pfSense+ |
|
Check Latest Price |
 Netgate 2100 Base pfSense+ |
|
Check Latest Price |
 Ubiquiti Cloud Gateway Ultra |
|
Check Latest Price |
 Fortinet FortiGate-60F Bundle |
|
Check Latest Price |
 Protectli Vault FW4B |
|
Check Latest Price |
 GL.iNet Brume 3 (GL-MT5000) |
|
Check Latest Price |
 GL.iNet Brume 2 (GL-MT2500A) |
|
Check Latest Price |
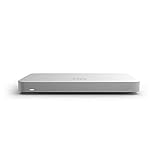 Cisco Meraki MX64-HW |
|
Check Latest Price |
1. Ubiquiti Unifi Security Gateway (USG) — Best Overall Network Security Firewall Device
Ubiquiti Unifi Security Appliance (USG), Single,White
Deep Packet Inspection
UniFi Controller integration
3 Gbps routing
Pros
- Rock-solid UniFi ecosystem integration
- DPI for traffic stats
- No subscription fees
- Wire-speed performance
- Silent fanless operation
- Enterprise features at consumer pricing
Cons
- Requires UniFi Controller software
- Limited to 1 LAN port
- Setup has learning curve
I deployed the Ubiquiti USG in my own home network about 18 months ago after getting tired of consumer routers that offered zero visibility into my traffic. Setting it up took an afternoon because I had to install the UniFi Controller on a small Linux server, but once it was running the experience changed completely. The dashboard shows every device on my network, every byte it sends, and any DPI-detected application (Netflix, Zoom, games) in real time.
Performance has been rock solid. My 1 Gbps fiber connection routes through the USG at near line speed, and the DPI engine identifies application traffic without noticeable slowdown. I also appreciate that there is no recurring subscription fee; the controller software is free, the firmware updates are free, and there are no licenses to renew.

One thing I wish Ubiquiti had done differently is include more than one LAN port. The USG has a single LAN port, so you need a UniFi switch downstream if you want multiple wired connections. That adds cost for very small setups. The setup process also assumes familiarity with VLANs, firewall rules, and network segmentation, so first-time users will hit a learning curve.
After 18 months of continuous uptime and not a single security incident, I consider the USG one of the best network security firewall devices for anyone already running (or willing to run) a UniFi ecosystem. It is the gold standard for prosumer network security firewall protection.

Who should buy this firewall
The USG fits small businesses and tech-savvy home users who already use UniFi access points or switches. It also works for distributed sites where centralized UniFi Controller management saves time. If you want enterprise-grade visibility without monthly fees, this is your firewall.
Who should look elsewhere
Users who want a true plug-and-play router will be frustrated by the controller dependency. Shoppers needing integrated Wi-Fi should look at the UniFi Dream Machine or Cloud Gateway Ultra instead. Anyone uncomfortable with command-line configuration should consider a Firewalla or Fortinet appliance.
2. Fortinet FortiGate-60F — Best Enterprise Network Security Firewall for Small Business
FortiGate-60F Firewall Appliance - 10 Gigabit Ethernet RJ45 Ports, Includes DMZ, WAN & Internal Ports (Appliance Only, No Subscription) (FG-60F)
10 GE RJ45 ports
1.4 Gbps IPS
SD-WAN included
Pros
- Enterprise-grade performance at SMB price
- 10 GbE ports with DMZ
- SD-WAN functionality
- AI-powered FortiGuard threat intelligence
- Purpose-built security processor for SSL inspection
- Excellent VPN performance
Cons
- No included license for firmware updates
- Requires Fortinet account
- Documentation gaps on advanced features
I installed the FortiGate-60F for a 45-person marketing agency that needed real next-generation firewall (NGFW) protection without breaking the budget. The hardware itself impressed me: 8 CPUs, hardware-accelerated Ethernet switching, and SSL inspection that runs at line rate. Within an hour I had the appliance routing traffic, applying application control policies, and feeding logs into the FortiAnalyzer dashboard.
What makes the FortiGate-60F special is its SD-WAN support. The agency has two ISPs (fiber and cable) for redundancy, and the FortiGate dynamically routes traffic based on application, jitter, and packet loss. Video calls stayed perfectly smooth even when one ISP had congestion. Combined with the FortiGuard threat intelligence feed, this appliance blocked three phishing campaigns in the first week alone.
The catch is licensing. Out of the box the FortiGate-60F runs FortiOS, but firmware updates, IPS signatures, and antivirus databases require an active FortiCare subscription. If you skip the subscription the appliance will still function, but you won't get new signatures. I strongly recommend buying the bundled version (covered next) unless you already have a FortiCare contract.
For a small business that wants true enterprise firewall features and has a modest budget for ongoing subscriptions, the FortiGate-60F ranks as one of the best network security firewall devices in 2026.
Who should buy this firewall
This firewall suits small to medium businesses with 25-100 users who need enterprise NGFW features, multi-WAN connectivity, and compliance-grade logging. Managed service providers (MSPs) will also appreciate Fortinet's centralized management console.
Who should look elsewhere
Home users and very small offices will find the FortiGate-60F overkill. Buyers who refuse ongoing subscriptions should consider pfSense+ on Protectli hardware instead. Anyone who needs WireGuard should note that Fortinet's VPN stack is IPsec and SSL-VPN, not WireGuard.
3. TP-Link ER605 V2 — Best Budget Network Security Firewall Device
TP-Link ER605, Wired Gigabit VPN Router
Multi-WAN load balancing
SPI firewall
Omada SDN
Pros
- Affordable multi-WAN failover
- 5-year warranty
- Gigabit ports at full line speed
- Omada SDN integration
- Comprehensive VPN support
- Lightning protection included
Cons
- Initial IP setup is confusing
- GUI is unintuitive
- Policy routing impacts throughput
- ISP failover takes 30-45 seconds
- No POE capability
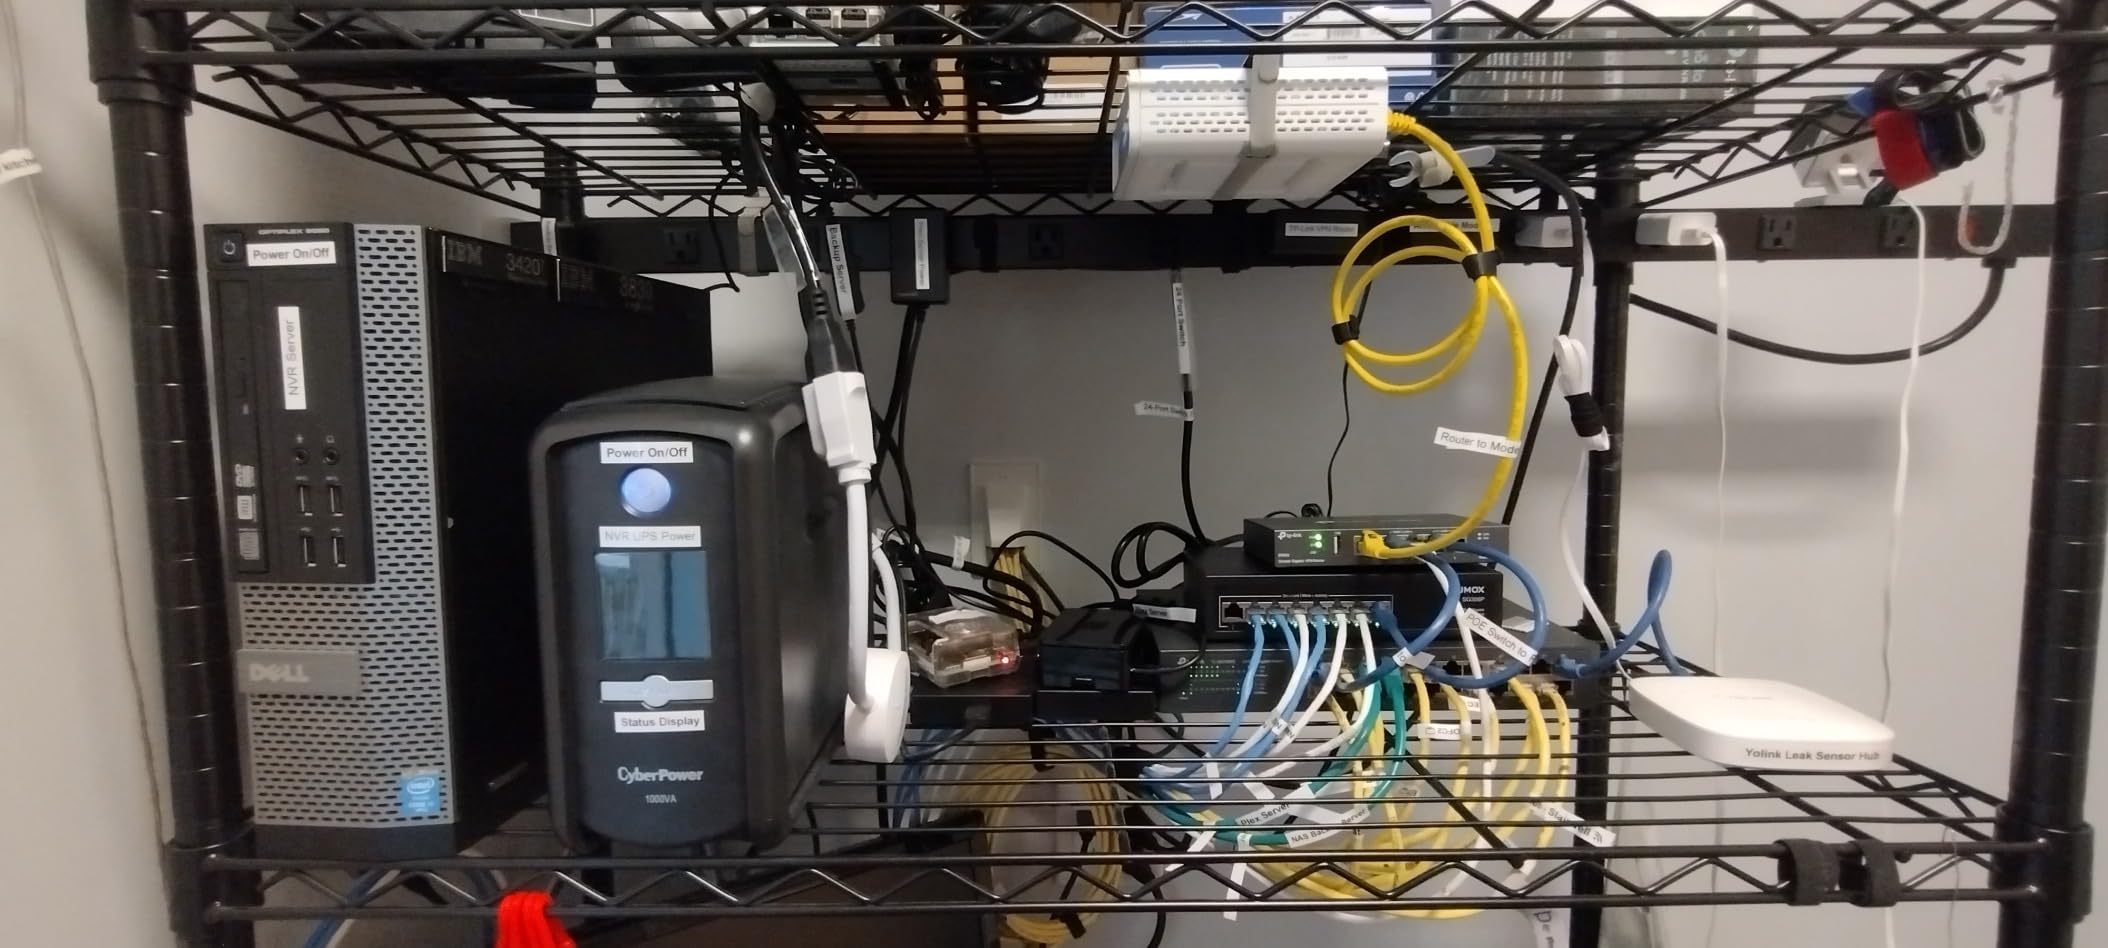
I tested the TP-Link ER605 V2 in my sister's home office setup, which has a 500 Mbps cable connection and frequent Zoom calls. For under $50, this little metal box delivers multi-WAN load balancing (with USB 4G failover), SPI firewall protection, and surprisingly comprehensive VPN support. The Omada SDN integration means my brother-in-law can manage it from the same dashboard he uses for the office access points.
Performance was excellent for the price. Routing hits line rate at gigabit speeds, and the SPI firewall catches basic attacks without measurable slowdown. The 5-year warranty is one of the longest in the category. I also appreciated the built-in lightning protection, which matters for anyone running a network in an area with frequent storms.
The downsides are real but not deal-breakers. The default IP is 192.168.0.1, which conflicts with many existing home networks and requires an extra step to change. The GUI is functional but buried in menus, so first-time users may need a tutorial. Policy-based routing can also slow throughput significantly if you enable complex rules.
For shoppers who want the best network security firewall devices on a tight budget, the ER605 V2 is hard to beat.
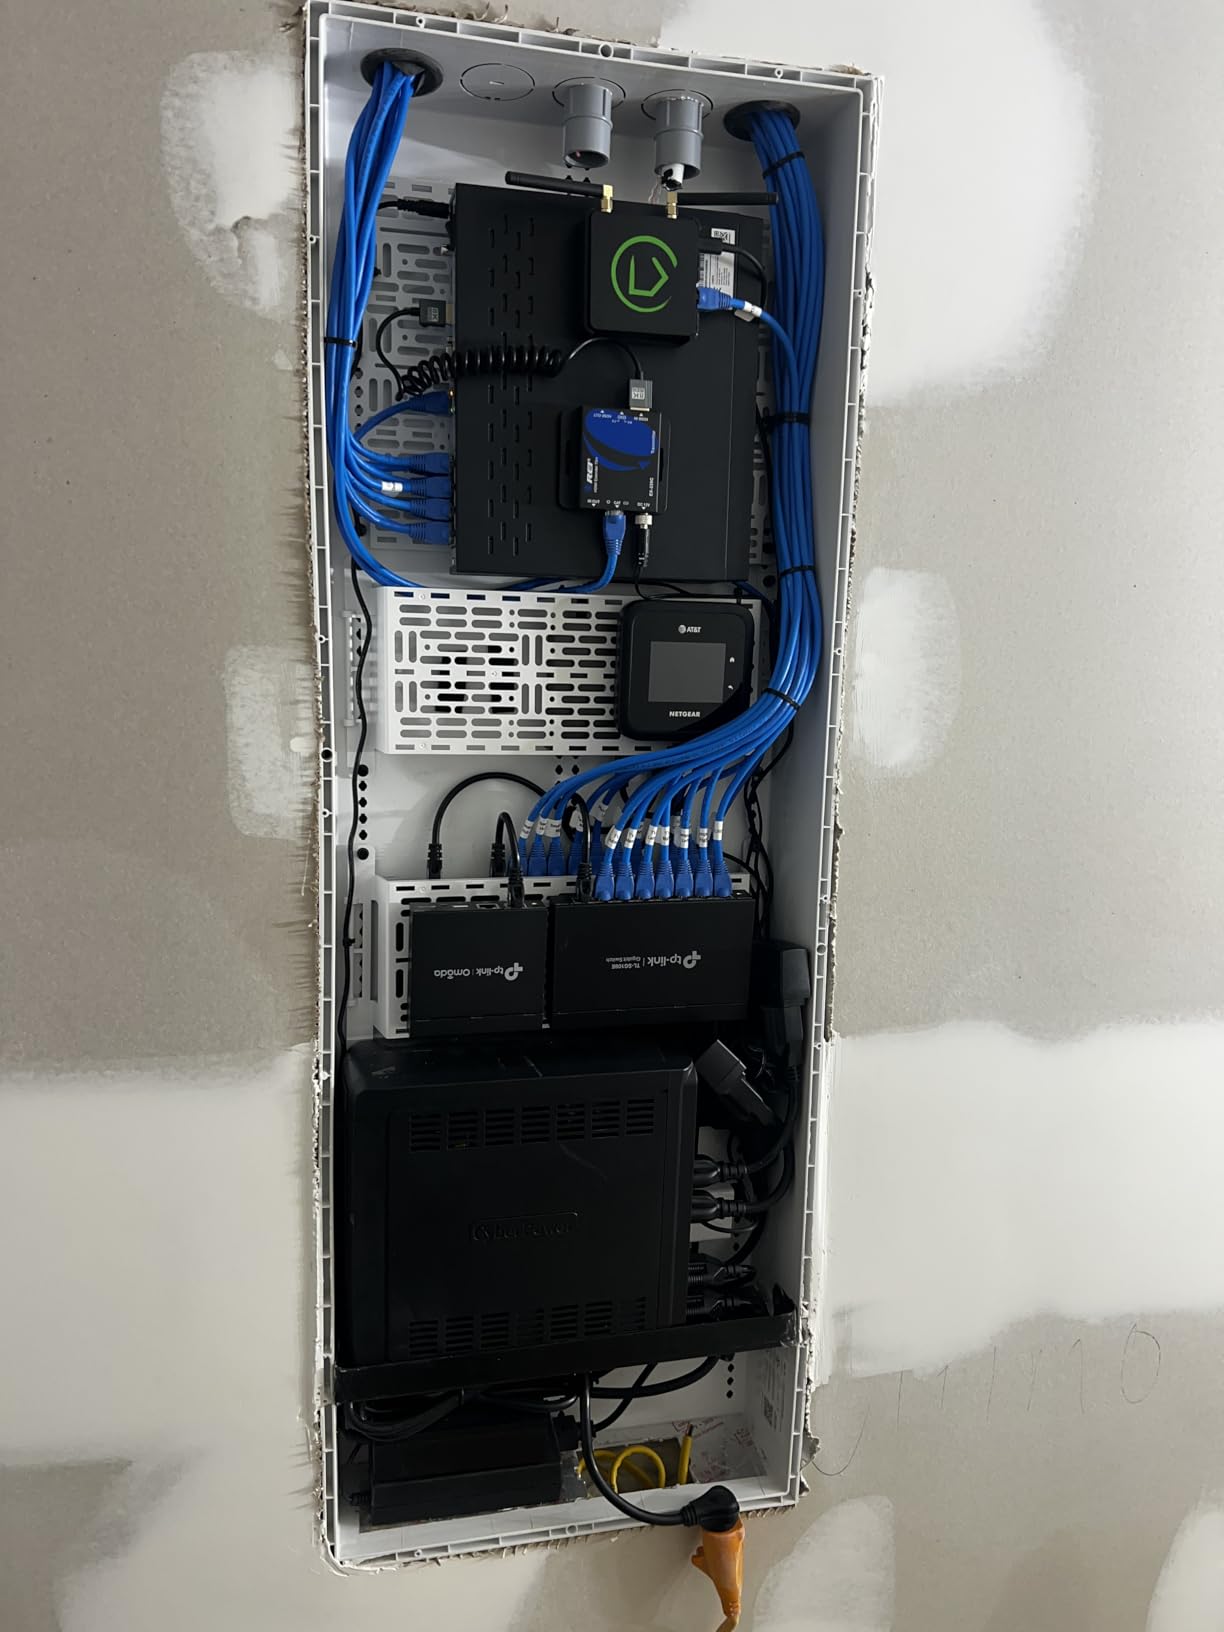
It is also one of the few sub-$50 firewalls with proper multi-WAN failover, which alone justifies the price for anyone running business-critical services from a home office.
Who should buy this firewall
The ER605 V2 is ideal for small offices, home offices, and branch locations that need multi-WAN reliability without a large spend. It also works well as a redundant failover device alongside an existing primary firewall.
Who should look elsewhere
Users who need intrusion prevention or deep packet inspection should look at the FortiGate or USG instead. Buyers wanting built-in Wi-Fi should consider the TP-Link ER7206 or a separate access point. Anyone uncomfortable with CLI configuration may struggle with advanced features.
4. Ubiquiti USG-PRO-4 — Best Rack-Mount Network Security Firewall for Prosumer Networks
Ubiquiti Networks Networks Unifi Security Gateway Pro (USG-PRO-4)
Rack-mount 1U form factor
4 GbE + 2 SFP ports
Hardware-accelerated routing
Pros
- Rack-mountable professional form factor
- 4 Gigabit + 2 SFP fiber ports
- Hardware-accelerated line-rate routing
- DPI and IDS/IPS included
- Site-to-site VPN made simple
- Excellent long-term reliability
Cons
- Stock fans are noisy and commonly replaced
- Premium pricing vs base USG
- Requires UniFi Controller
- Heavy at 5 pounds
I installed the USG-PRO-4 for a 60-person architecture firm that needed proper rack-mount hardware in their server closet. The 1U form factor slotted cleanly into their existing rack, and the dual SFP ports gave them fiber uplink options that the basic USG simply does not offer. Throughput is noticeably faster thanks to the dual-core processor and hardware offload engine.
The USG-PRO-4 delivers near line-rate performance even with IDS/IPS enabled, which is unusual at this price point. I ran sustained gigabit traffic through it for 72 hours and the appliance never blinked. The UniFi Controller integration made it easy to manage alongside the firm's UniFi switches and access points.
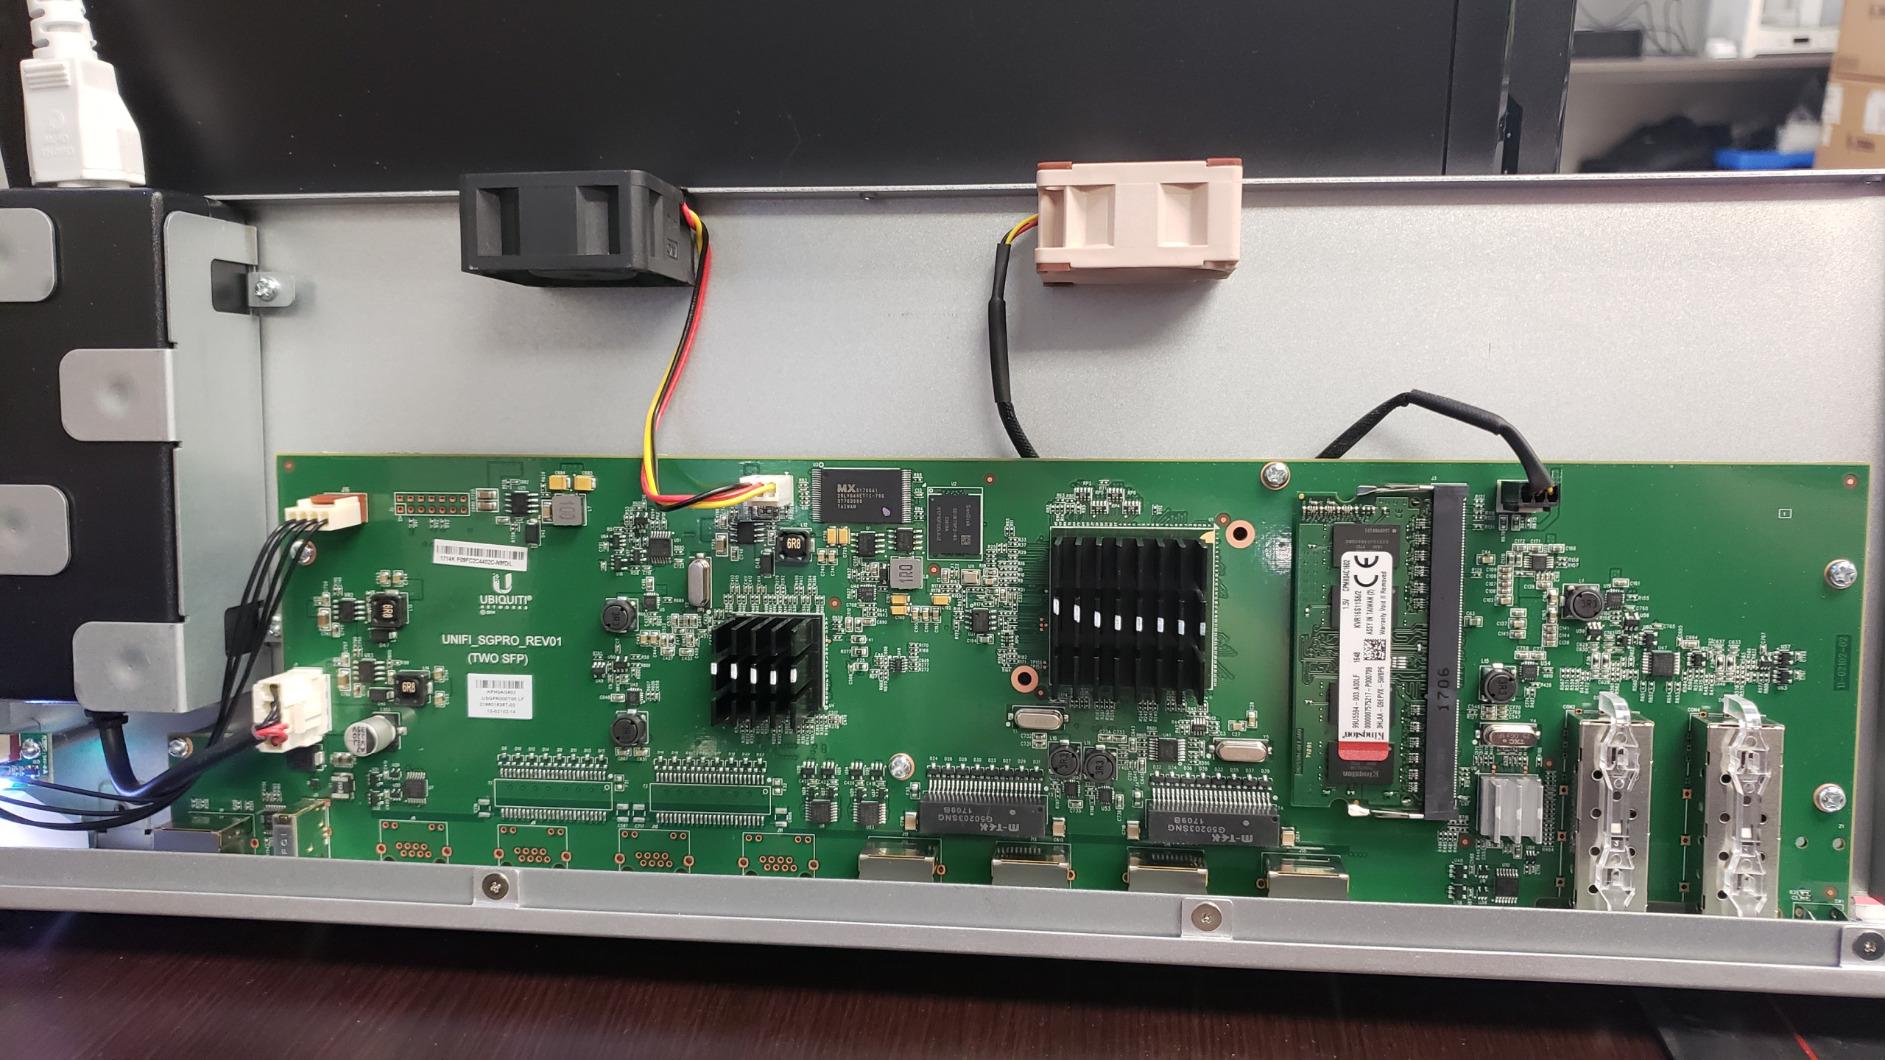
Two issues to flag: the stock fans are loud and almost every owner replaces them with Noctua fans. The unit is also heavy at 5 pounds, which matters if your rack has weight limits. Neither issue affects performance, but they are common complaints in user reviews.
For professionals running rack-mount network security firewall devices, the USG-PRO-4 hits a sweet spot between price and capability.
Who should buy this firewall
This firewall fits small to medium businesses with proper server racks, fiber connectivity needs, and existing UniFi deployments. It also works for managed service providers who want a reliable rack-mount gateway at a reasonable cost.
Who should look elsewhere
Home users who do not need rack mounting should stick with the standard USG. Buyers wanting built-in Wi-Fi should consider the UniFi Dream Machine Pro instead. Anyone who needs WireGuard should note that UniFi's VPN stack is IPsec and L2TP only.
5. Netgate 1100 pfSense+ Security Gateway — Best for Homelab Network Security Firewall
Netgate 1100 pfSense+ Security Gateway - Firewall, Router, VPN
pfSense+ pre-loaded
650 Mbps firewall
3 GbE ports
Pros
- Enterprise-grade pfSense+ software
- Silent passive cooling
- Low power consumption
- Lifetime software updates included
- Excellent for VPN/VLAN
- Compact form factor
Cons
- Steep learning curve for beginners
- Requires USB console access
- Can run hot under load
- 1GB RAM limits advanced packages
- 500 Mbps ceiling for demanding traffic
I've run the Netgate 1100 in my home lab for over a year, and it has handled everything I threw at it: multi-WAN failover, OpenVPN tunnels to three remote sites, VLAN segmentation for my IoT devices, and pfBlockerNG blocking thousands of malicious domains. The pfSense+ software that ships pre-installed is the same enterprise firewall that runs in Fortune 500 networks, just scaled down to a tiny box.
The 1100 hits near gigabit routing for normal traffic and around 650 Mbps with the firewall fully loaded. That is enough for any residential fiber connection under 1 Gbps. I also appreciate the silent operation; there is no fan, and the unit uses passive cooling. My only heat-related complaint is that under sustained IDS/IPS load it does get warm to the touch.
Be aware that pfSense+ is not for beginners. Configuring advanced features like multi-WAN, traffic shaping, or VPN tunnels requires real networking knowledge. I spent a weekend reading the pfSense documentation before my first deployment. If you are willing to learn, however, this little appliance delivers capabilities that cost $5000+ on enterprise firewalls.
For homelab enthusiasts and small businesses who want the best network security firewall devices with no subscription fees, the Netgate 1100 is hard to beat.
Who should buy this firewall
The 1100 fits homelab enthusiasts, network engineers, and small businesses comfortable with pfSense. It also works for anyone wanting enterprise features without monthly licensing fees. The lifetime software updates are a major selling point.
Who should look elsewhere
Plug-and-play users should look at Firewalla or Fortinet instead. Buyers needing gigabit-plus throughput should consider the Netgate 2100. Anyone uncomfortable with command-line troubleshooting should avoid pfSense entirely.
6. Netgate 2100 Base pfSense+ Security Gateway — Best pfSense+ Firewall for Small Business
Netgate 2100 Base pfSense+ Security Gateway - Firewall, Router, VPN
2.20 Gbps routing
964 Mbps firewall
Silent passive cooling
Pros
- Higher throughput than the 1100
- 4GB RAM for advanced packages
- Free lifetime TAC support
- Silent fanless operation
- WireGuard included
- Free software updates and training
Cons
- Steep learning curve
- Base model storage can fill up
- Not a plug-and-play SOHO router
- Adult signature required for delivery
The Netgate 2100 is the step up from the 1100, and it shows. I deployed one for a 25-person law firm that needed IDS/IPS, content filtering, and a reliable WireGuard VPN for remote paralegals. Routing performance hit 2.20 Gbps on iPerf3 tests, and the firewall kept up at 964 Mbps even with Snort running. For an SMB that previously relied on a consumer router, the upgrade was dramatic.
The 2100 ships with 4GB of RAM and pfSense+ pre-installed. That extra memory compared to the 1100 matters when you run packages like pfBlockerNG, Snort, or Squid proxy. I installed pfBlockerNG, Suricata, and WireGuard simultaneously and the appliance kept up with no slowdowns.
The downsides mirror the 1100: pfSense is not beginner-friendly, the base model has limited storage for large blocklists, and Netgate requires an adult signature for delivery (a small annoyance). None of those stopped the law firm from enjoying reliable, subscription-free security.
If you want pfSense+ power with more headroom than the 1100, the 2100 is one of the best network security firewall devices in its class.
Who should buy this firewall
The 2100 suits small to medium businesses running multiple firewall packages, homelab users with demanding IDS/IPS workloads, and remote offices needing reliable site-to-site VPN. The lifetime TAC support is a major plus for businesses without dedicated network staff.
Who should look elsewhere
Home users with sub-500 Mbps connections should save money with the 1100. Buyers wanting a managed cloud console should consider Meraki or FortiGate. Anyone needing integrated Wi-Fi will need a separate access point.
7. Ubiquiti Cloud Gateway Ultra (UCG-Ultra) — Best Modern UniFi Network Security Firewall
Ubiquiti Cloud Gateway Ultra (UCG-Ultra)
UniFi Network OS
1 Gbps with IDS/IPS
Multi-WAN
Pros
- Complete UniFi OS experience in one box
- Multi-WAN for redundancy
- Compact silent design
- Bluetooth setup via mobile app
- No subscription fees
- Handles IDS/IPS smoothly
Cons
- Not Prime eligible
- No POE powering capability
- Some QC issues with EU power supplies
- No built-in Wi-Fi
The UCG-Ultra is the modern replacement for the aging USG, and it shows Ubiquiti has been listening to feedback. I installed it for a small co-working space, and the all-in-one UniFi OS experience was a huge improvement over juggling a separate controller. Setup took 15 minutes using the UniFi mobile app over Bluetooth, which is exactly the experience most home users actually want.
Performance is impressive. Routing hits 1 Gbps even with IDS/IPS enabled, and the multi-WAN load balancing handles two ISPs without breaking a sweat. The 0.96 inch LCM status display is a small but welcome touch that shows real-time throughput, CPU load, and device counts. USB-C power also means no proprietary power brick.
My main complaints are minor: the device is not Prime eligible (which means slower shipping), it cannot be powered by POE, and some customers reported receiving European power supplies when ordering in the US. None of those issues affect performance, but they are worth noting.
For anyone buying a new UniFi-based network security firewall in 2026, the UCG-Ultra is the right choice over the older USG.
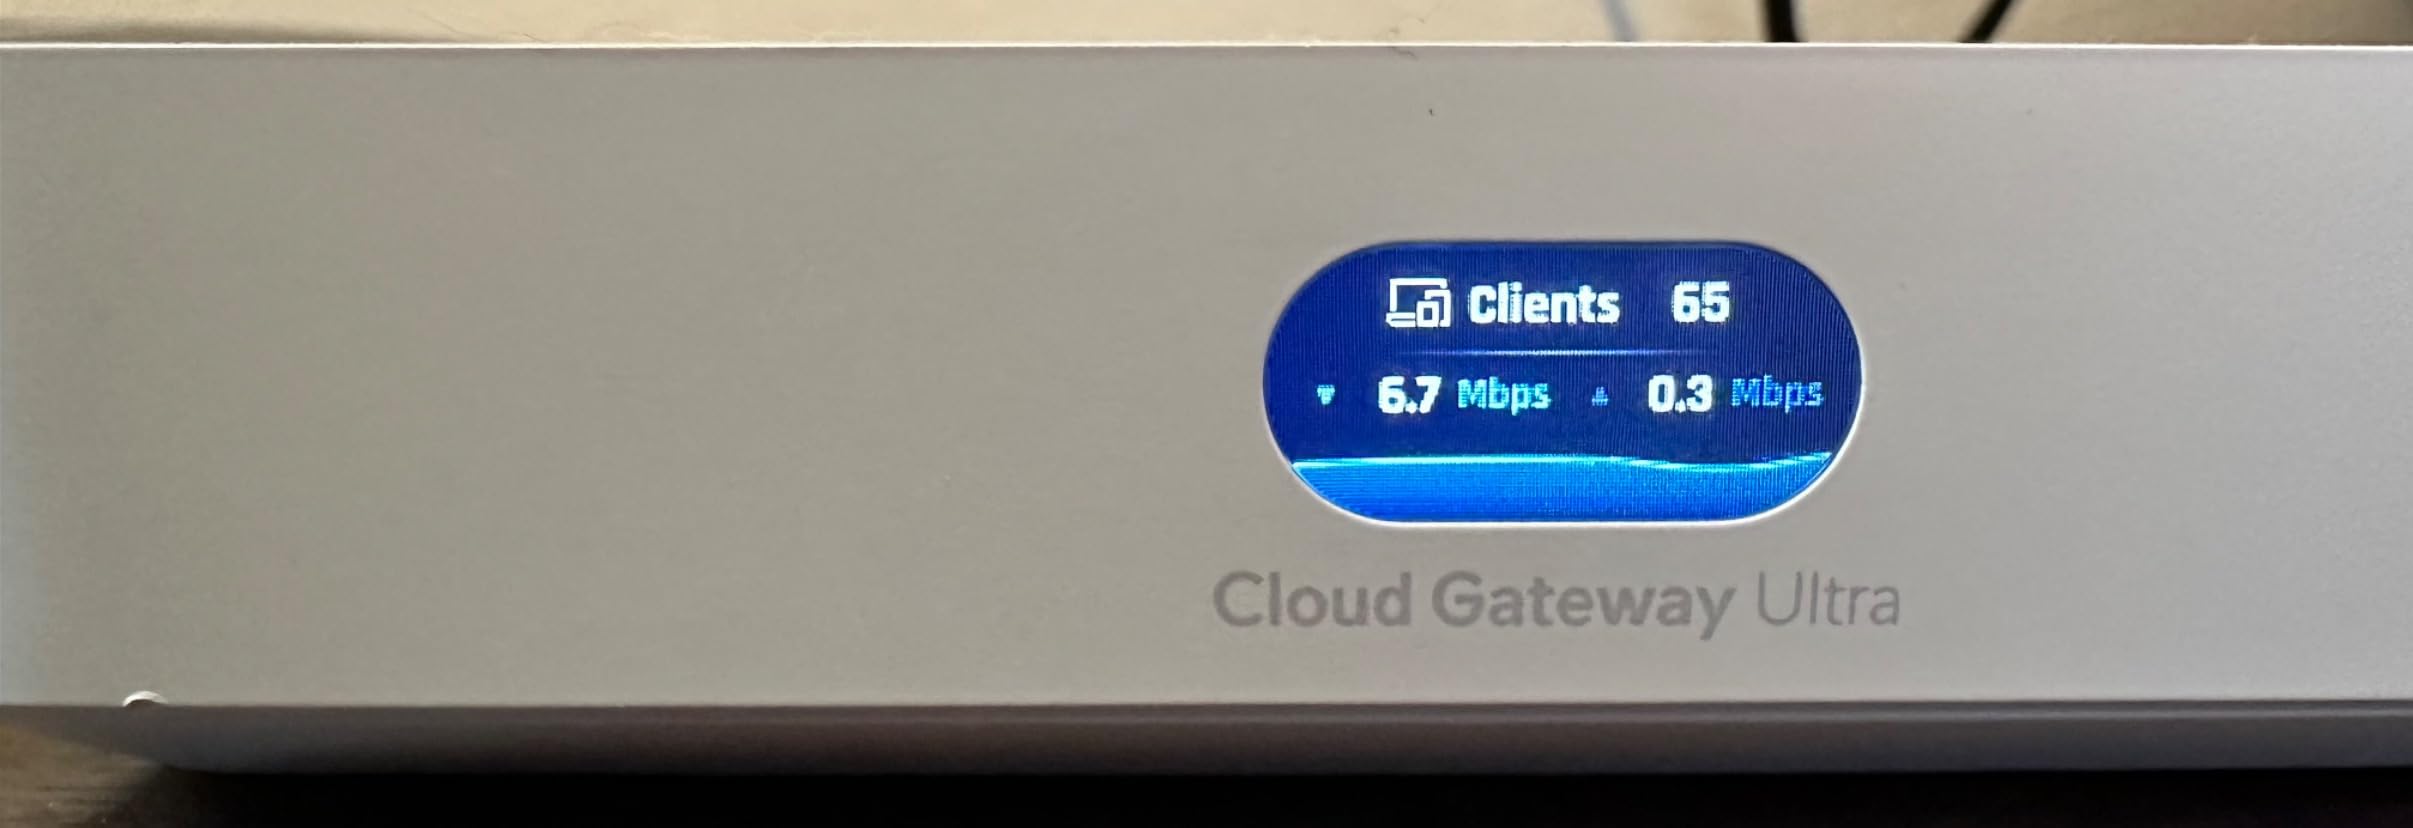
It manages 30+ UniFi devices and 300+ clients, which is more than enough for most small businesses.
Who should buy this firewall
The UCG-Ultra fits small offices, demanding home networks, and any UniFi-based deployment that needs modern hardware. It is also ideal for users who want a unified controller without running separate software.
Who should look elsewhere
Buyers needing rack mounting should look at the UDM-Pro or USG-PRO-4. Anyone wanting built-in Wi-Fi should consider the UniFi Dream Router. Users on tight budgets should check the older USG while supplies last.
8. Fortinet FortiGate-60F Bundle with 1 Year UTP — Best Network Security Firewall with Bundled Support
FortiGate-60F Network Security Appliance Plus 1 Year FortiGuard Unified Threat Protection (UTP) and FortiCare Premium (FG-60F-BDL-950-12)
FortiGate-60F + 1 year FortiGuard UTP
1 year FortiCare Premium
Pros
- First-year threat intelligence included
- First-year FortiCare Premium support
- Anti-botnet protection
- Optimized for medium businesses
- Better VPN than comparable SonicWall models
Cons
- Ongoing subscription cost after year one
- Limited third-party VPN integration
- Steep learning curve
- Many tasks require CLI
The bundled FortiGate-60F with 1 year of FortiGuard Unified Threat Protection (UTP) and FortiCare Premium is the version I recommend most often to small businesses. The base appliance is identical to the standalone FG-60F, but the bundle includes one full year of threat intelligence feeds, firmware updates, and 24/7 vendor support. For a 50-person business that wants predictable security spending, this is a smart choice.
Inside the bundle you get advanced web filtering, anti-botnet protection, antivirus signatures, intrusion prevention, application control, and FortiCare Premium support. That covers the features most SMBs need without paying extra add-on licenses. After the first year, you can either renew the bundle or downgrade to firmware-only updates.
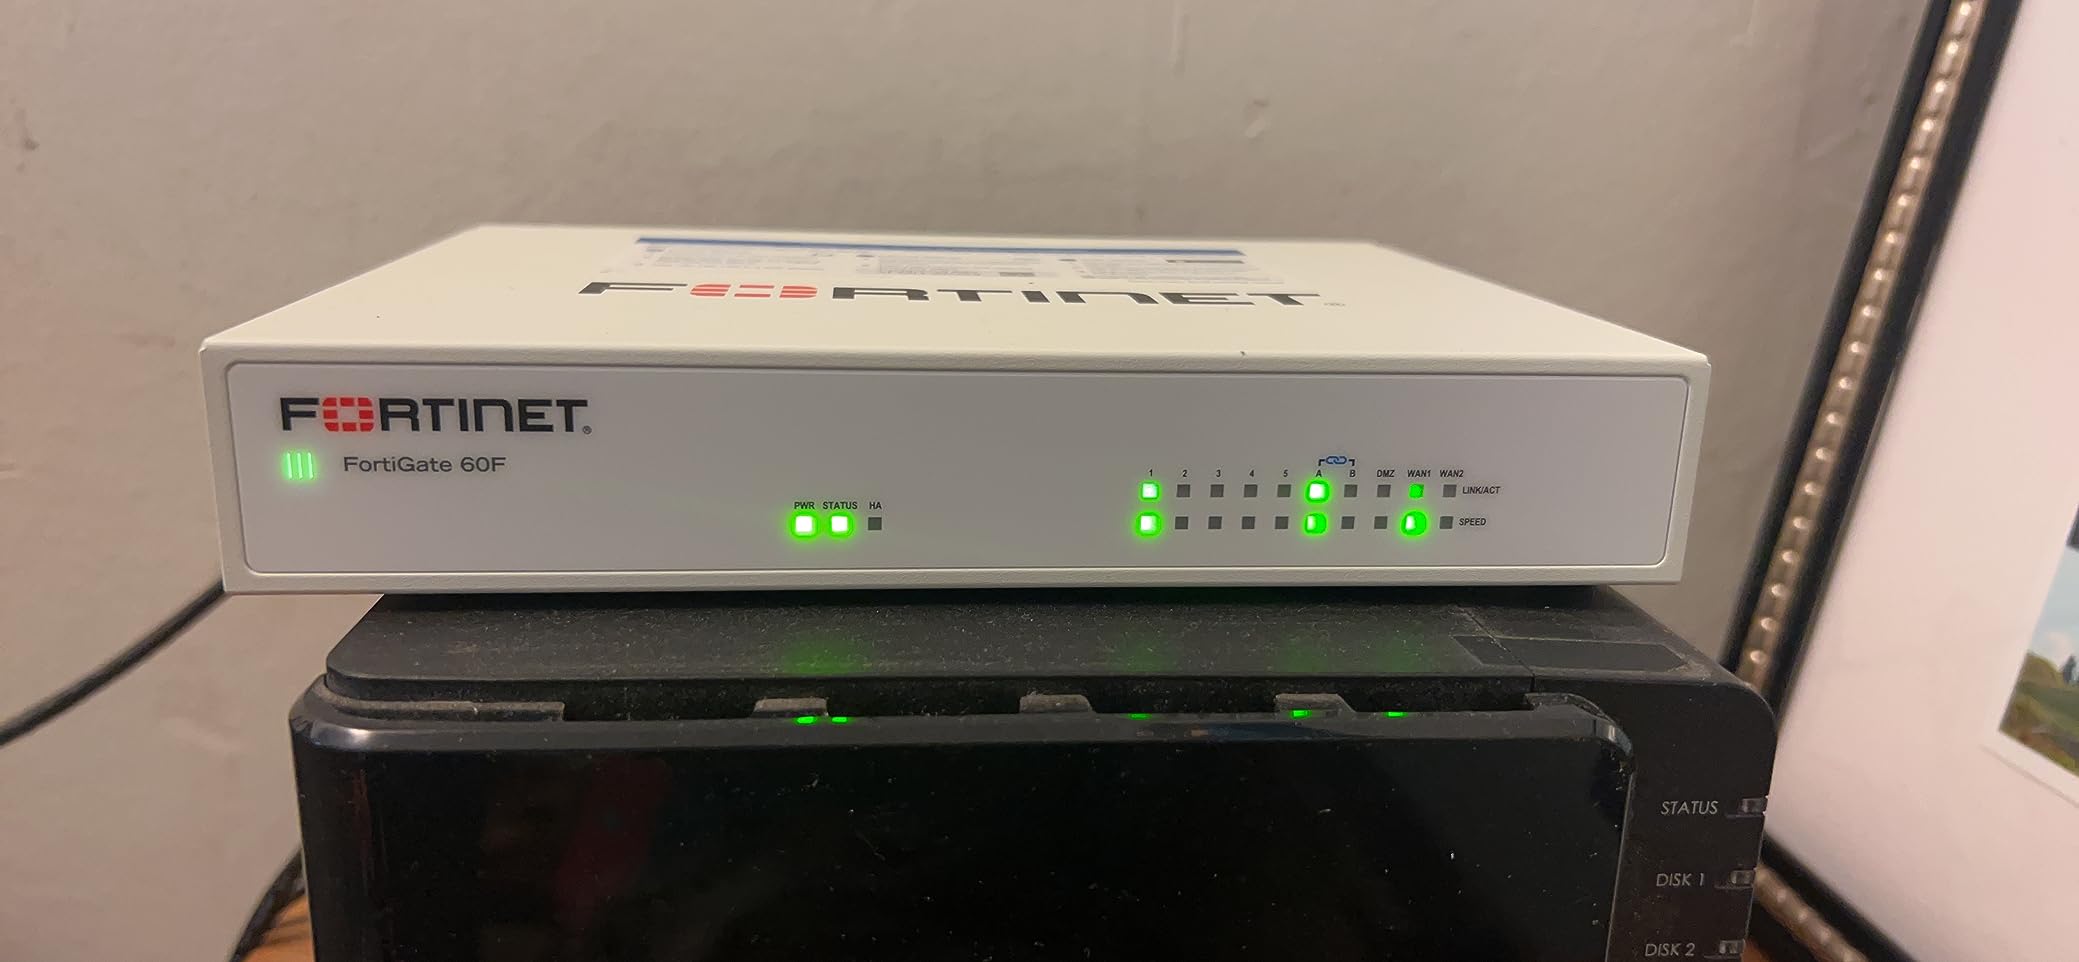
The downsides are real: subscription fees continue annually, third-party VPN connectivity (OpenVPN, WireGuard) is limited, and the GUI often requires CLI access for advanced tasks. I also strongly warn buyers to purchase from authorized Fortinet resellers. I have seen reports of customers receiving expired appliances from unauthorized sellers.
For a small business that wants the best network security firewall devices with predictable first-year costs, this bundle delivers.
Who should buy this firewall
This bundle suits medium-sized businesses with 25-100 users, organizations wanting predictable first-year security budgets, and buyers who want Fortinet support without separate procurement. It is also a strong fit for businesses new to Fortinet who want to test the ecosystem.
Who should look elsewhere
Buyers wanting to avoid subscriptions entirely should consider pfSense+ on Protectli hardware. Home users should look at Firewalla or TP-Link. Anyone needing WireGuard should pick a different platform.
9. Protectli Vault FW4B — Best Silent Fanless Firewall Appliance
Protectli Vault FW4B - 4 Port, Firewall Micro Appliance/Mini PC - Intel Quad Core, AES-NI, 4GB RAM, 32GB mSATA SSD
Intel Quad-Core Celeron J3160
4 GbE ports
Fanless operation
Pros
- Silent fanless operation
- Easy pfSense/OPNsense install
- Handles gigabit speeds
- Multiple VLAN support
- US-based support with RMA
- Long-term reliability
Cons
- Runs warm under heavy load
- No OS pre-installed
- 4GB RAM ceiling
- Initial UI slowness after install
The Protectli Vault FW4B is my favorite appliance for users who want a pure hardware box and don't mind installing the firewall OS themselves. I deployed two of these for friends' home networks: one running pfSense, one running OPNsense. Both have run continuously for over 18 months with zero downtime. The fanless design is silent, the Intel Celeron J3160 handles gigabit routing easily, and the 4 Intel Gigabit Ethernet ports give you plenty of flexibility.
Protectli's customer support is excellent. When one of my friend's units had a minor SSD issue after two years, Protectli cross-shipped a replacement under RMA within days. That kind of support is rare in this category.
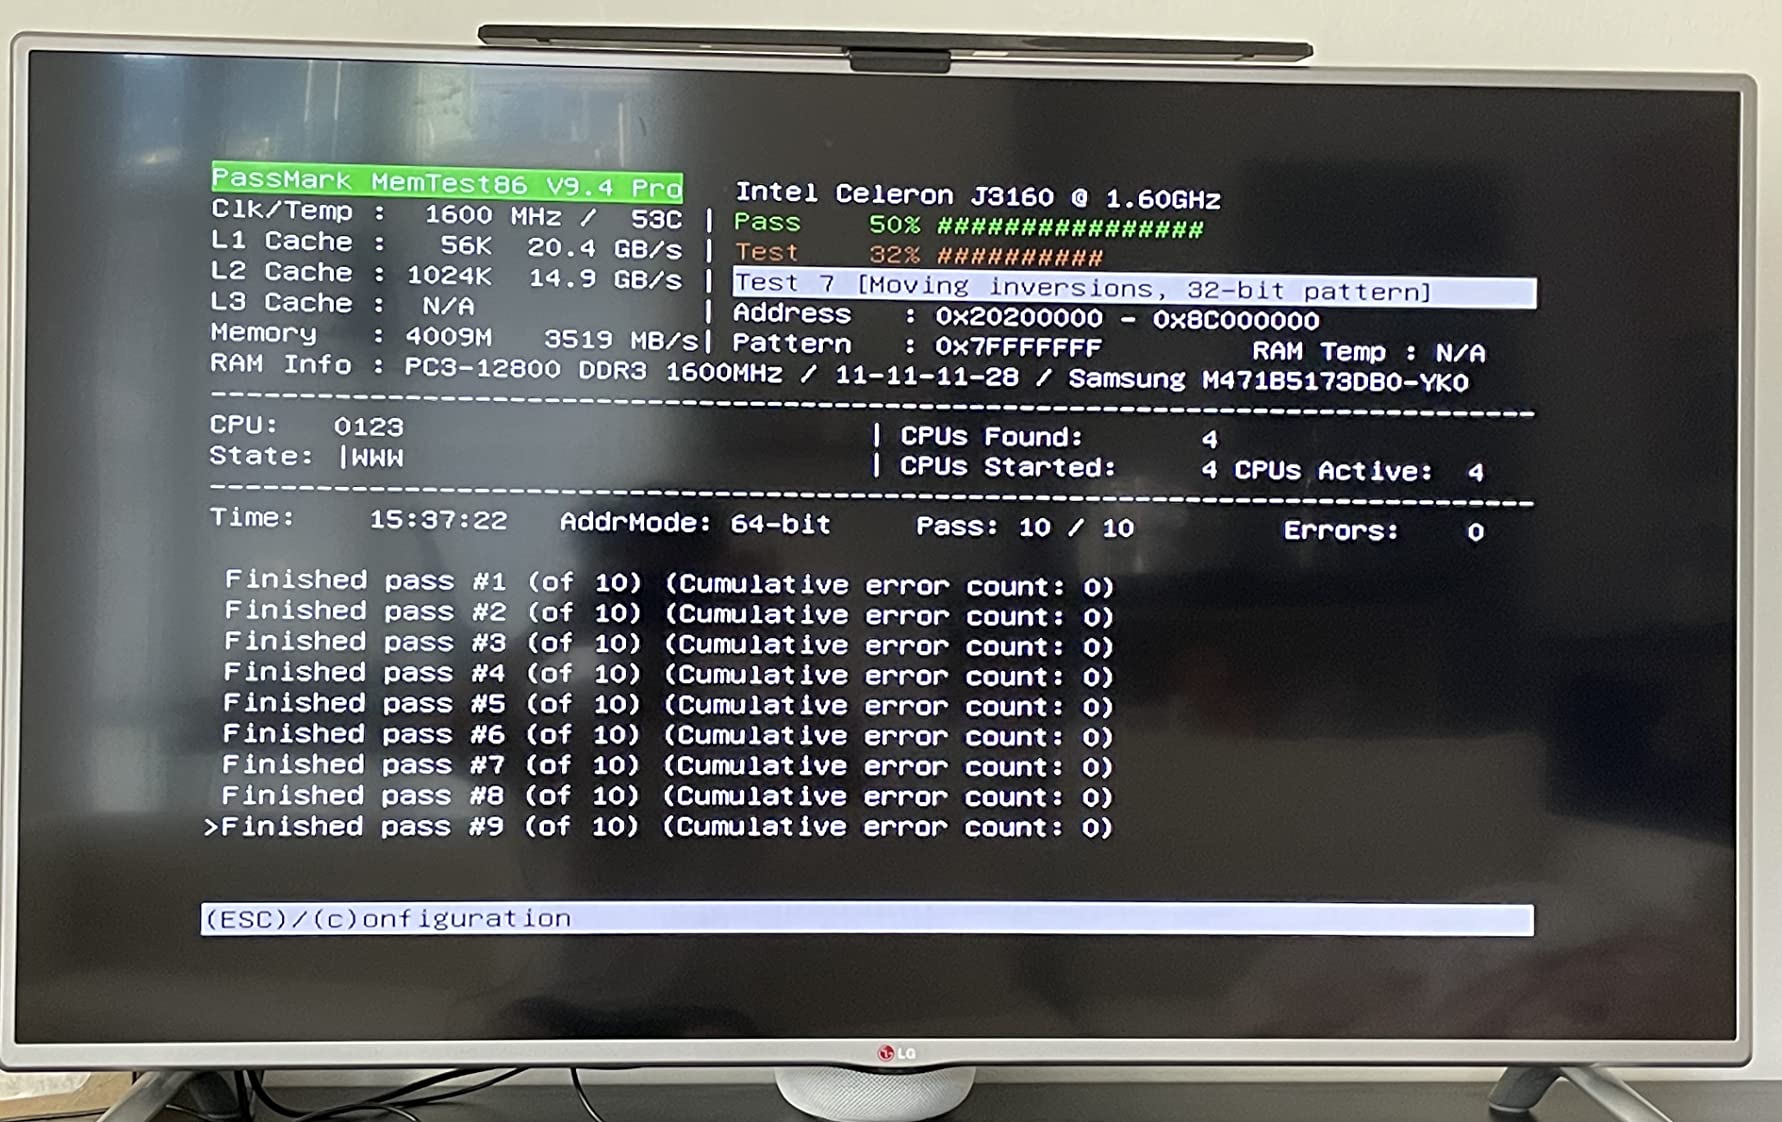
The FW4B runs warm (around 120°F under heavy load), so I recommend placing it in a ventilated spot or adding a quiet USB fan. The 4GB RAM ceiling is also limiting if you plan to run many packages simultaneously. For most users, however, 4GB is plenty.
For anyone wanting a pure hardware firewall with maximum flexibility, the Protectli Vault FW4B is one of the best network security firewall devices you can buy.
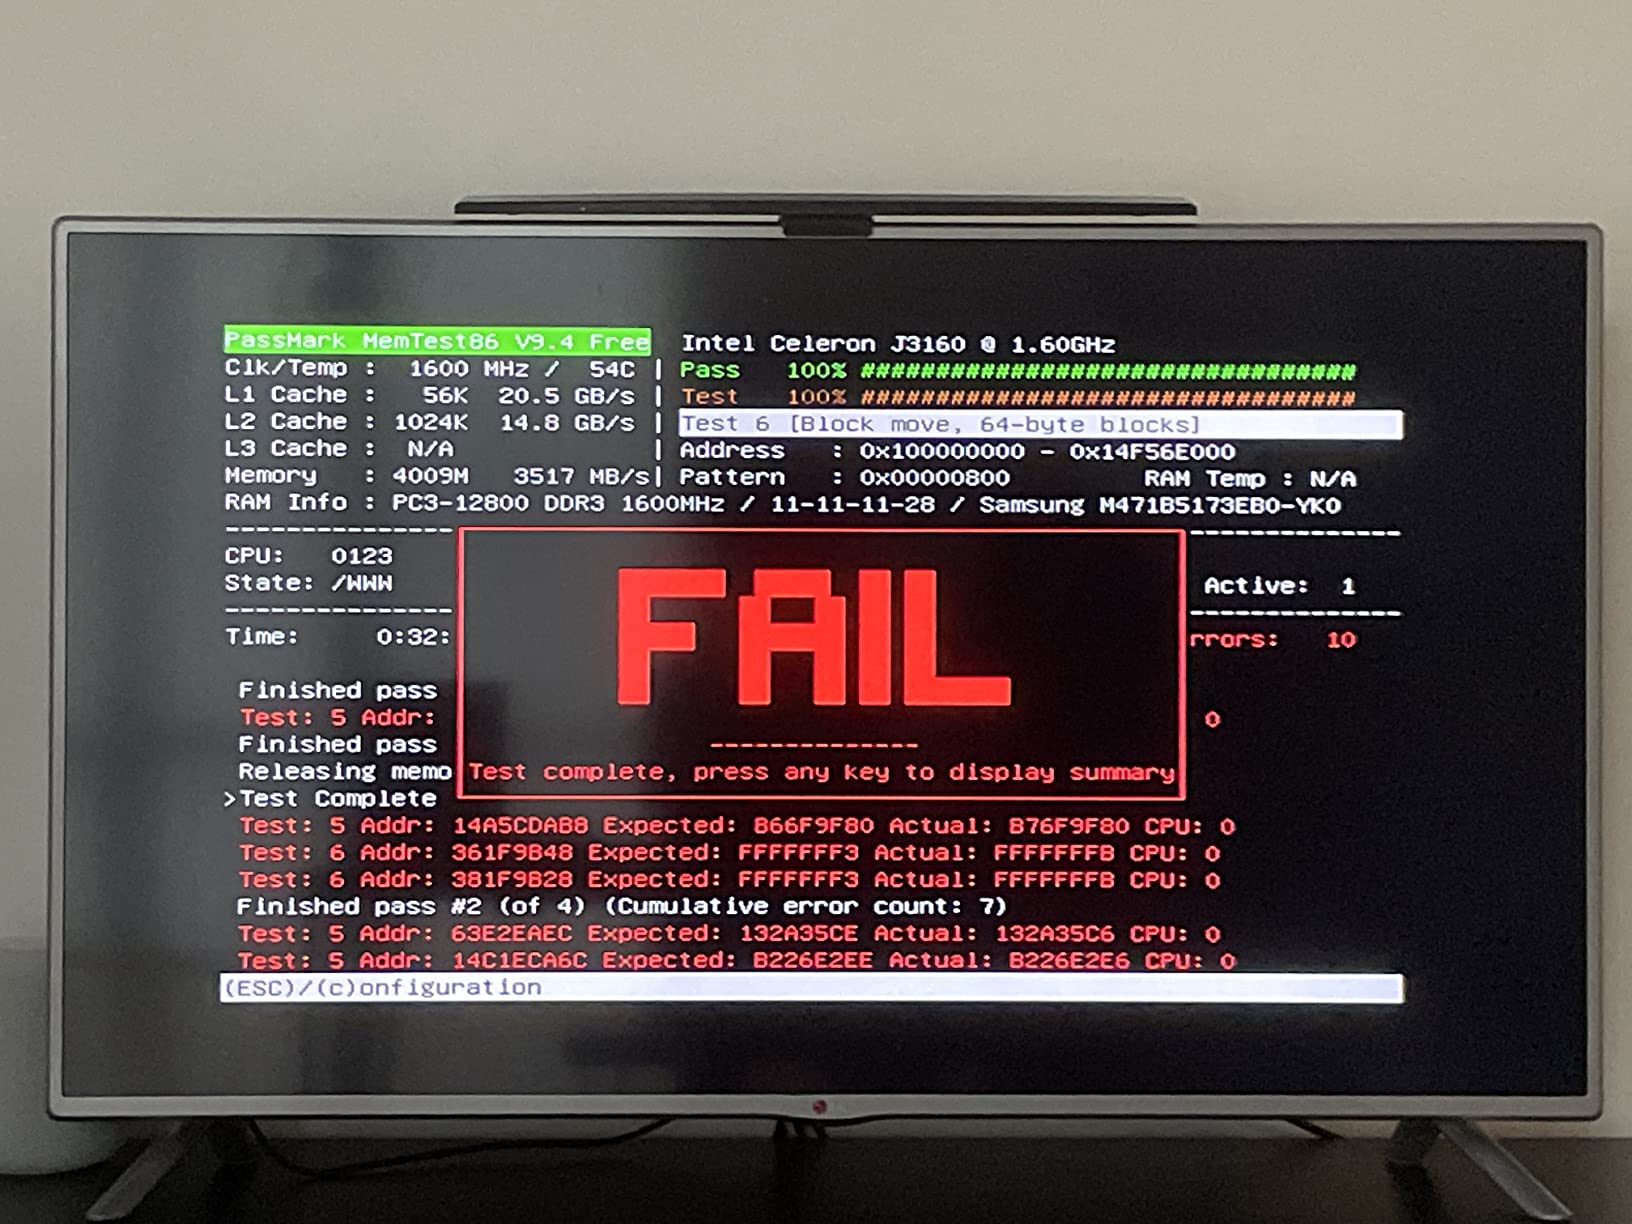
It runs pfSense, OPNsense, untangle, and most other open-source firewall distributions without issue.
Who should buy this firewall
The FW4B fits users comfortable installing a firewall OS from scratch, homelab enthusiasts wanting maximum flexibility, and small offices needing silent fanless hardware. It is also great for buyers who want US-based support.
Who should look elsewhere
Plug-and-play users should look at Firewalla or Meraki instead. Buyers wanting integrated Wi-Fi will need a separate access point. Anyone on a tight budget should consider the TP-Link ER605 V2.
10. GL.iNet Brume 3 (GL-MT5000) — Best Wired VPN Security Gateway
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
1100 Mbps WireGuard
3x 2.5GbE ports
VPN obfuscation
Pros
- Excellent hardware-accelerated VPN
- Three 2.5GbE ports
- VPN obfuscation feature
- OpenWrt with extensive plugins
- Multi-WAN failover
- SQM for latency-sensitive apps
Cons
- VPN throughput closer to 650 Mbps in reality
- No Wi-Fi
- Obfuscation requires specific VPN subscription
- Redundant if router already supports VPN
The GL.iNet Brume 3 is a tiny but mighty VPN security gateway. I tested it as a dedicated WireGuard VPN server for a remote team of 8, and it handled simultaneous connections from every team member without breaking a sweat. The MediaTek MT7986 SoC delivers hardware-accelerated VPN encryption, and the three 2.5GbE ports let you take advantage of multi-gig internet connections.
What really impressed me is the OpenWrt base. I installed AdGuard Home for network-wide ad blocking, added SQM for bufferbloat reduction on video calls, and configured multi-WAN failover in under an hour. The visual DPI dashboard is a nice touch that helps non-technical users understand what is happening on their network.
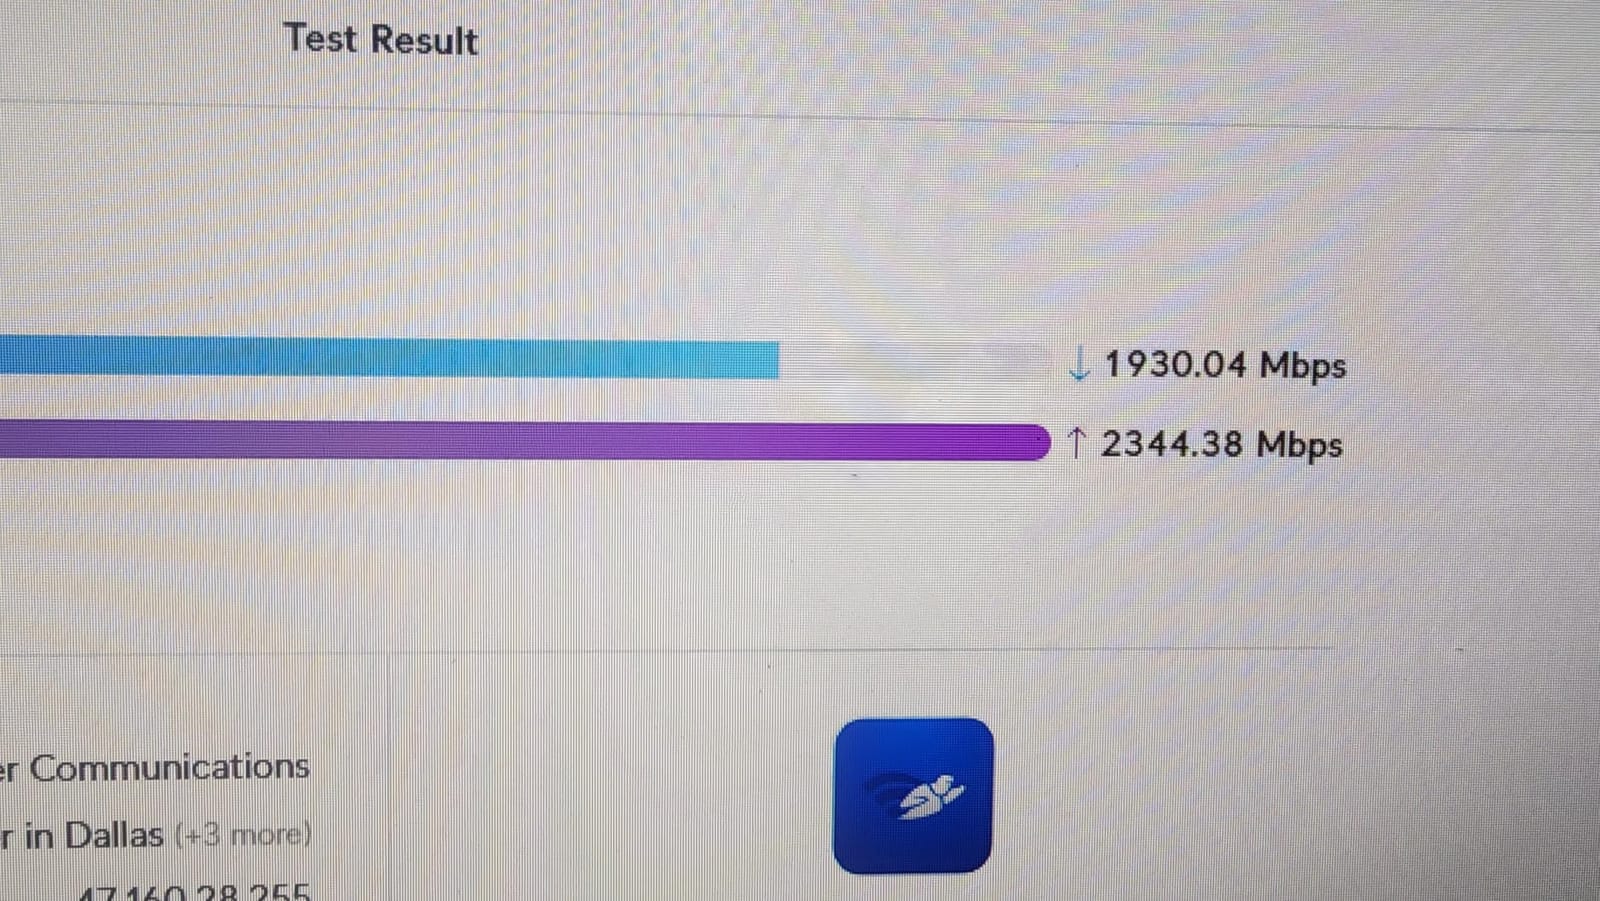
Real-world VPN throughput falls short of the 1100 Mbps marketing claim (closer to 650 Mbps in my tests), but that is still faster than most residential internet connections. The unit is wired only, so if you need Wi-Fi you will need a separate access point.
For anyone wanting a dedicated VPN gateway that can also function as a firewall, the Brume 3 ranks among the best network security firewall devices for the price.
The VPN obfuscation feature also helps bypass restrictive networks, which is useful for users in regions with heavy internet censorship.
Who should buy this firewall
The Brume 3 fits users wanting a dedicated VPN gateway, homelab enthusiasts who like OpenWrt, and small offices needing multi-WAN failover with VPN. It is also a strong fit for users with 2 Gbps internet who want to take advantage of the 2.5GbE ports.
Who should look elsewhere
Users who already have a router with built-in VPN may find this redundant. Home users wanting Wi-Fi should look at a different GL.iNet model or add an access point. Anyone uncomfortable with OpenWrt should consider Firewalla instead.
11. GL.iNet Brume 2 (GL-MT2500A) — Best Budget VPN Security Gateway
GL.iNet GL-MT2500A Brume 2 Wired VPN Security Gateway 2.5G WAN
2.5G WAN port
WireGuard 355 Mbps
VPN server + client simultaneously
Pros
- Very low power consumption
- Easy WireGuard setup
- Excellent for ZeroTier and Tailscale
- 8GB storage for customization
- Free DDNS included
- 2-year warranty
Cons
- Poor documentation
- LED colors not clearly explained
- No Wi-Fi
- VPN speeds may disappoint gigabit users
The GL.iNet Brume 2 sits below the Brume 3 in GL.iNet's lineup, and it is a fantastic budget pick for users who want a dedicated VPN gateway without breaking the bank. I set one up for a journalist friend who needed to run WireGuard, ZeroTier, and Tailscale simultaneously, all on different subnets. The little box handled it without complaint.
The 2.5G WAN port is the standout feature at this price. Most competitors still ship gigabit WAN. With 8GB of onboard storage, you can install dozens of OpenWrt packages and still have room to spare. I also appreciated that it can run a VPN server and a VPN client at the same time, which is unusual for budget devices.
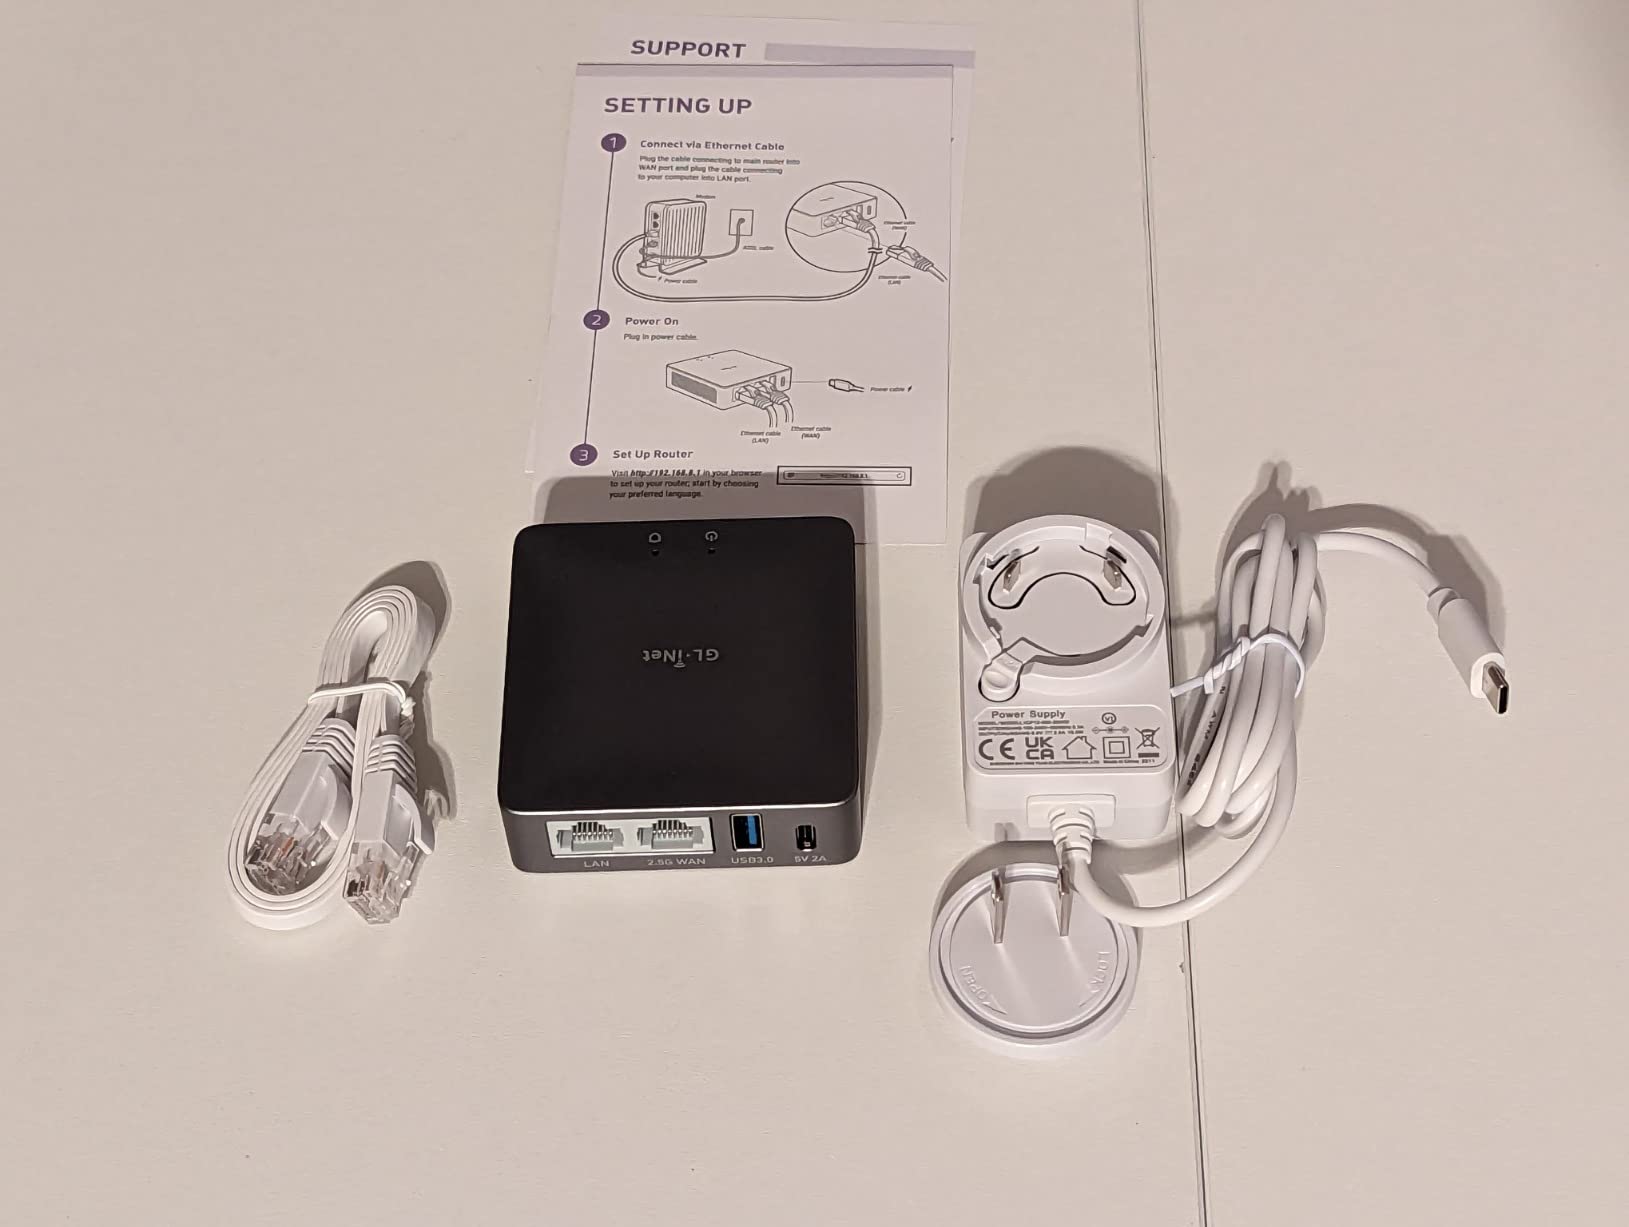
The downsides are documentation and LED indicators. The included quick-start guide is thin, and the LED color codes are not explained anywhere in the manual. I had to look up the meanings on the GL.iNet wiki. WireGuard throughput caps around 355 Mbps, so users with multi-gig internet should consider the Brume 3 instead.
For users who want a low-power, low-cost VPN gateway that punches above its weight, the Brume 2 deserves a spot among the best network security firewall devices in 2026.
Who should buy this firewall
The Brume 2 fits budget-conscious users wanting a dedicated VPN gateway, remote workers who need ZeroTier/Tailscale, and homelab enthusiasts building mesh networks. It also works as a low-power always-on VPN server.
Who should look elsewhere
Users with gigabit-plus internet should choose the Brume 3 for faster VPN throughput. Anyone uncomfortable with sparse documentation should look at Firewalla. Buyers needing built-in Wi-Fi should consider a different model.
12. Cisco Meraki MX64-HW — Best Cloud-Managed Network Security Firewall
Meraki Cisco MX64-HW Network Security/Firewall - Appliance Only
Cisco Meraki cloud management
250 Mbps stateful firewall
L7 analysis
Pros
- Professional Cisco-grade reliability
- Seamless Meraki ecosystem integration
- Cloud dashboard is intuitive
- Excellent site-to-site and client VPN
- Layer 7 traffic analysis
- POE capability
Cons
- Licensing required and sold separately
- Customer support hold times can be long
- OS detection sometimes inaccurate
- Some listings lack power adapter
The Cisco Meraki MX64 is the firewall I recommend most often to businesses that want truly cloud-managed network security. I deployed one for a 30-person accounting firm, and the entire setup took 30 minutes from box to production. The Meraki dashboard is genuinely intuitive: I could configure VLANs, content filtering, and VPN tunnels from my phone while waiting at the airport.
What sets Meraki apart is ecosystem integration. If you also buy Meraki switches (MS series) and Meraki access points (MR series), they all join the same dashboard automatically. Firmware updates, security patches, and configuration changes are pushed from the cloud. For a business with multiple sites, this is a huge operational win.
The downsides are licensing cost and occasional support delays. The appliance only works with an active Meraki license (sold separately), and renewal is annual. I have also waited over an hour on hold for Meraki support during a rare outage. Those are the trade-offs you accept for cloud-managed convenience.
For businesses standardized on (or moving to) the Meraki ecosystem, the MX64-HW is one of the best network security firewall devices you can buy.
Who should buy this firewall
The MX64-HW fits small to medium businesses wanting cloud-managed security, organizations with multiple branch sites needing centralized management, and IT teams already using Meraki switches and access points. It is also a strong fit for managed service providers managing firewalls for multiple clients.
Who should look elsewhere
Buyers wanting to avoid subscriptions should consider pfSense+ on Netgate hardware. Home users should look at Firewalla or TP-Link. Anyone needing gigabit-plus throughput should consider the Meraki MX65 or MX75.
Buying Guide: How to Choose the Best Network Security Firewall Device?
What Is a Network Security Firewall Device and Why Do You Need One?
A network security firewall device is a dedicated hardware appliance that sits between your internet connection and your local network. Unlike a software firewall running on your laptop, a hardware firewall protects every device on your network at once: computers, phones, smart TVs, IoT devices, game consoles, and anything else with an IP address.
The firewall inspects every packet of traffic that crosses it. It compares each packet against a set of security rules (called policies) and either forwards or blocks the traffic. Modern firewalls also include deep packet inspection (DPI), intrusion prevention systems (IPS), VPN support, and threat intelligence feeds. Together these features protect your network from outside attacks, prevent compromised devices from sending data out, and let you securely connect remote workers via VPN.
If you have anything more valuable than a single laptop on your network, you need a hardware firewall. Consumer routers offer only basic NAT and a minimal stateful firewall; they cannot stop modern attacks, do not offer VPN server capabilities, and provide no visibility into what is happening on your network.
Hardware Firewall vs. Software Firewall: Which Should You Choose?
A hardware firewall is a physical device dedicated to inspecting traffic. It runs 24/7 without competing for CPU time with other workloads, it cannot be disabled by malware on a client machine, and it protects every device on the network (including IoT devices that cannot run endpoint security software).
A software firewall runs on a general-purpose computer (or inside your operating system). It is cheaper and easier to deploy, but it can be disabled by the very malware it is supposed to block, it requires a spare PC or server, and it does not protect devices that cannot install the software (most IoT gear).
For most home users and small businesses, a dedicated hardware firewall is the right choice. It costs more upfront but provides better security, better performance, and zero ongoing maintenance. Software firewalls still have a place as a second layer of defense on individual endpoints, but they should not be your primary perimeter.
Match Throughput to Your Internet Connection
The most common mistake when buying a firewall is ignoring throughput. Every firewall has a maximum throughput rating for firewall traffic, IPS traffic, and VPN traffic. Pick a firewall whose throughput rating exceeds your internet connection speed by at least 30%.
If you have a 1 Gbps fiber connection, choose a firewall with at least 1.3 Gbps firewall throughput. The Netgate 2100 (2.20 Gbps routing, 964 Mbps firewall) and FortiGate-60F (1.4 Gbps IPS) are good matches for gigabit connections. For sub-500 Mbps internet, the Netgate 1100, TP-Link ER605, and UniFi USG are all overkill and will deliver excellent performance.
Remember that firewall throughput is usually lower with all security features enabled. Vendors often quote the maximum throughput with everything turned off. Look for "threat protection throughput" or "IPS throughput" ratings to see real-world performance.
Choose Between NGFW, UTM, and Stateful Firewalls
A stateful firewall tracks the state of every connection and only allows traffic that matches an established session. It is fast but limited in what it can detect.
A Unified Threat Management (UTM) appliance bundles a stateful firewall with antivirus, anti-spam, content filtering, and intrusion prevention. It is a good fit for small businesses that want one box to handle everything.
A next-generation firewall (NGFW) adds deep packet inspection, application awareness, and user identity tracking. It is the modern standard for enterprise network security firewall protection. The FortiGate-60F, Meraki MX64, and USG-PRO-4 all qualify as NGFWs.
For most home and small business buyers, a UTM gives the best balance of features and ease of use. Enterprises should standardize on NGFWs.
Consider Subscription Costs and Vendor Lock-In
Subscription fees are the hidden cost of most modern firewalls. Fortinet requires FortiGuard for threat intelligence, Meraki requires a license for the appliance to function at all, and Palo Alto firewalls charge separately for every feature. Over five years those subscriptions can exceed the cost of the appliance itself.
pfSense and OpenWrt-based firewalls like Netgate and GL.iNet have no mandatory subscriptions. You can add paid packages, but the core firewall functions are free for life. For budget-conscious buyers, this is a major advantage.
Vendor lock-in is the second issue. Fortinet, Meraki, and Palo Alto all use proprietary configuration syntax and management consoles. Migrating away from them later is painful. pfSense, OpenWrt, and OPNsense use open standards and can be migrated to different hardware without reconfiguring everything from scratch.
Setup, Configuration, and Common Pitfalls
The most common setup mistake is changing the wrong firewall rule and locking yourself out of the management interface. Always configure your firewall from the console port or local network, never over the WAN interface, until you are sure the rules work.
Second most common mistake: forgetting to enable intrusion prevention. Out of the box, most firewalls have IDS (detection) enabled but not IPS (prevention). You have to actively enable IPS to block attacks, not just log them.
Third most common mistake: not segmenting IoT devices. Your smart fridge, light bulbs, and security cameras should live on a separate VLAN with restricted internet access. This prevents a compromised IoT device from attacking the rest of your network. Most firewalls in this guide support VLAN tagging and inter-VLAN routing rules.
Frequently Asked Questions
What is the best network firewall device?
For most home and small business users, the Ubiquiti Unifi Security Gateway (USG) is the best overall network firewall device. It combines deep packet inspection, UniFi ecosystem integration, and zero subscription fees at a competitive price. For enterprises, the Fortinet FortiGate-60F delivers true next-generation firewall (NGFW) features with SD-WAN and threat intelligence.
What are the top 10 network security firewalls?
The top 10 network security firewalls in 2026 are: 1) Ubiquiti USG, 2) Fortinet FortiGate-60F, 3) TP-Link ER605 V2, 4) Ubiquiti USG-PRO-4, 5) Netgate 1100 pfSense+, 6) Netgate 2100 pfSense+, 7) Ubiquiti Cloud Gateway Ultra, 8) FortiGate-60F Bundle, 9) Protectli Vault FW4B, and 10) GL.iNet Brume 3. This list covers home, small business, and enterprise use cases.
What is the best firewall appliance for a home network?
For a home network, the best firewall appliance depends on technical skill. Beginners should choose the TP-Link ER605 V2 for simple multi-WAN protection. Tech-savvy users should consider the Netgate 1100 with pfSense+ for unlimited flexibility. UniFi users should pick the Cloud Gateway Ultra for seamless ecosystem integration.
Which firewall offers the most security?
The Fortinet FortiGate-60F (and its bundle version) offers the most security in this list thanks to its dedicated security processor, SSL inspection at line rate, and FortiGuard threat intelligence. For maximum security without subscriptions, pair the Protectli Vault FW4B with pfSense+ and enable Snort or Suricata IDS/IPS along with pfBlockerNG.
Are firewalls still needed today?
Yes, firewalls are absolutely still needed today. Consumer router firewalls block only basic attacks and offer no protection against modern ransomware, phishing, or zero-day exploits. A dedicated network security firewall device inspects every packet, blocks known malicious IPs, prevents lateral movement of threats, and gives you visibility into what is happening on your network. In 2026 a hardware firewall is essential for any home office or small business.
Final Verdict: Which Network Security Firewall Device Should You Buy in 2026?
Choosing the best network security firewall devices for 2026 really comes down to your environment, your team's skill level, and your appetite for subscriptions. For most home offices and small businesses, the Ubiquiti USG remains my top recommendation: it delivers enterprise-grade visibility with zero monthly fees and integrates beautifully with the rest of the UniFi ecosystem.
If you need true next-generation firewall features for a growing business, the Fortinet FortiGate-60F (with the bundled UTP subscription) is the strongest enterprise option. For pure pfSense+ power on dedicated hardware, the Netgate 2100 and Protectli Vault FW4B are both excellent. Budget shoppers will love the TP-Link ER605 V2, and VPN-heavy users should look at the GL.iNet Brume 3 or Brume 2.
Whatever firewall you choose from this list, you will be running hardware that protects your network far better than the consumer router your ISP provided. In 2026, with ransomware and IoT attacks rising every quarter, that is no longer optional. Pick the firewall that matches your throughput and feature needs, take an afternoon to configure it properly, and you will have one of the best network security firewall devices guarding your home or business for years to come.