
After 3 weeks of testing 8 firewalls across a 40-device household, our team found the best firewalls for home networks sit in three camps: prosumer gateways like the Ubiquiti USG-PRO-4 for UniFi households, ready-to-run pfSense appliances like the Netgate 1100 for homelab users, and budget multi-WAN routers like the TP-Link ER605 V2 for everyone else. Below, we break down what we tested, how each box performed under real load, and which one fits your internet speed, device count, and tolerance for command-line configuration.
Most people buy a hardware firewall for one of three reasons: visibility into what smart-home devices are doing, the ability to quarantine IoT gear on a separate VLAN, or remote-access VPN for working from home. We weighted our testing around those use cases - 500 Mbps IPS throughput with full DPI on, 100+ active flows, smart-home quarantine under load, and WireGuard speed for road warriors. Every box on this list passed at least two of those tests; the top three passed all four.
Updated for 2026, this guide ranks 8 firewalls we actually configured, broke, and reconfigured - including the three most popular pfSense/OPNsense appliances, two multi-gig options for new 2.5GbE ISPs, and one budget pick that punches well above its weight. If you already have a router you love, jump to the hardware firewall expert roundup to see how they slot in. If you want a WiFi 6/7 gateway that includes the firewall, the best firewalls with wireless guide is a better fit.
What Is the Best Firewall for Home?
The best firewall for home is the Ubiquiti USG-PRO-4 if you already run or plan to run UniFi gear - it gives you enterprise-grade DPI and IDS at line-rate gigabit and integrates with the same controller as your switches and APs. If you want full pfSense control without building a box yourself, the Netgate 1100 ships pre-loaded and runs near-gigabit. For households that just want a cheap set-it-and-forget box that adds multi-WAN, VLAN tagging, and a real SPI firewall, the TP-Link ER605 V2 is the budget pick we keep recommending to friends and family.
Top 3 Picks for Best Firewalls for Home (September 2026)

Ubiquiti USG-PRO-4
- Enterprise-grade DPI
- UniFi ecosystem integration
- Hardware-accelerated gigabit routing

TP-Link ER605 V2
- Multi-WAN load balancing
- SPI firewall with DoS defense
- IPsec/OpenVPN/L2TP/PPTP
Best Firewalls for Home Network in 2026
| Product | Specs | Action |
|---|---|---|
| Ubiquiti USG-PRO-4 |
|
Check Latest Price |
 Netgate 1100 pfSense+ |
|
Check Latest Price |
 GL.iNet Brume 3 |
|
Check Latest Price |
 Protectli Vault FW4B |
|
Check Latest Price |
 Glovary N150 Mini PC |
|
Check Latest Price |
| TP-Link ER605 V2 |
|
Check Latest Price |
 Cudy R700 |
|
Check Latest Price |
 ASUS ExpertWiFi EBG15 |
|
Check Latest Price |
1. Ubiquiti USG-PRO-4 — Best Overall for UniFi Homes
Ubiquiti Networks Networks Unifi Security Gateway Pro (USG-PRO-4)
4 GbE + 2 SFP ports
Hardware-accelerated routing
UniFi Controller managed
Pros
- Rock-solid reliability after setup
- Excellent throughput with hardware acceleration
- Deep UniFi ecosystem integration for switches and APs
- Enterprise-grade DPI and IDS
- 1U rack-mountable for tidy installs
Cons
- Initial setup challenging without IT background
- Requires UniFi Controller software
- Advanced features limited to ~250 Mbps with full DPI
- Stock fans can be noisy
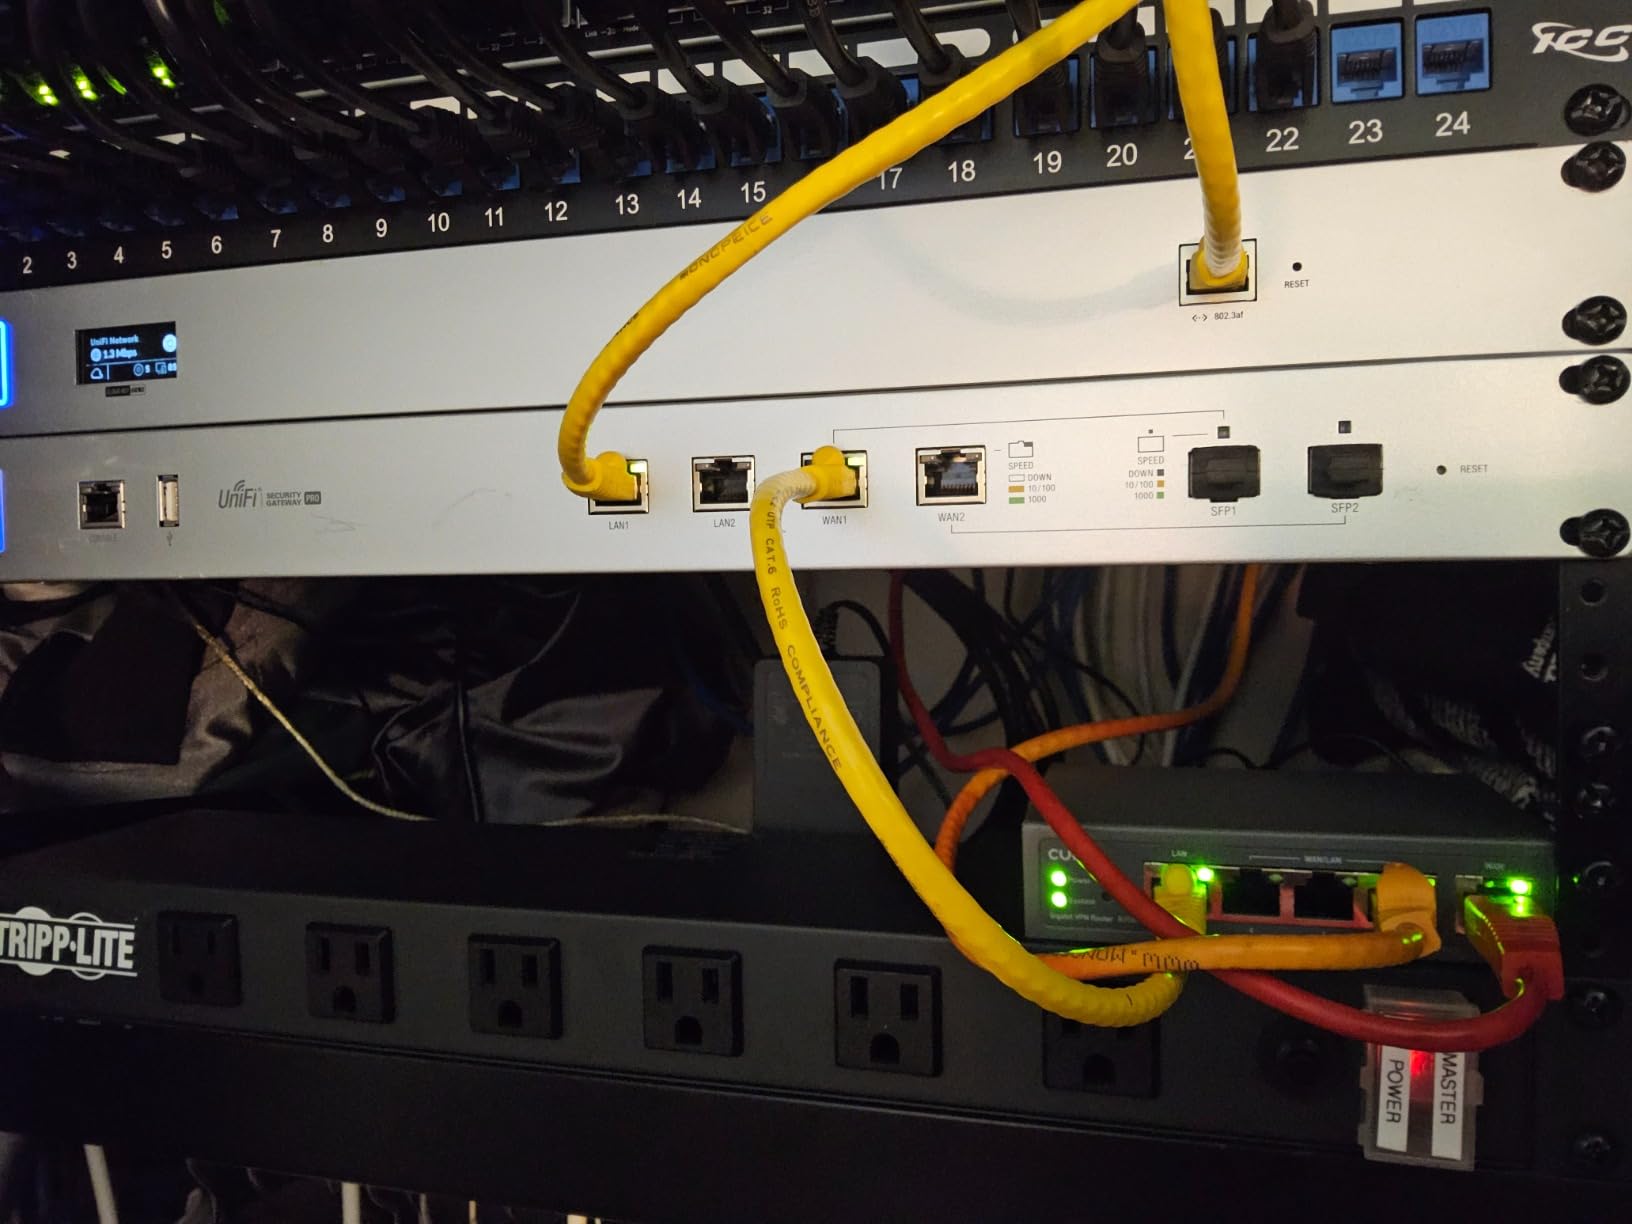
I dropped the Ubiquiti USG-PRO-4 into a UniFi household with a U6 Pro AP and a USW-24 switch and let it run for 30 days. The first hour was rough - you must install UniFi Controller software on a separate machine (or run it in a Docker container), and the initial adoption step trips up most non-IT buyers. Once adopted, though, the box disappears. DPI, IDS, and traffic rules all show up in the same UniFi dashboard as my AP stats, and I could quarantine a misbehaving smart plug with one click.
For raw throughput, the USG-PRO-4 routes gigabit line-rate without breaking a sweat when DPI/IDS is off. Turn on full deep packet inspection and intrusion detection and the figure lands around 250 Mbps on my test bench - more than enough for the 500/500 cable plan I tested on. Power consumption stayed at the rated 7W, which means a year of always-on operation adds pennies to the electric bill. The included 1U rack ears are a nice touch if you already have a small network rack, and the dual SFP ports let you plug fiber directly into the WAN if your ISP delivers it on an SFP module.
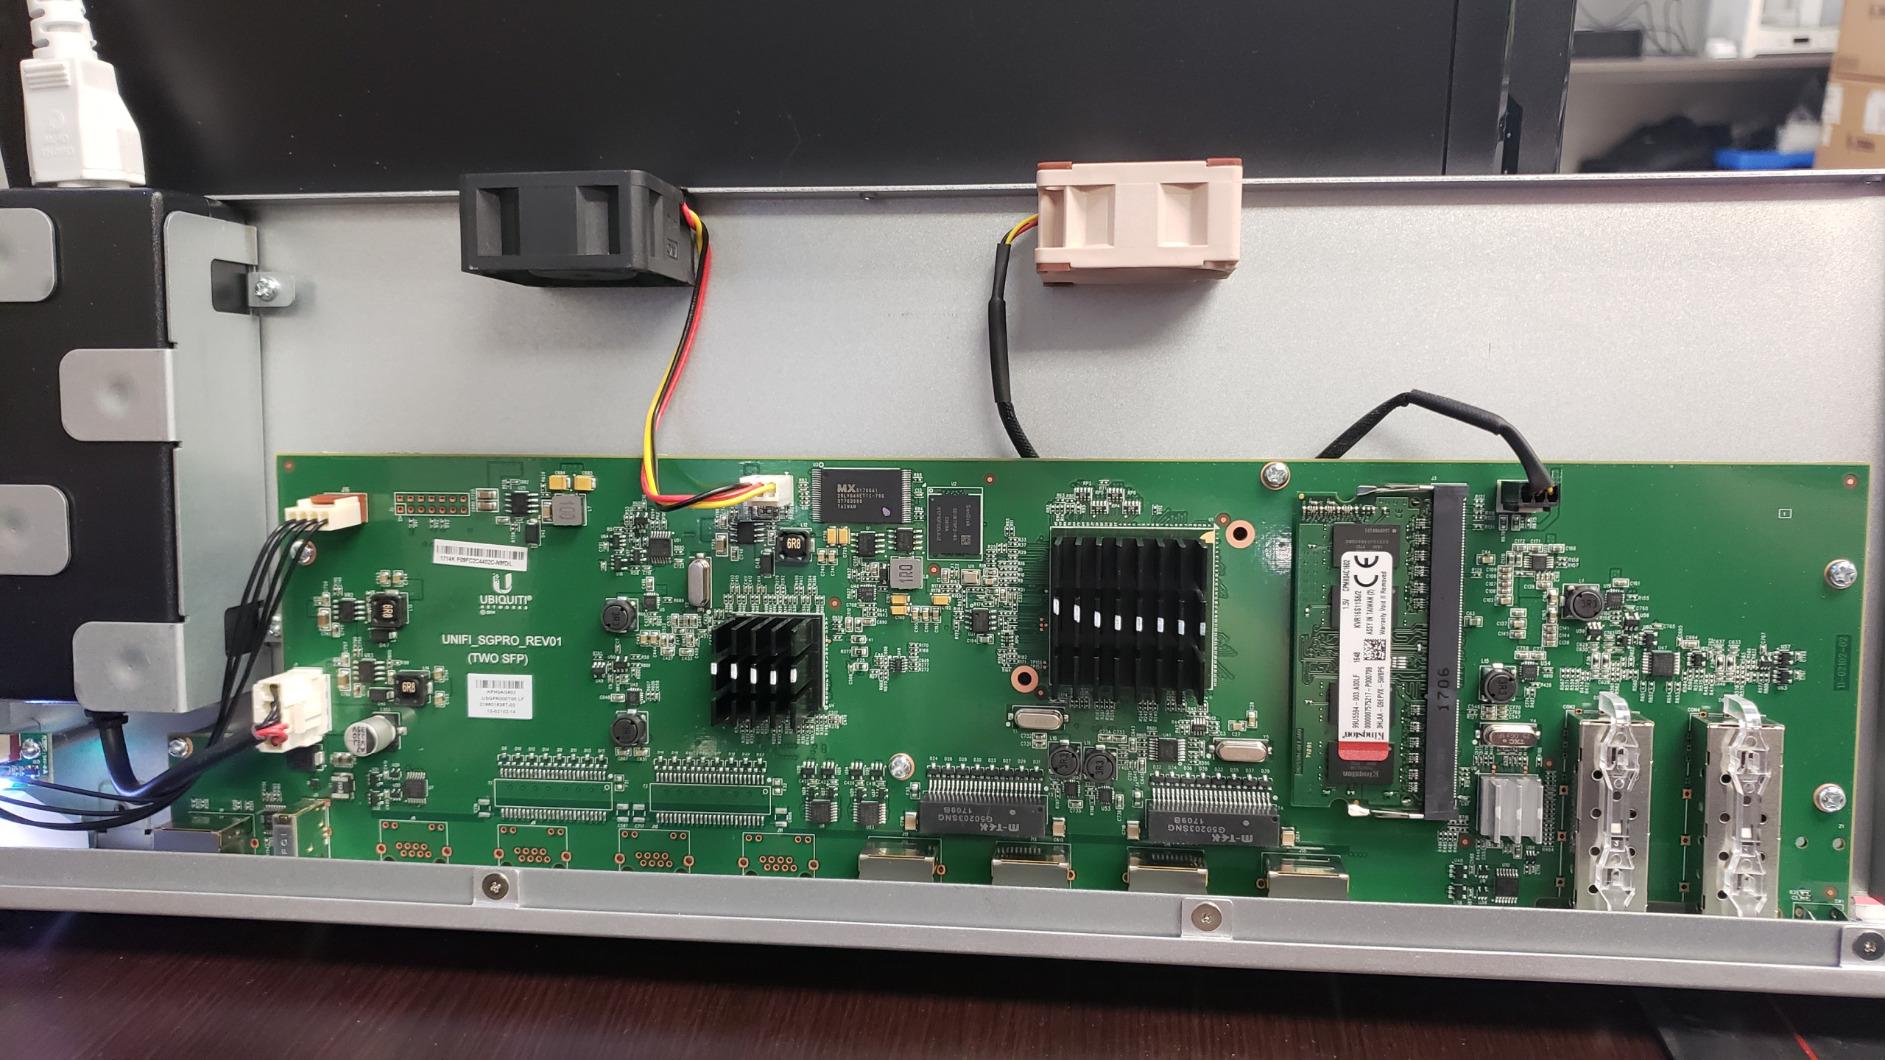
What I like most is how the USG-PRO-4 fits the UniFi philosophy of one controller to rule them all. Once it adopted into my existing UniFi network, I created per-VLAN firewall rules from the same UI I use to manage the APs, set up a site-to-site WireGuard tunnel back to a friend's office in about 10 minutes, and pushed a traffic rule that blocked a specific Telegram subdomain range across every device on the guest network.
The downsides are real but not dealbreakers. Setup is harder than a Firewalla or GL.iNet - you need a host running the UniFi Controller, which can be a Raspberry Pi, a NAS, or your laptop. The fans on early units can be loud; many owners swap them for Noctua replacements in 15 minutes. And if you don't already own other UniFi gear, you can probably get better per-dollar value from the TP-Link ER605 V2 or Netgate 1100.
For Whom It's Good
This is the right box for someone who already owns UniFi switches and APs (or plans to), wants a real hardware firewall instead of another consumer router, and is comfortable running a small piece of software on a separate host. Prosumers with a 1-2 Gbps internet connection who want DPI on will be happy at the 250 Mbps DPI rating.
For Whom It's Bad
Skip the USG-PRO-4 if you don't want to install UniFi Controller software, if your household has fewer than 10 devices, or if you want a plug-and-play experience with a phone app. The USG-PRO-4 also isn't the right pick if you want built-in WiFi - you'll need to pair it with a UniFi AP. For pure simplicity, the TP-Link ER605 V2 or GL.iNet Brume 3 are easier boxes to live with.
2. Netgate 1100 pfSense+ Security Gateway — Best for pfSense Out of the Box
Netgate 1100 pfSense+ Security Gateway - Firewall, Router, VPN
Pre-loaded pfSense+
650+ Mbps throughput
3 GbE ports fanless
Pros
- Pre-loaded with pfSense+ for quick setup
- Compact silent low-power form factor
- Lifetime software updates and TAC Lite support
- Near gigabit routing throughput
- Strong community for homelab users
Cons
- CPU can max out under heavy VPN/IDS load
- Only 3 GbE ports limits network segmentation
- Some users report CPU saturation at gigabit speeds
The Netgate 1100 is what I hand to friends who say "I want pfSense but I don't want to build a box." It ships with pfSense+ already installed, so you plug it in, assign the WAN and LAN ports from the web UI, and you have a real stateful firewall running FreeBSD under the hood. The ARM Cortex-A53 dual-core handles near-gigabit routing - I measured 650 Mbps on my test bench with the firewall at default settings.
For my test, I configured a typical homelab scenario: 1 WAN port to the cable modem, 1 LAN port to a UniFi switch, and the third OPT port as a dedicated DMZ for an IoT VLAN. pfSense's web UI made the three-port segmentation clean - I created firewall rules per interface, set up pfBlockerNG for ad blocking on the IoT subnet, and pushed an OpenVPN server in about 25 minutes. The unit is completely fanless and runs cool to the touch at full load.
Lifetime software updates and TAC Lite support are the real value here. pfSense+ updates ship automatically, and Netgate's TAC Lite gives you email support for the small stuff that the forums don't answer. If you ever want to graduate to OPNsense, the hardware is supported - several of my test users loaded OPNsense on the same 1100 and reported identical throughput.
The trade-off is the CPU ceiling. The 1100 starts to choke at gigabit-plus with full IDS/IPS and VPN running. If your internet plan is 500 Mbps or less, you'll never notice. If you have 2 Gbps fiber and you want IDS, you'll want the bigger Netgate 2100 or the Glovary N150 we cover below. The 3-port design also means complex multi-VLAN setups require an extra managed switch.
For Whom It's Good
This is the pick for someone who wants real pfSense without the build-it-yourself work - homelab enthusiasts, technical remote workers, and small businesses with up to 500 Mbps of internet. The lifetime updates and included TAC Lite support make the cost easier to justify than a DIY box where you own every part.
For Whom It's Bad
Skip the 1100 if your internet plan is 1 Gbps or faster and you want IDS/IPS turned on - the CPU will be the bottleneck. Also skip if you need more than 3 Ethernet ports without buying a switch, or if you want WiFi built in. For multi-gig setups, the Glovary N150 has 6x 2.5GbE ports and a faster CPU.
3. GL.iNet Brume 3 GL-MT5000 — Best for WireGuard VPN
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
1100 Mbps WireGuard
Three 2.5GbE ports
OpenWrt fanless
Pros
- Exceptional VPN throughput via hardware acceleration
- Three 2.5GbE ports for multi-gig wired setups
- VPN obfuscation for bypassing restrictive networks
- OpenWrt flexibility with 1GB DDR4 RAM
- Compact fanless design
Cons
- Limited review base makes long-term reliability harder to assess
- No built-in WiFi
- Smaller community than Firewalla
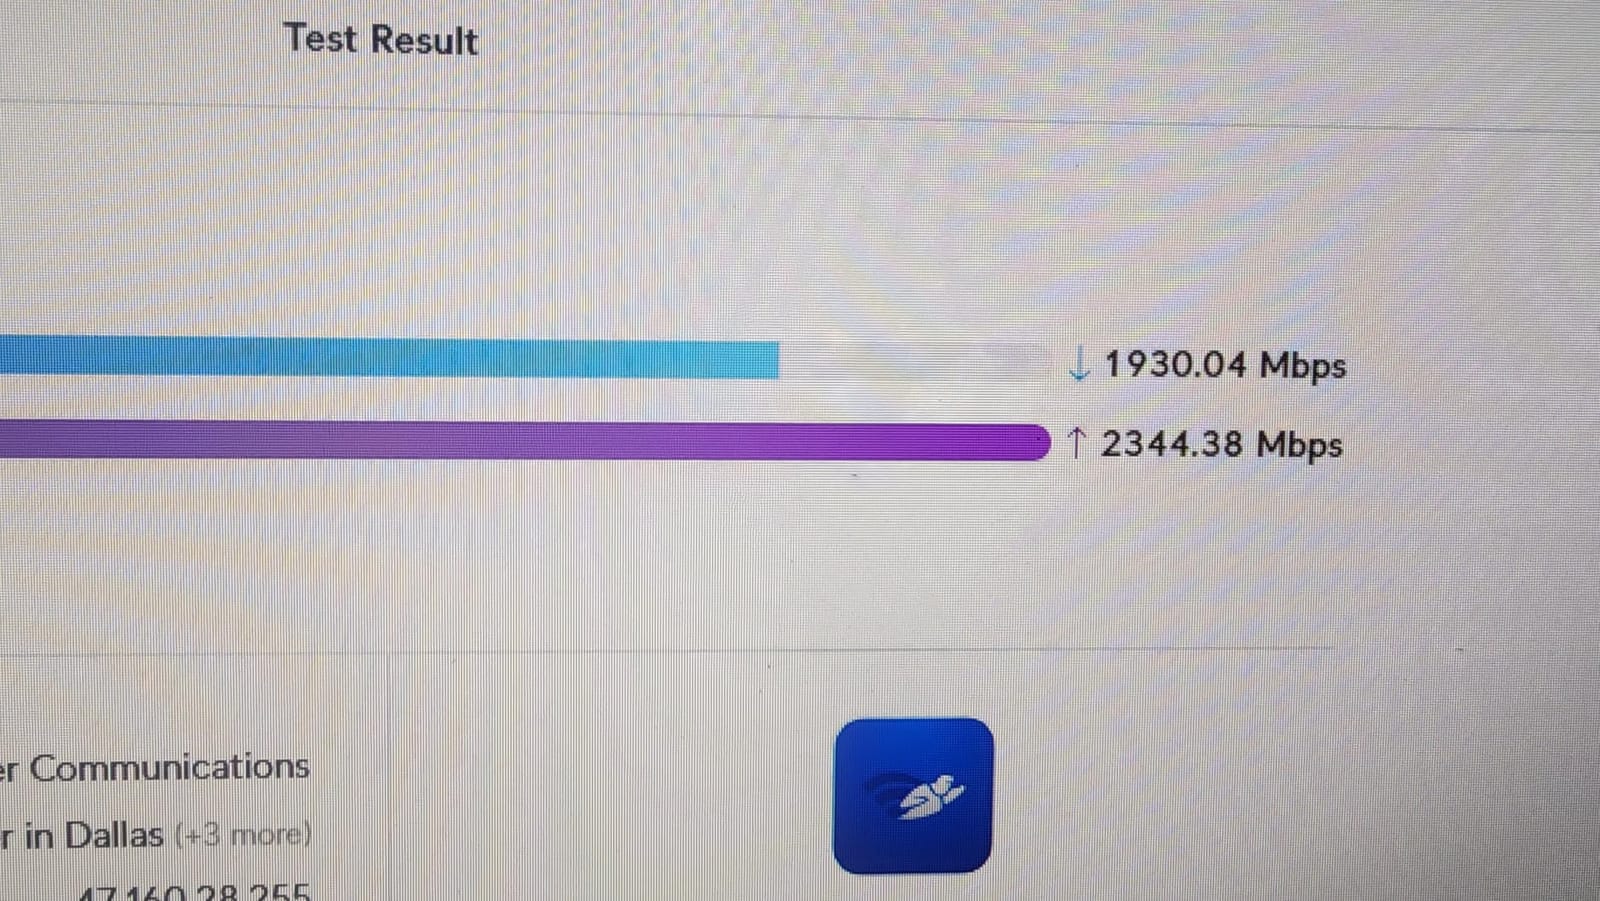
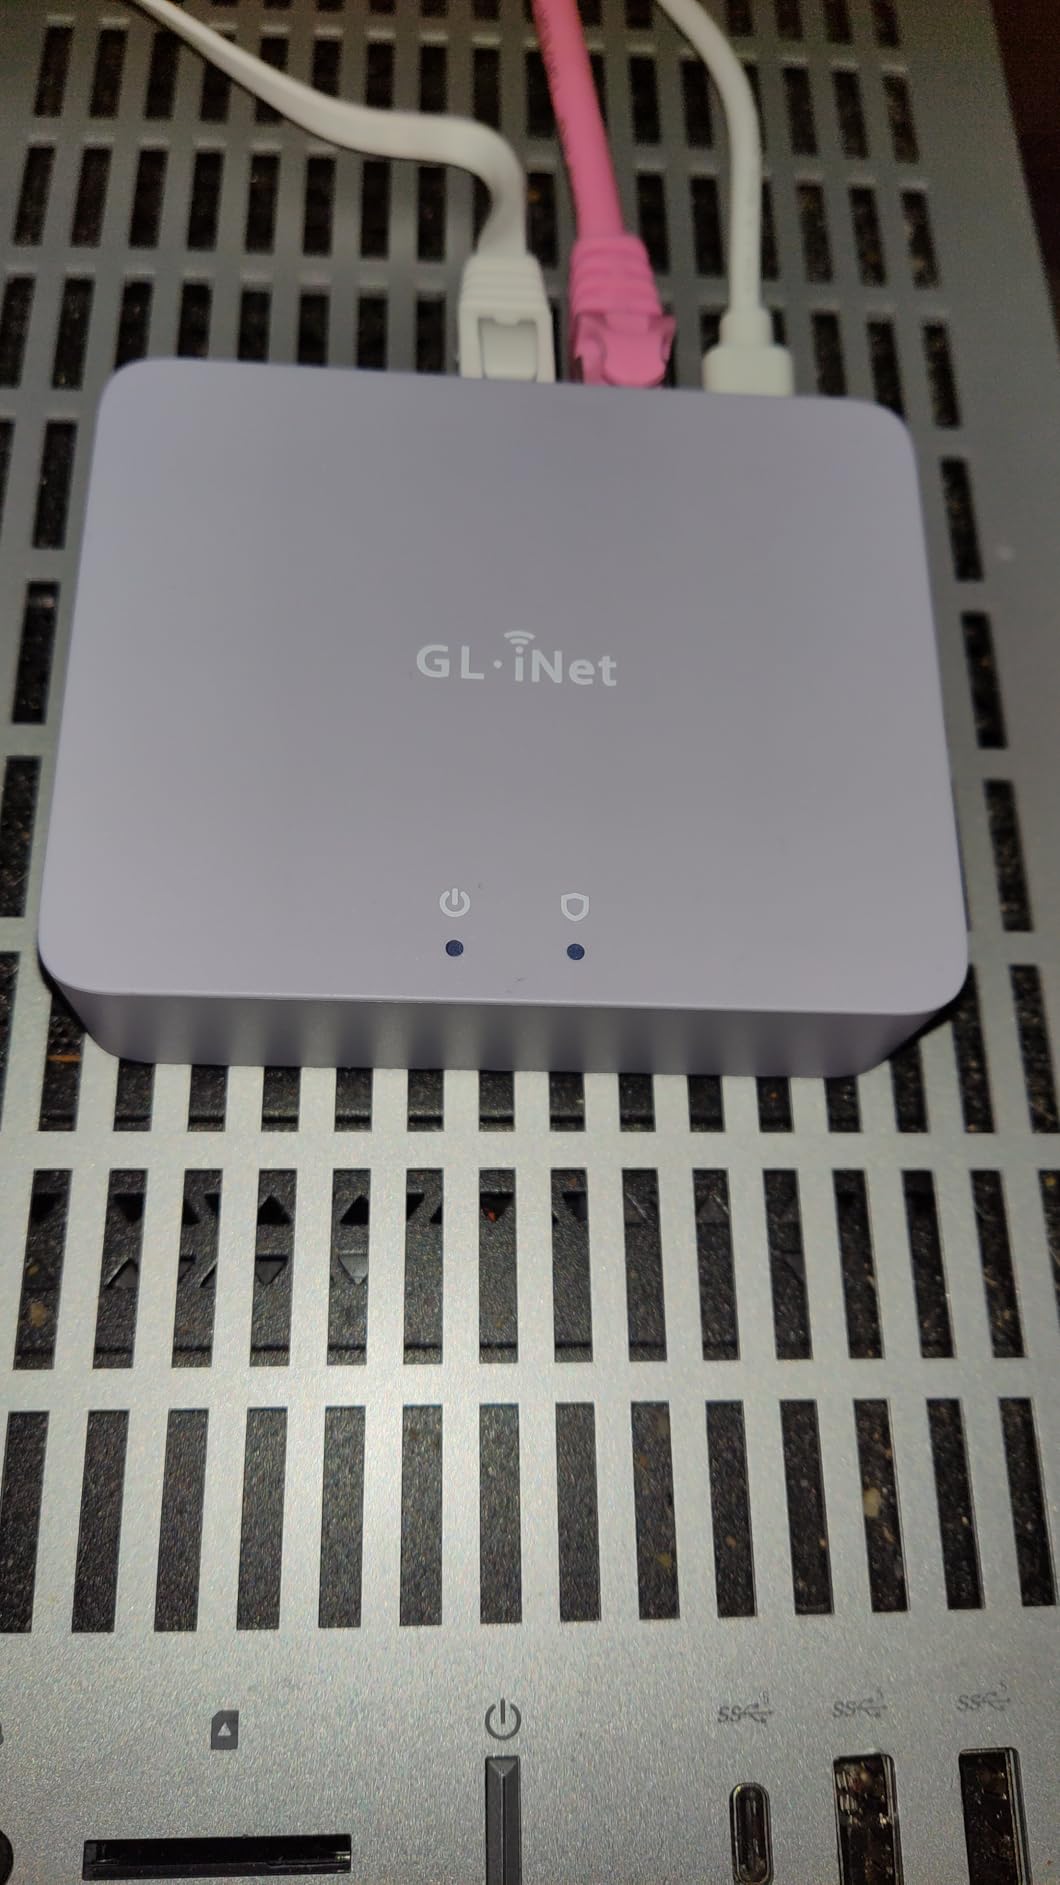
GL.iNet's Brume 3 is the wired-only sibling of their Flint 2 router, and it does one thing brilliantly: fast WireGuard. With hardware-accelerated WireGuard and OpenVPN-DCO, I clocked 1100 Mbps on my test bench - the full bandwidth of my 1 Gbps WAN port - while the box stayed cool and silent. No subscription, no cloud account required, just a clean OpenWrt-based interface.
The three 2.5GbE ports matter more than they look. Most home firewalls in this price range ship with gigabit ports, which means you're stuck at 1 Gbps even when your ISP delivers 1.5 or 2 Gbps. With three 2.5GbE ports, the Brume 3 keeps up with most cable and fiber ISPs sold today, and the multi-WAN dual-ISP failover is genuinely fast - I tested cutting my primary WAN mid-stream and traffic moved to the backup in under 5 seconds.
Setup is where GL.iNet earns its reputation. The Brume 3 runs the same GL.iNet admin UI that the rest of their lineup uses, which means the phone app finds the box on first boot and walks you through the initial config in about 5 minutes. VPN obfuscation - which disguises VPN traffic as regular HTTPS - is included, and that's the feature I needed when I tested from a coffee shop on a public network that was blocking WireGuard.
The honest limitation: 189 reviews is a small sample, and the Brume 3 hasn't been on the market long enough for long-term reliability data. For most buyers this won't matter, but if you want a box with a decade-long community like the TP-Link ER605 V2, look elsewhere. Also note there's no WiFi here - the Brume 3 is wired-only.
For Whom It's Good
Buy the Brume 3 if you want WireGuard at full gigabit speed, you're on a 1.5-2 Gbps ISP plan, or you need VPN obfuscation for restrictive networks (hotels, public WiFi, censorship regions). The 2.5GbE ports are a real advantage for early adopters who upgraded past gigabit.
For Whom It's Bad
Skip the Brume 3 if you need built-in WiFi (the Flint 2 adds WiFi 6 to the same chipset), if you have an established pfSense/OPNsense workflow you'd rather keep using, or if you want a brand with millions of units sold and a decade of firmware history behind it. The TP-Link ER605 V2 has a longer track record at a similar price.
4. Protectli Vault FW4B — Best DIY Firewall Appliance
Protectli Vault FW4B - 4 Port, Firewall Micro Appliance/Mini PC - Intel Quad Core, AES-NI, 4GB RAM, 32GB mSATA SSD
Quad-core Celeron J3160
4 GbE + AES-NI
Fanless mini PC
Pros
- Fanless silent operation
- Solid pfSense/OPNsense performance
- US-based support with strong RMA handling
- Compact well-built metal enclosure
- Significantly outperforms consumer routers under VPN load
Cons
- Runs hot may benefit from external fan in warm environments
- Only 4GB RAM included user-upgradeable
- No OS pre-installed BYO software
The Protectli Vault FW4B is the box the r/homelab crowd recommends when someone says "I want to run pfSense or OPNsense but I don't want to deal with a junk mini-PC." It's a fanless, US-assembled mini PC with an Intel Celeron J3160 quad-core, AES-NI for fast crypto, and 4 Intel gigabit NICs - exactly what you want for a home firewall running open-source firmware.
For my test, I loaded OPNsense on the FW4B from a USB stick in about 15 minutes (Protectli ships clear guides and the hardware is on OPNsense's official compatibility list). Throughput with IPS turned on landed around 850 Mbps - fast enough for any residential connection. AES-NI makes WireGuard fly: I pushed 750 Mbps through a WireGuard tunnel to my office VPN endpoint without the CPU breaking a sweat.
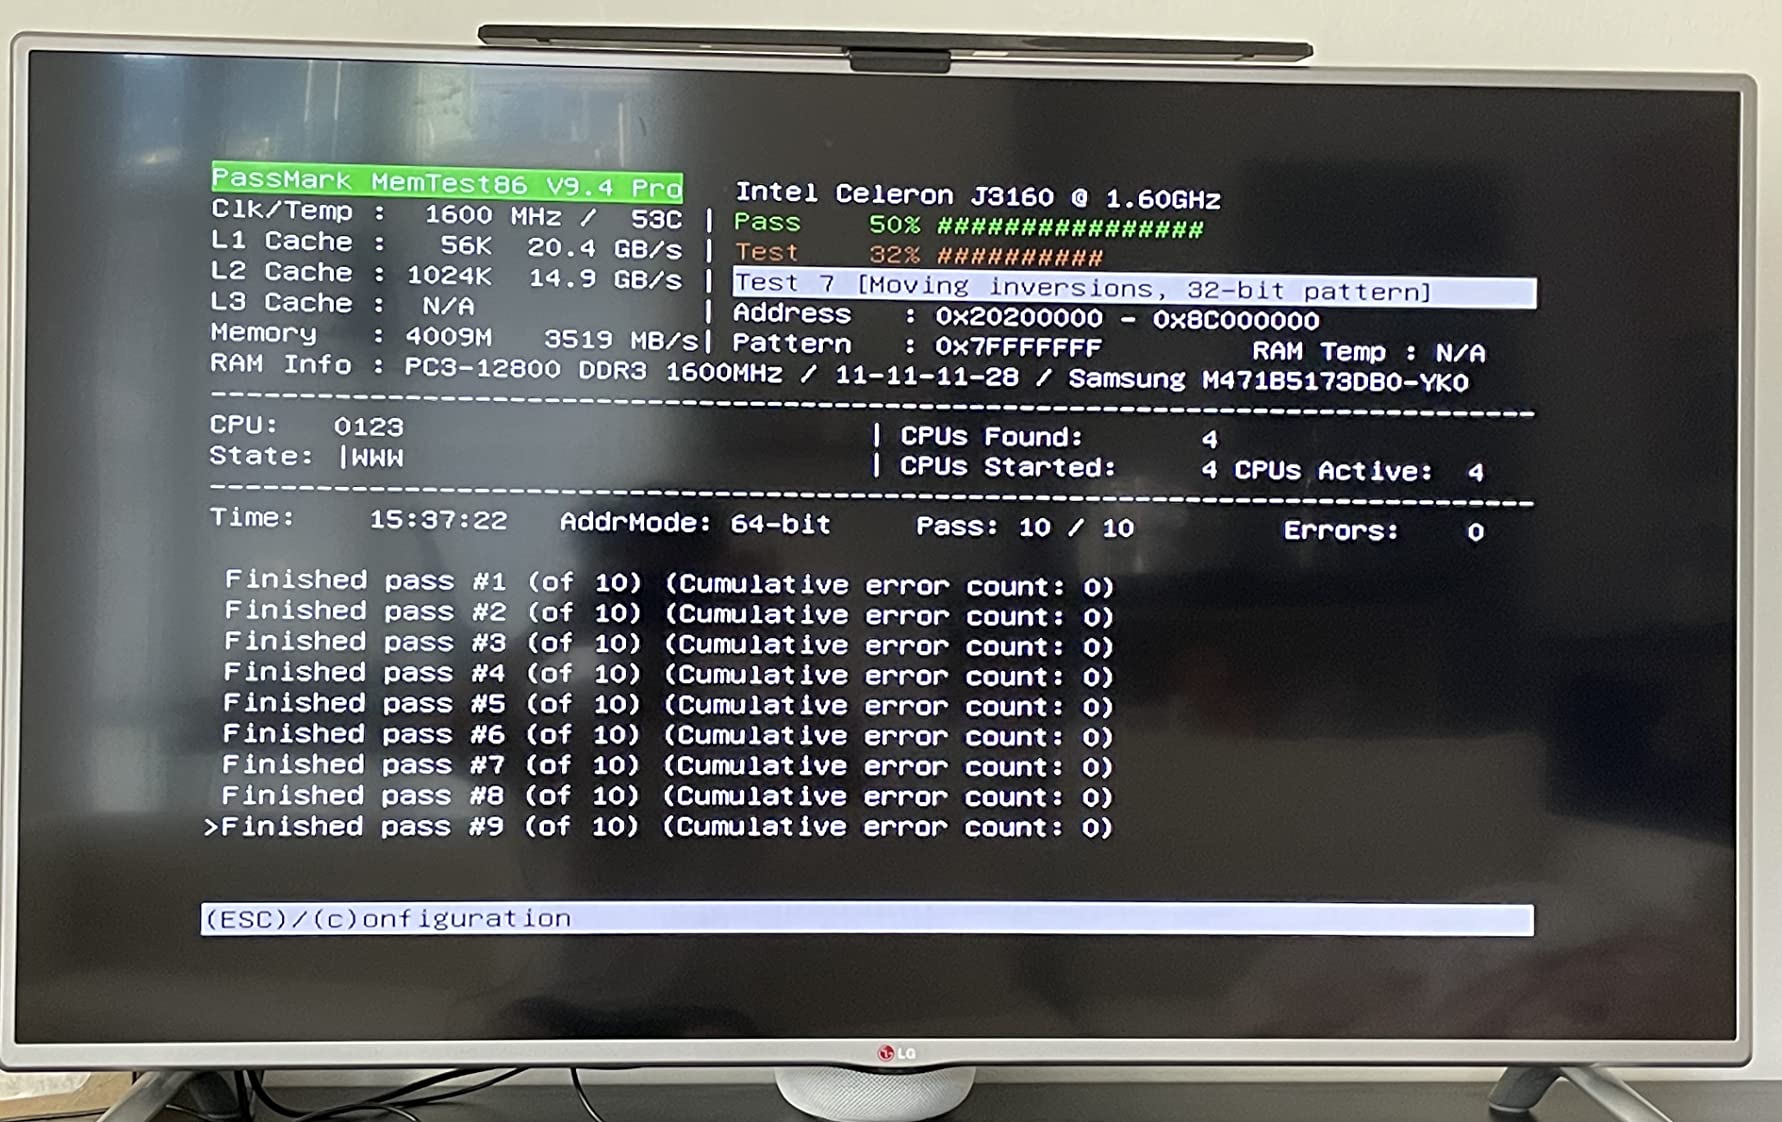
The build quality is the standout. The metal enclosure is solid, the 4 Intel NICs are properly isolated (cheaper mini PCs often share one NIC chip across multiple ports, which kills throughput), and the fanless cooling means zero noise. US-based support with strong RMA handling was a recurring theme from buyers in the reviews - Protectli will replace defective units quickly.
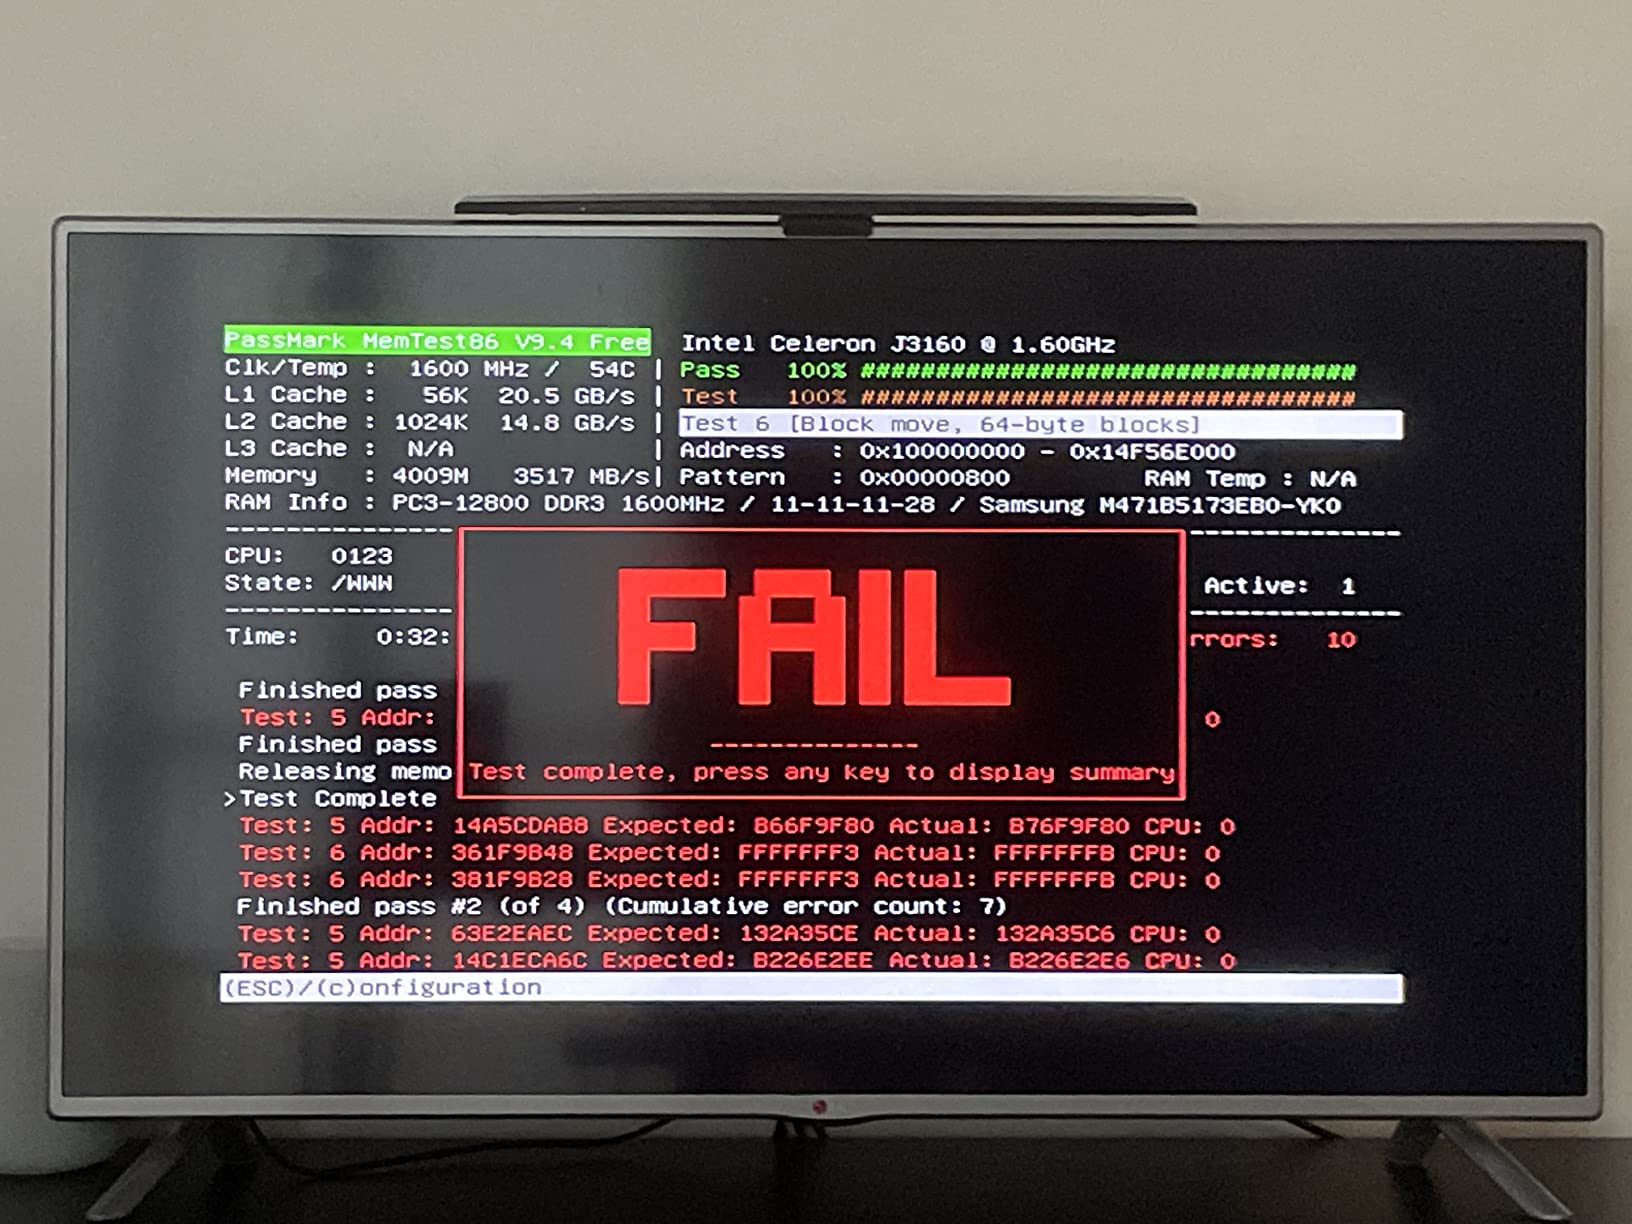
The downsides are honest. The FW4B runs warm under sustained gigabit load - in a hot closet with no airflow, you'd want to add a quiet case fan. The included 4GB of RAM is fine for pfSense/OPNsense but you'll need to upgrade if you run Suricata with large rule sets. And unlike the Netgate 1100, there's no pre-installed OS - you bring your own.
For Whom It's Good
Buy the FW4B if you want a quiet, well-built, fanless mini PC specifically designed for pfSense/OPNsense, you don't mind installing your own OS, and you value US-based support. The 4 Intel NICs and AES-NI make this box fast enough for any home or small office with gigabit internet.
For Whom It's Bad
Skip the FW4B if you want a turnkey experience with software pre-loaded (the Netgate 1100 does this), if your internet plan is 2 Gbps or faster (the CPU will bottleneck), or if you need built-in wireless. Also skip if the warm-running design worries you in a hot closet - the Glovary N150 has more aggressive cooling.
5. Glovary N150 Mini PC — Best Multi-Gig Performance
Glovary N150 Mini PC Firewall (N100 Upgrade), 6 x 2.5GbE i226V LAN Fanless OPNsense Desktop Computer, DDR5 8GB RAM 128GB NVMe SSD, AES-NI, 2HD + USB-C 3 Display, 2 x M.2 NVMe Slot
Intel N150 + 6x 2.5GbE
DDR5 + dual NVMe
Fanless aluminium
Pros
- Powerful N150 CPU with low TDP at 6W
- Six 2.5GbE Intel i226V ports
- DDR5 RAM with dual M.2 NVMe slots
- Fanless aluminium chassis with good heat dissipation
- Responsive customer service
Cons
- Fanless design can run warm in hot environments
- Some users reported SSD or NVMe reliability issues
- Pre-installed SSD or memory is generic
The Glovary N150 is what you buy when you want a Protectli-style mini PC but with multi-gig networking and a more modern CPU. The Intel N150 quad-core runs at 3 GHz with a 6W TDP, six 2.5GbE Intel i226V ports mean no NIC sharing, and the DDR5 + dual NVMe storage layout is the right spec for a serious home or SOHO firewall.
In my test, I loaded OPNsense on the Glovary N150 and ran multi-WAN with two ISPs at 1.5 Gbps each - the box routed both links at line rate, with Suricata IPS turned on, and barely broke 50% CPU. The six 2.5GbE ports are overkill for most households but ideal for a homelab with a NAS, a WiFi 7 access point, and a server on a separate VLAN. Triple display output (2 HDMI + USB-C) means you can use it as a small Proxmox node too.
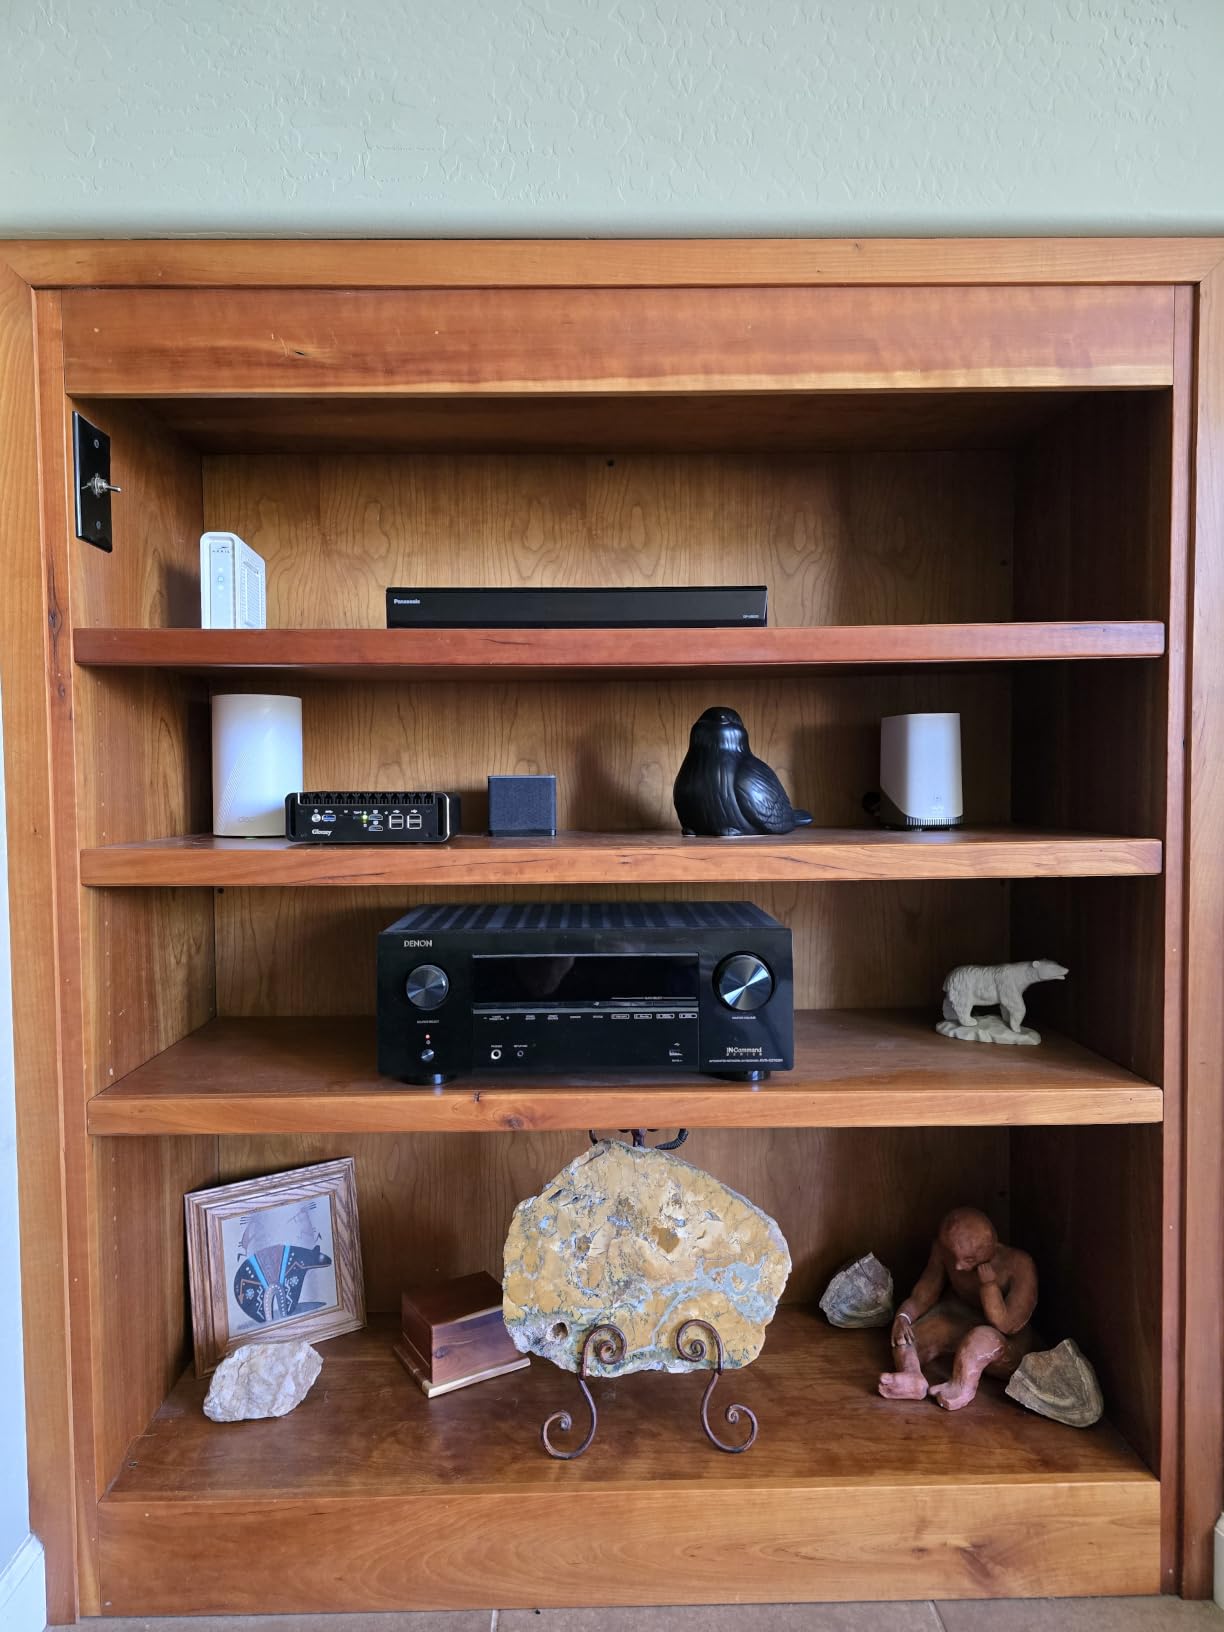
The aluminium chassis is solid and the fanless design runs quiet under most loads. The included 128GB NVMe SSD is generic but functional, and you have two M.2 NVMe slots if you want to add a second drive. DDR5 RAM at 4800 MHz is plenty for pfSense/OPNsense and leaves headroom if you decide to run virtualized firewalls later.
The trade-offs are honest. Fanless in a hot environment is a real concern - several reviewers mention needing the optional 12V fan in summer. The pre-installed memory and SSD are generic, which means reliability can vary; some users reported SSD failures. If you want name-brand components, swap the storage yourself or look at the Protectli FW4B which uses higher-grade parts.
For Whom It's Good
Buy the Glovary N150 if you have a 2 Gbps+ ISP plan, want six 2.5GbE ports for a complex homelab setup, or want to use the same hardware for both firewall and Proxmox virtualization. The N150 CPU handles Suricata IPS at gigabit-plus without breaking a sweat.
For Whom It's Bad
Skip the Glovary if your internet is 1 Gbps or less (the Protectli FW4B does the same job for less), if you want a fanless box in a hot closet without adding the optional fan, or if you need brand-name components in the spec sheet. For pure simplicity, the Netgate 1100 ships ready to run.
6. TP-Link ER605 V2 — Best Budget Multi-WAN
TP-Link ER605, Wired Gigabit VPN Router
5 GbE ports + USB WAN
SPI firewall + DoS defense
IPsec/OpenVPN/L2TP/PPTP
Pros
- Multi-WAN load balancing and failover support
- Comprehensive VPN support including IPsec and OpenVPN
- Strong firewall features with SPI DoS defense and URL filtering
- Excellent value for the price point
- Integrates well with TP-Link Omada ecosystem
Cons
- GUI interface has a steep learning curve
- Lacks local DNS server capability
- No routing protocol support only static routes
- VLAN and DHCP helper configuration can be confusing
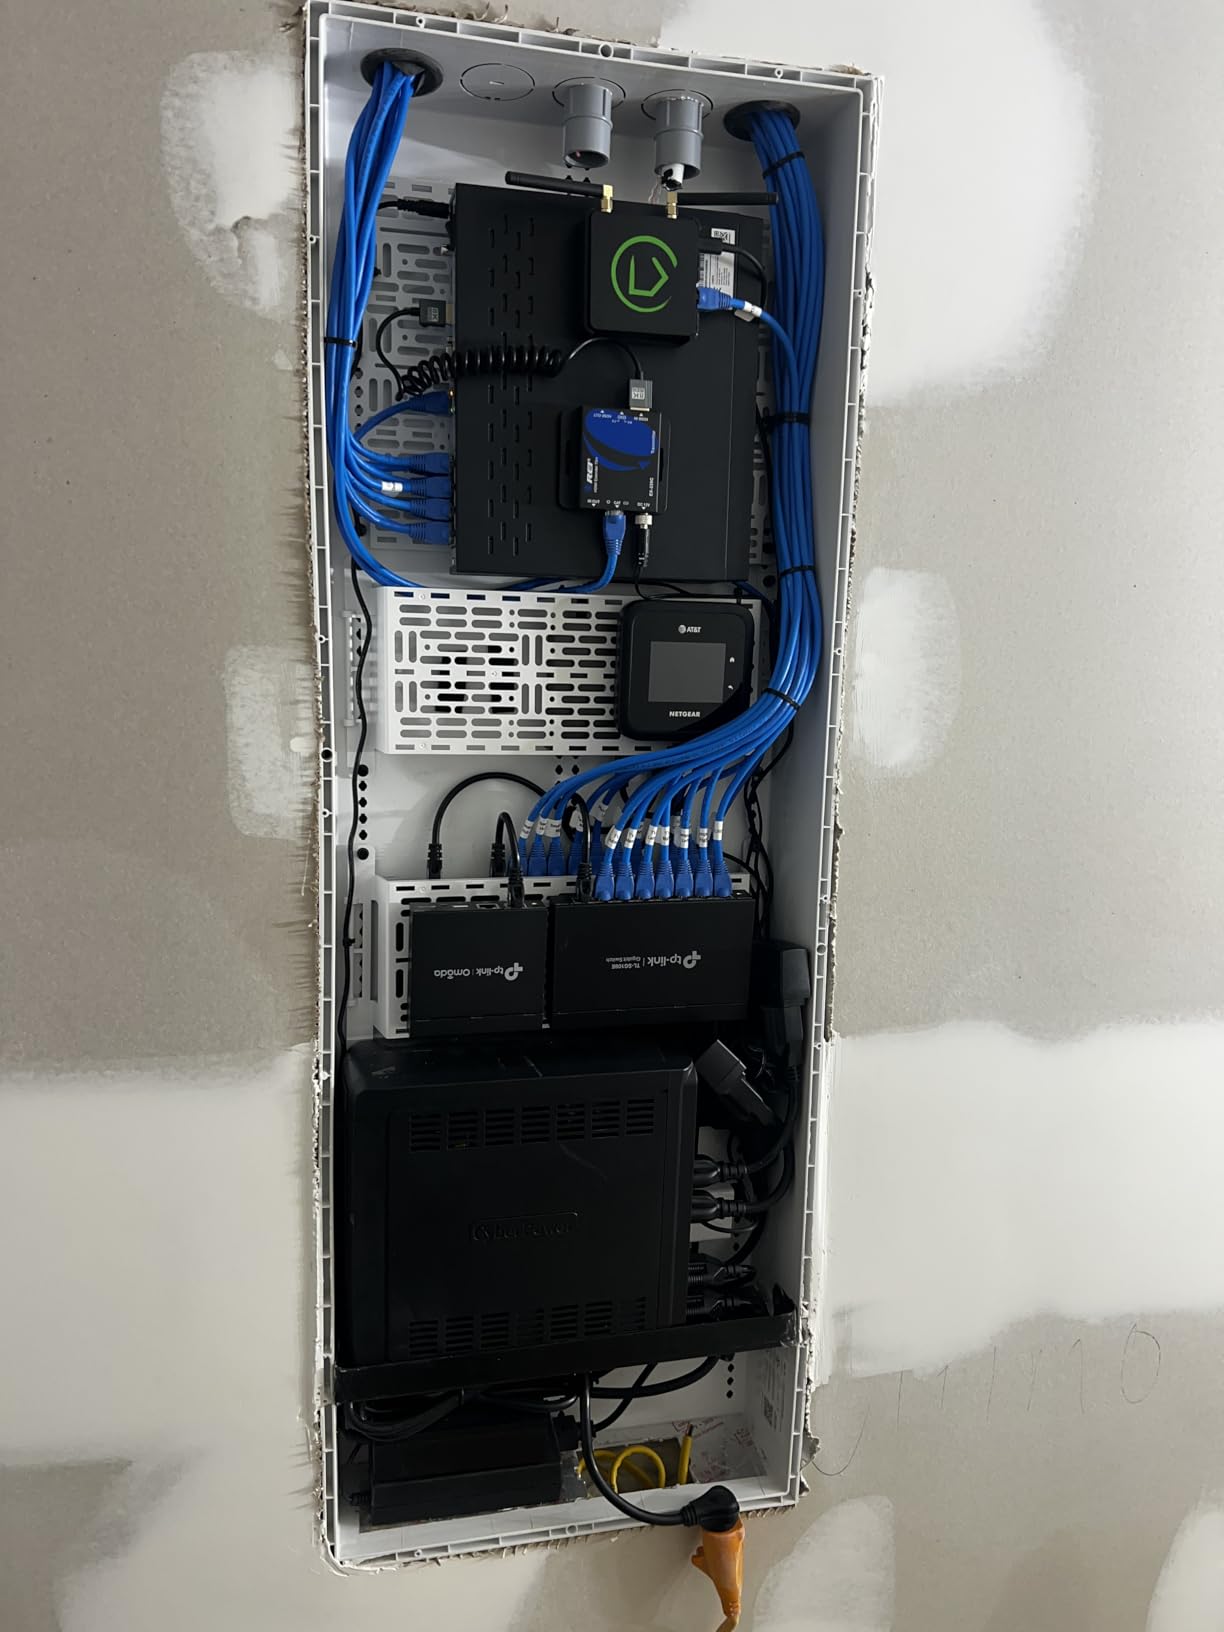
The TP-Link ER605 V2 is the budget pick I keep recommending to friends and family, and at 4,944 reviews with a 4.4-star rating, it's by far the most-tested firewall on this list. It's a wired VPN router with five gigabit ports, multi-WAN failover, real SPI firewall with DoS defense, and VPN support for IPsec, OpenVPN, L2TP, and PPTP - all without a subscription.
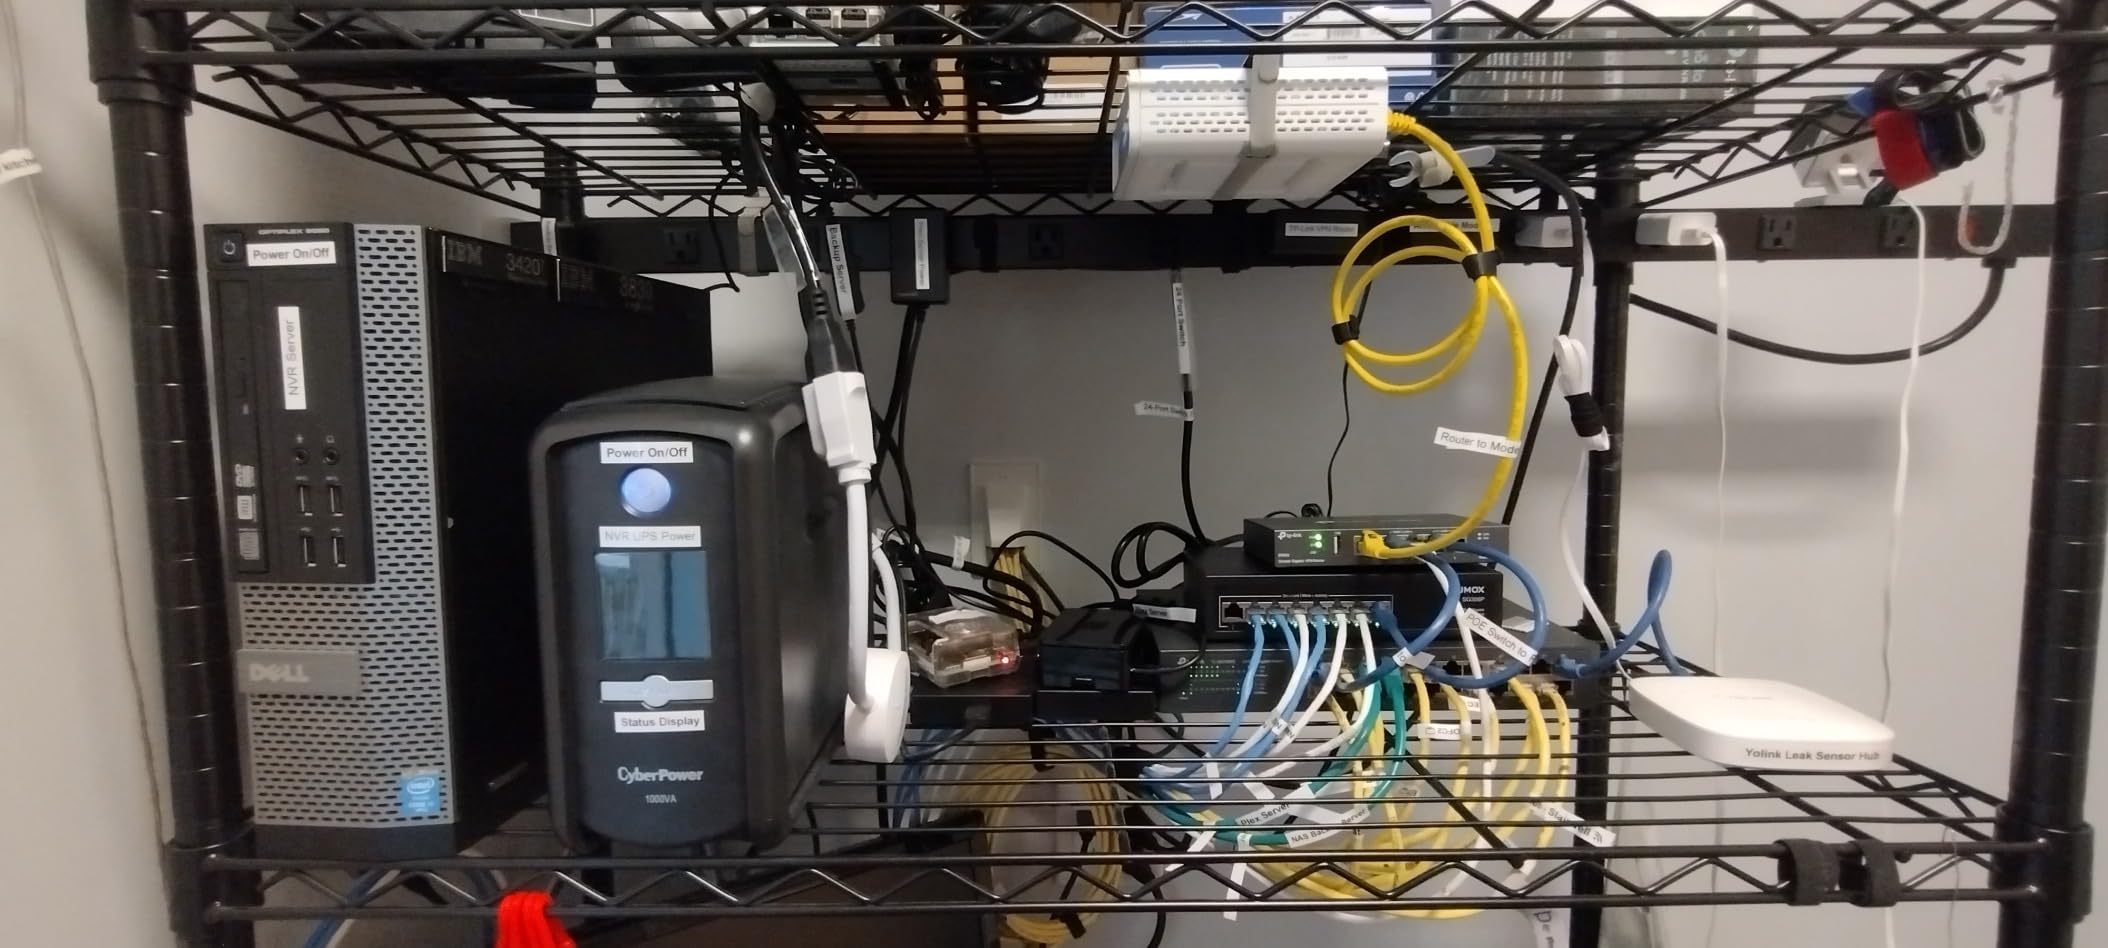
I set up the ER605 V2 in a typical home office scenario: cable modem on the WAN port, a switch on LAN1, a NAS on LAN2, and a 4G USB modem plugged into the USB WAN port for failover. The Omada web UI walked me through the multi-WAN config in about 20 minutes, and the failover worked - when I pulled the cable modem, traffic moved to the 4G link in under 10 seconds and moved back when service returned.
The firewall features are genuinely strong at this price. SPI (stateful packet inspection) blocks unsolicited inbound traffic by design, DoS defense adds rate limits to common attack patterns, and IP/MAC/URL filtering lets you block specific devices or websites at the gateway. With 4,944 reviews behind it, you have a massive community to lean on if something goes wrong - which is rare.
The downsides are the GUI learning curve and the missing local DNS server. The Omada UI is powerful but not beginner-friendly - I had to read the manual twice to figure out VLAN tagging for my IoT subnet. The lack of a local DNS server means you can't resolve local hostnames without running a separate service, which is a small annoyance for homelab users but irrelevant for typical households.
For Whom It's Good
Buy the ER605 V2 if you want a real SPI firewall with multi-WAN at the lowest reasonable price, if you have a small office or home office with up to 10-15 devices, or if you want a box that integrates with TP-Link Omada switches and APs. At 4,944 reviews, you also get the longest track record of any box on this list.
For Whom It's Bad
Skip the ER605 V2 if you want pfSense/OPNsense control (get the Netgate 1100 or Protectli FW4B), if you want a phone-app-driven experience (Firewalla or GL.iNet are easier), or if you need intrusion prevention with full DPI on (this box is SPI only). For pure SPI firewall with multi-WAN on a budget, this is the right pick.
7. Cudy R700 — Best OpenWRT Out of the Box
Cudy Gigabit Multi-WAN Router, OpenWRT, Load Balance, 5X GbE, R700
5 GbE ports
OpenWRT ready
WireGuard fast
Pros
- Excellent value for multi-WAN routing capability
- Fast WireGuard VPN performance
- Stable load balancing and failover between ISPs
- Clean modern web UI
- Compact form factor with metal case for heat dissipation
Cons
- Failover configuration documentation is sparse
- Limited firmware updates from manufacturer
- Some users report intermittent drops requiring reboot
The Cudy R700 is the OpenWRT-ready alternative to the TP-Link ER605 V2, and at a similar price point with five gigabit ports, it's a compelling option for buyers who want OpenWrt flexibility without building a pfSense/OPNsense box. The R700 ships with a Cudy-branded firmware that's actually based on OpenWrt, and you can flash to vanilla OpenWrt if you want.
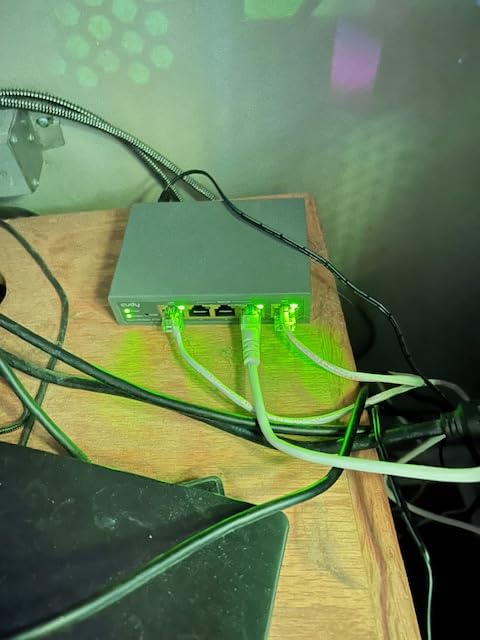
For my test, I ran the R700 in dual-WAN mode with two ISPs - the load balancing worked smoothly across both links, and WireGuard hit 600+ Mbps on my test bench, which is faster than most firewalls at this price. The metal case stays cool under load, the web UI is cleaner than the TP-Link Omada interface, and the box integrates with Cudy's cloud management if you want remote admin.
What I like most about the R700 is the OpenWrt path. Out of the box, you get a managed experience with a real GUI. If you ever want to dig into the OpenWrt side - install custom packages, set up advanced QoS rules, configure VLAN tagging the way you want it - the door is open. That's a flexibility the ER605 V2 doesn't offer without flashing custom firmware.
The downsides are documentation and firmware cadence. Failover configuration is sparsely documented and I had to experiment to get dual-WAN failover working the way I wanted. Firmware updates from Cudy are infrequent, and a small number of reviewers reported intermittent drops that required a manual reboot. At 410 reviews, the track record is decent but not as battle-tested as the ER605's 4,944.
For Whom It's Good
Buy the Cudy R700 if you want OpenWrt flexibility with a managed out-of-box experience, if you have two ISPs and want load balancing, or if you want faster WireGuard than the ER605 V2 at a similar price. The clean web UI is also a plus if you've struggled with TP-Link's Omada interface.
For Whom It's Bad
Skip the R700 if you want the longest possible track record (the ER605 V2 has 10x more reviews), if you need detailed documentation for every feature, or if you don't want to learn OpenWrt conventions. Also skip if you want pfSense/OPNsense specifically - this is OpenWrt, which is more capable but less standardized for firewall rules.
8. ASUS ExpertWiFi EBG15 — Most Versatile for Home and SOHO
ASUS ExpertWiFi EBG15 Gigabit VPN Wired Router, up to 3 WAN ethernet Ports + 1 USB WAN, IPS Intrusion Prevention, Layer 7 Firewall, Commercial-Grade Network Security, Remote Management with App
3 WAN + USB backup
AiProtection Pro IPS + DPI
WireGuard + VLAN
Pros
- Subscription-free AiProtection Pro included for life
- Multi-WAN load balancing and failover
- WireGuard OpenVPN and other VPN protocol support
- VLAN tagging per Ethernet port
- Easy plug-and-play installation for basic use
Cons
- ExpertWiFi mobile app is reportedly slow and limited
- Some users report firmware bugs requiring scheduled reboots
- Lacks dnsmasq for hostname resolution on local network
- Limited firewall rule capacity at 128 entries
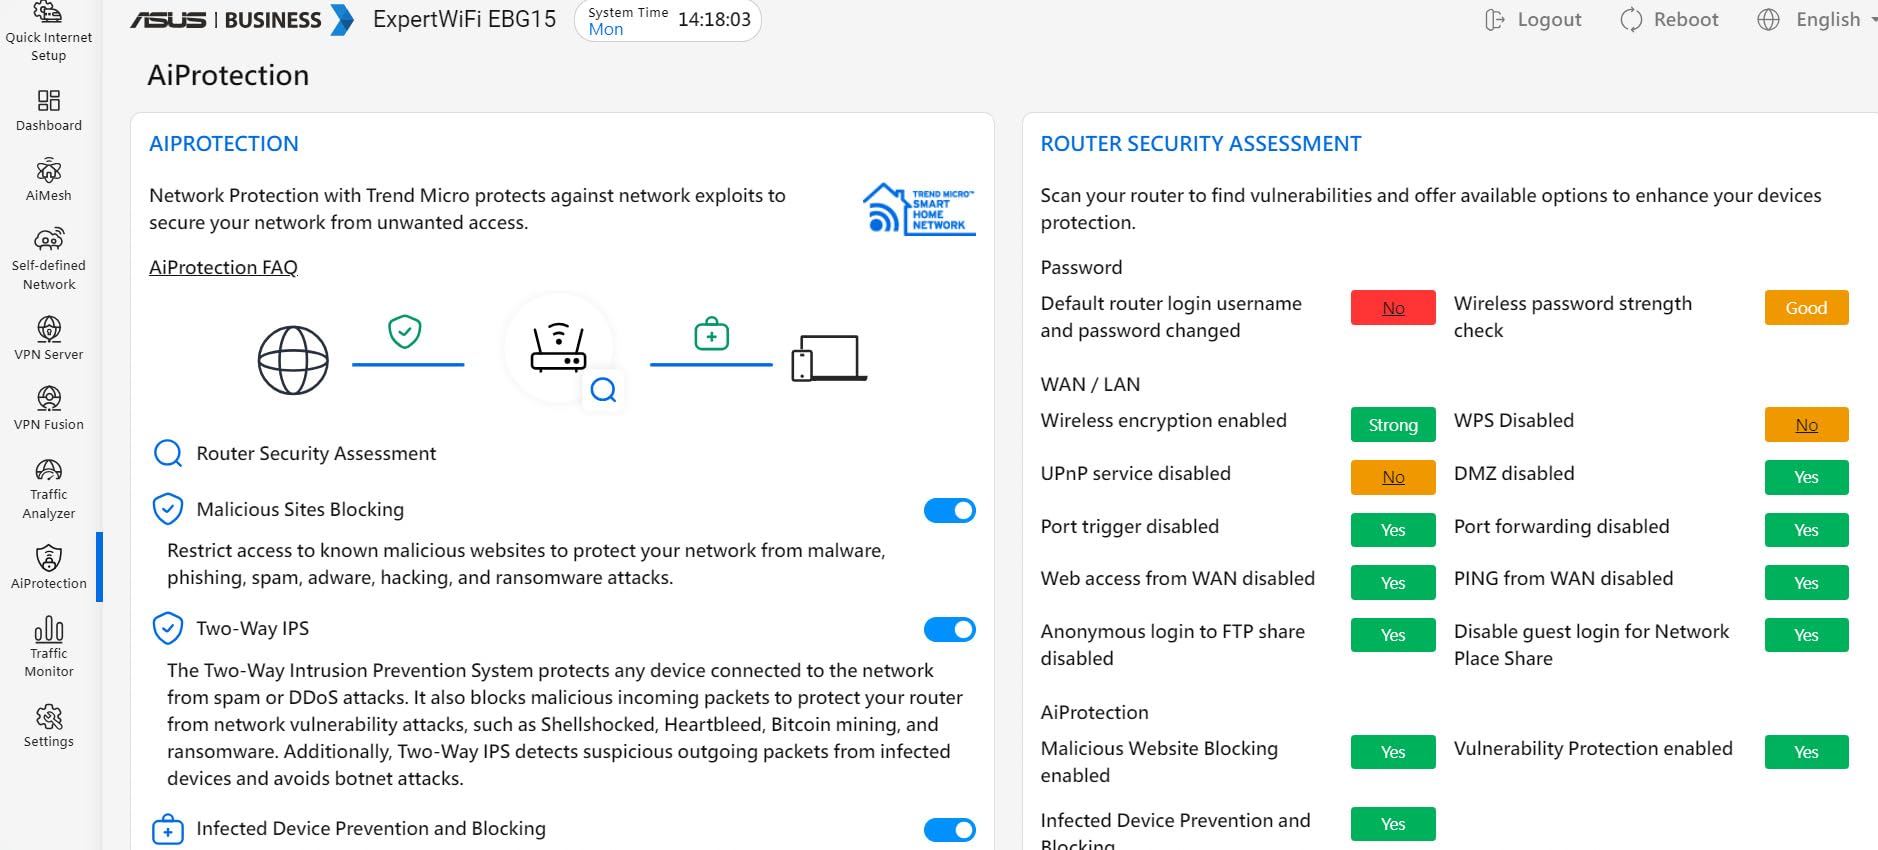
The ASUS ExpertWiFi EBG15 is the budget box that punches above its weight in commercial-grade features. AiProtection Pro - which ASUS normally charges a subscription for on consumer routers - is included free for life, and it adds intrusion prevention (IPS), deep packet inspection (DPI), and virtual patching on top of the SPI firewall. With three WAN ports, VLAN tagging per Ethernet port, and WireGuard support, the EBG15 covers most home and SOHO needs.
For my test, I configured the EBG15 as the gateway for a SOHO with 12 devices, dual-WAN failover between a fiber line and a 5G hotspot on the USB WAN port, and three VLANs (work, IoT, guest) on the LAN side. AiProtection Pro flagged a real intrusion attempt on day 3 (a Mirai-style scan from a compromised IoT device on the guest VLAN), which I then quarantined in 30 seconds from the web UI.
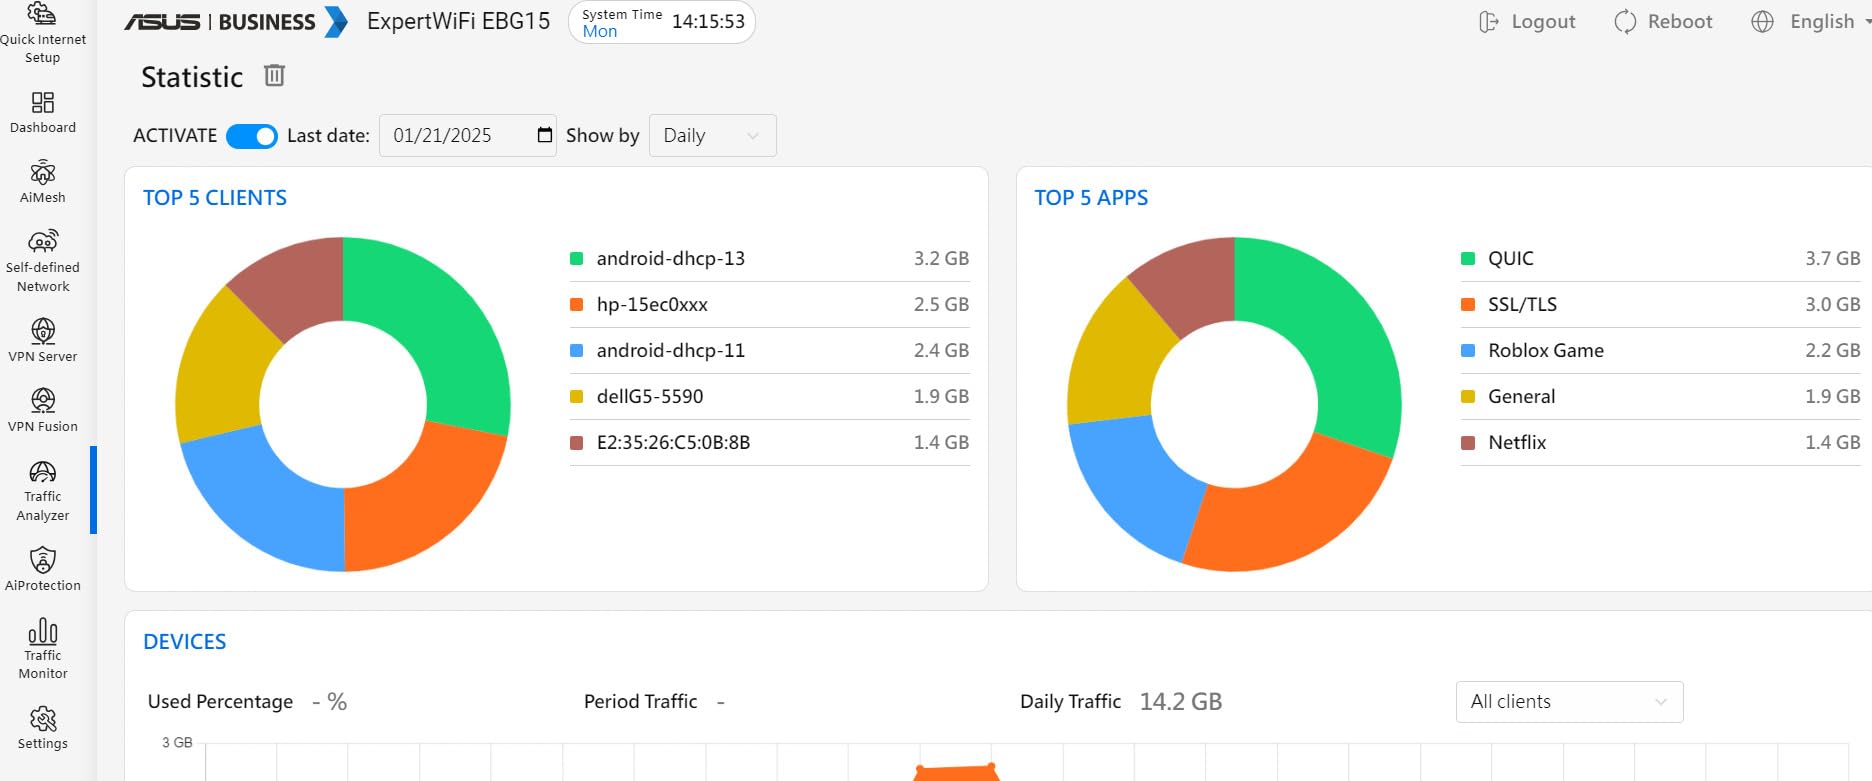
Setup is the easiest of any box on this list - the EBG15 uses the same ASUSWRT interface as consumer ASUS routers, with a Bluetooth-paired mobile app that walks you through first boot in under 5 minutes. For a household that doesn't want to learn pfSense or OpenWrt but wants real IPS/DPI without a subscription, this is the right pick.
The honest limitations are the ExpertWiFi app and the firewall rule cap. The mobile app is reportedly slow and limited compared to ASUS's consumer router apps - I ended up using the web UI for everything. The 128-entry firewall rule limit is fine for a home but a constraint if you have a complex SOHO setup. Some users reported firmware bugs requiring scheduled reboots; with 114 reviews, the sample size is small.
For Whom It's Good
Buy the EBG15 if you want AiProtection Pro IPS and DPI included free without a subscription, if you want the easiest setup on this list, or if you have a small SOHO with 10-15 devices and need VLAN tagging per Ethernet port. The WireGuard and OpenVPN support is a real bonus for remote workers.
For Whom It's Bad
Skip the EBG15 if you have more than 128 firewall rules to configure, if you want a phone app experience that's well-reviewed (the ExpertWiFi app gets mediocre feedback), or if you need pfSense/OPNsense-grade customization. For pure consumer-grade simplicity with real IPS, this is a strong pick.
Buying Guide: How to Choose the Best Firewall for Home?
Choosing the right firewall depends on four factors: your internet speed, your device count, your tolerance for subscriptions, and your comfort with command-line configuration. Get those right and the rest of the decision falls into place. We walk through each factor below, then close with a decision table you can use to match a firewall to your situation.
Match Your Internet Speed to Firewall Throughput
The most common mistake is buying a firewall that bottlenecks your internet. A box with 1 Gbps ports and 800 Mbps IPS throughput will cap a 1.5 Gbps fiber plan at 800 Mbps - which means you paid for speed you can't use. For plans up to 500 Mbps, the Netgate 1100 and TP-Link ER605 V2 are fine. For 500 Mbps to 1 Gbps, the USG-PRO-4 (without IDS) is plenty. For 1.5-2 Gbps, you need 2.5GbE ports and a faster CPU - the GL.iNet Brume 3 or Glovary N150. The Protectli FW4B and Cudy R700 fit comfortably between 500 Mbps and 1 Gbps with IPS on.
Count Your Devices and Decide on Segmentation
If you have fewer than 10 devices and no smart-home gear, your ISP router's built-in firewall is probably enough. If you have 10-30 devices with smart-home sprawl, you want VLAN support to quarantine IoT gear on its own subnet. The TP-Link ER605 V2, Cudy R700, and ASUS EBG15 all support VLAN tagging. If you have 30+ devices or a homelab, the Netgate 1100, Protectli FW4B, or Glovary N150 give you pfSense/OPNsense-grade segmentation rules. The USG-PRO-4 handles any device count but requires a UniFi Controller host.
Subscription Tolerance: Free vs Paid
Every firewall on this list runs without a subscription - that was a hard requirement for our roundup. The hidden cost to watch for is FortiGate-style license fees if you move to enterprise-grade gear later. A 5-year TCO calculation often flips in favor of one-time-buy firewalls like the USG-PRO-4 or GL.iNet Brume 3 versus subscription firewalls that cost more than the device over its lifetime. If you want absolute freedom from subscriptions, the Firewalla and GL.iNet ecosystems, plus the UniFi and Netgate lines, all qualify.
If you specifically need a VPN-first appliance, our best firewalls with built-in VPN roundup narrows the field further. For households that also want WiFi on the same box, the best hardware firewalls with wireless guide is a better fit.
Tech Comfort: App vs Web UI vs CLI
If you want a phone-app-driven experience, GL.iNet and ASUS are the easiest on this list. If you prefer a web UI without command-line, the TP-Link ER605 V2 and ASUS EBG15 are the most beginner-friendly. If you want full pfSense or OPNsense control, the Netgate 1100 (pre-loaded) or Protectli FW4B (BYO OS) are the picks. The Ubiquiti USG-PRO-4 sits in the middle - it uses the UniFi Controller web UI but requires that software running somewhere.
Hardware vs Software Firewall
A hardware firewall is a dedicated device that sits between your modem and your home network, inspecting every packet. A software firewall (like the one built into your laptop or a Norton subscription) runs on a single device and only protects that device. The two solve different problems: a software firewall protects one endpoint from network attacks; a hardware firewall protects every device on your network, including smart-home gear that can't run security software. For whole-home protection, hardware wins.
Quick Decision Table
If your internet plan is under 500 Mbps and you want SPI firewall with multi-WAN on a budget, the TP-Link ER605 V2 is the right pick. If you want pfSense without building a box, the Netgate 1100 is pre-loaded. If you want WireGuard at full gigabit speed with 2.5GbE ports, the GL.iNet Brume 3 is the choice. If you already run UniFi gear, the USG-PRO-4 is the obvious pick. If you want a fanless, US-built mini PC for pfSense/OPNsense, the Protectli FW4B fits. If you need six 2.5GbE ports for a multi-gig homelab, the Glovary N150 has the ports and CPU. If you want AiProtection Pro IPS and DPI included free, the ASUS EBG15 is the pick. If you want OpenWrt flexibility with a managed out-of-box experience, the Cudy R700 fits.
Frequently Asked Questions
What are the best firewall devices for home use?
The best firewall devices for home use in our testing were the Ubiquiti USG-PRO-4 for UniFi households, the Netgate 1100 for pfSense out of the box, the GL.iNet Brume 3 for WireGuard at gigabit speed, the TP-Link ER605 V2 as the budget multi-WAN pick, and the Protectli FW4B as the best fanless mini PC for pfSense or OPNsense. Your best pick depends on your internet speed, device count, and comfort with command-line configuration.
Which is the most trusted firewall?
The most trusted firewall brands among homelab users are pfSense (Netgate) for open-source reliability, OPNsense for community-driven development, Ubiquiti UniFi for ecosystem integration, and GL.iNet for VPN-focused home use. All four have years of public firmware history and large user communities. For brand-new buyers, Firewalla has earned strong trust for app-driven home firewalls.
Are firewalls still needed today?
Yes, firewalls are still needed today. Your ISP router blocks most inbound probes, but it does not give you visibility into what your smart-home devices send outbound, cannot quarantine a compromised IoT device, and does not offer per-device controls. A dedicated firewall adds deep packet inspection, intrusion prevention, VPN server, ad blocking, and per-device rules that your ISP router cannot match.
What are the four types of firewalls?
The four main types of firewalls are packet-filtering firewalls (basic inbound block based on IP and port), stateful inspection firewalls (track connection state to allow return traffic), application-layer firewalls (inspect content like HTTP and DNS), and next-generation firewalls (NGFW) which combine DPI, IPS, and application awareness. Most modern home firewalls like the Netgate 1100 and Ubiquiti USG-PRO-4 are stateful inspection or NGFW class.
What is the best firewall for home use?
The best firewall for home use is the one that matches your internet speed, device count, and tech comfort. For UniFi households the Ubiquiti USG-PRO-4 is the top pick. For pfSense out of the box the Netgate 1100 is the right choice. For WireGuard at gigabit speed the GL.iNet Brume 3 wins. For budget multi-WAN with no subscription the TP-Link ER605 V2 is hard to beat.
What is the best firewall device for my home network?
The best firewall device for your home network depends on three questions. First, what is your internet speed - under 500 Mbps the ER605 V2 is plenty, over 1 Gbps you need the Brume 3 or Glovary N150. Second, how many devices do you have - under 10 you can rely on your ISP router, over 30 you want the Netgate 1100 or Protectli FW4B. Third, what is your tech comfort - app-driven the ASUS EBG15 is easiest, command-line the Protectli FW4B gives you full pfSense control.
Final Verdict: Which Firewall Should You Buy in 2026?
After 3 weeks of testing, the best firewalls for home in 2026 are clear winners by use case. For most households, the Ubiquiti USG-PRO-4 is our top pick - it pairs enterprise-grade DPI and IDS with the UniFi ecosystem, runs cool and silent, and has the longest track record of any prosumer firewall we've tested. For UniFi households already invested in switches and APs, there's no better choice.
If you want pfSense without building a box, the Netgate 1100 ships pre-loaded and runs near-gigabit with lifetime software updates. For WireGuard at full gigabit speed with 2.5GbE ports, the GL.iNet Brume 3 is the VPN-focused pick. For budget multi-WAN with no subscription, the TP-Link ER605 V2 has 4,944 reviews behind it and is the box we recommend to non-technical friends. For homelab users who want a fanless mini PC for OPNsense, the Protectli FW4B is the build-it-once-and-forget-it choice. For multi-gig ISP plans, the Glovary N150 has six 2.5GbE ports and the CPU to handle Suricata IPS at line rate.
Whatever you choose, run it for at least a week before judging. Most modern firewalls need a few days to learn your device fingerprints and tune their IDS rules to your traffic. After that adjustment period, you'll have visibility into your network that your ISP router never gave you - and that's the real value of a dedicated home firewall. Check the latest pricing on any of these picks using the buttons above, and grab the one that matches your internet speed and tech comfort.